Quick answers
- Is CVE-2026-8262 exploited in the wild?
- No. Junglewise Threat Intelligence has no report of CVE-2026-8262 being exploited in the wild.
- How severe is CVE-2026-8262?
- Low severity, with a CVSS score of 2.4, published 11 May 2026.
- Which products and versions are affected?
- Devs Palace ERP Online up to 4.0.0.
- Is there a fix for CVE-2026-8262?
- No fixed version is recorded yet. Check the vendor's advisory in the references below. If you run it, Junglewise drafts a mitigation that fits your setup and applies it once you approve, with senior security engineers behind it.
- How is CVE-2026-8262 attacked?
- It is attacked over the network, in a web application.
- Am I affected by CVE-2026-8262?
- Check whether you run Devs Palace ERP Online at an affected version. Junglewise does that check for you around the clock: connect your code, cloud and domains, and it matches new vulnerabilities like this one against what you actually run and tells you when one reaches you.
Technical details
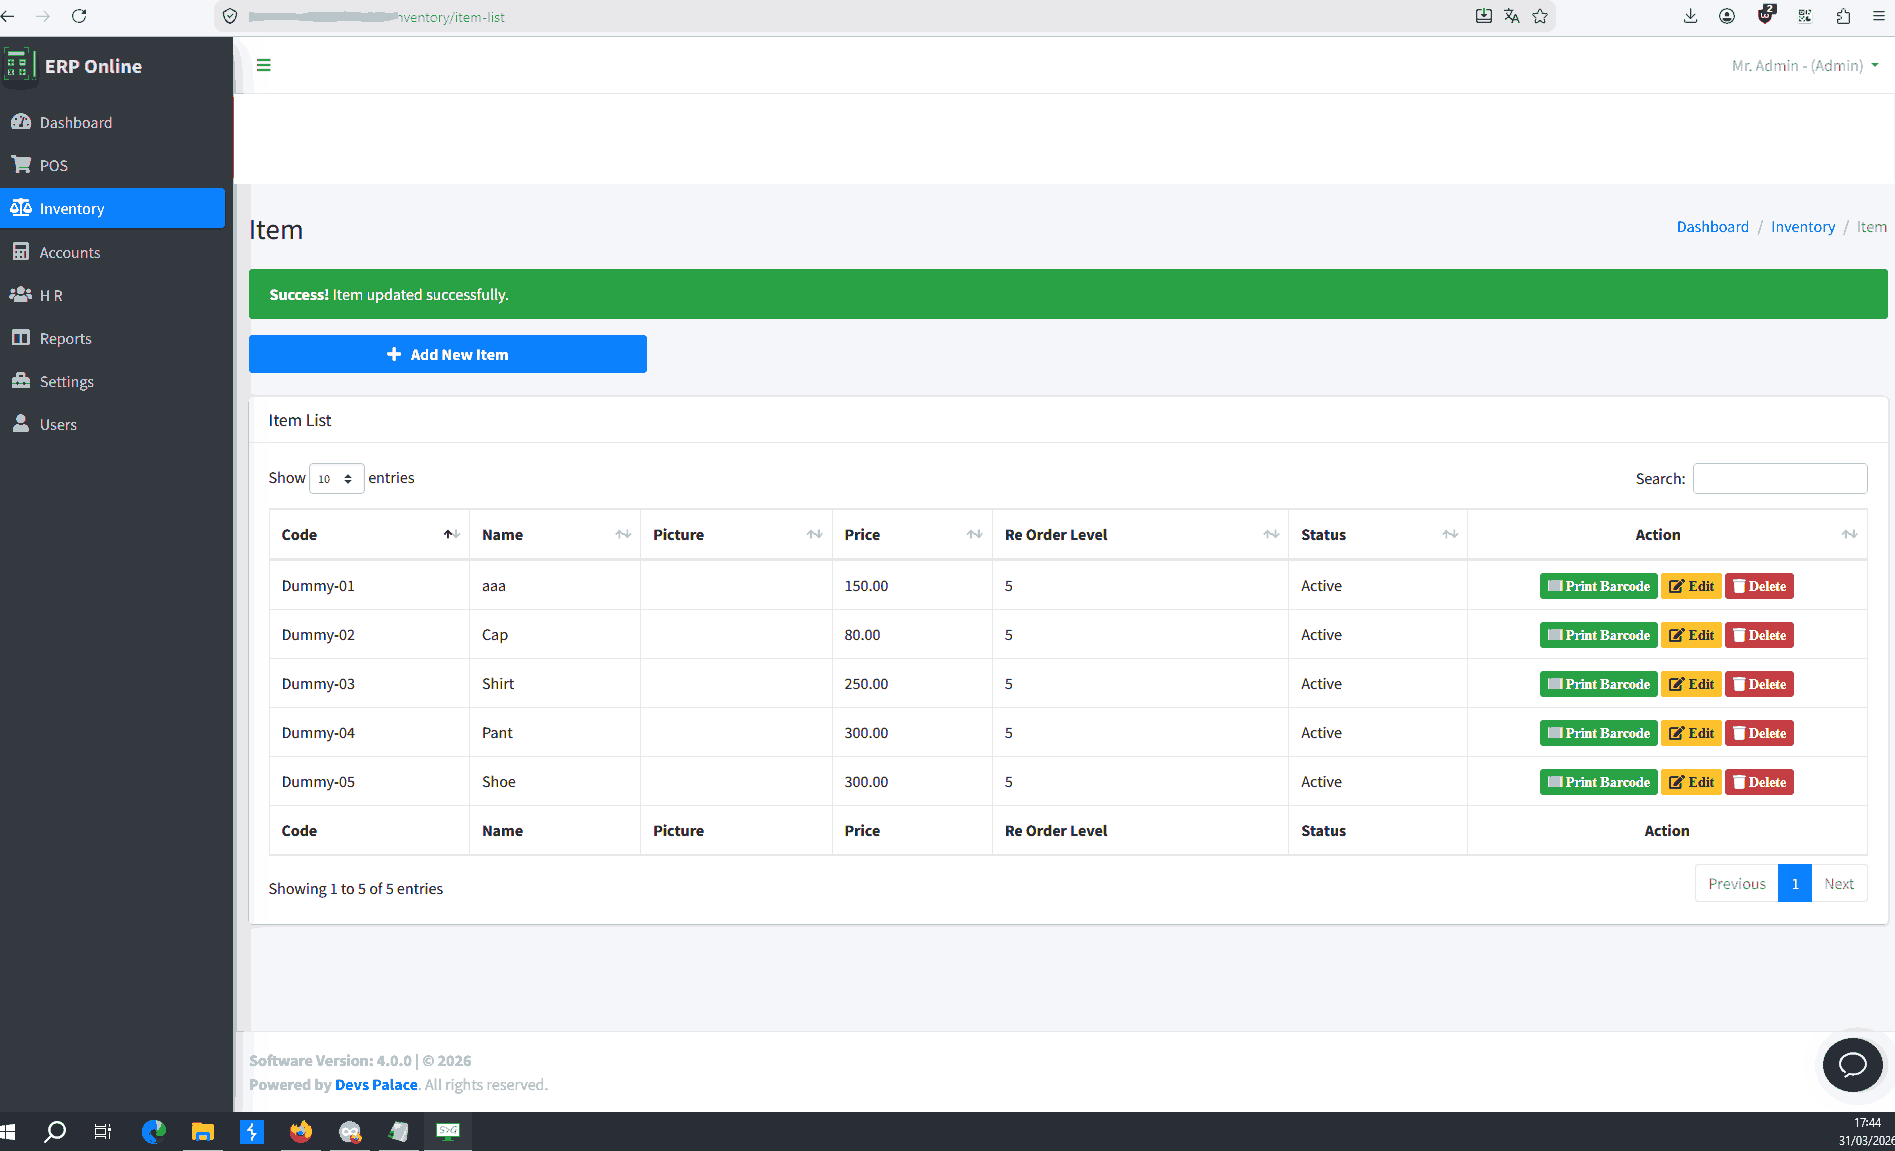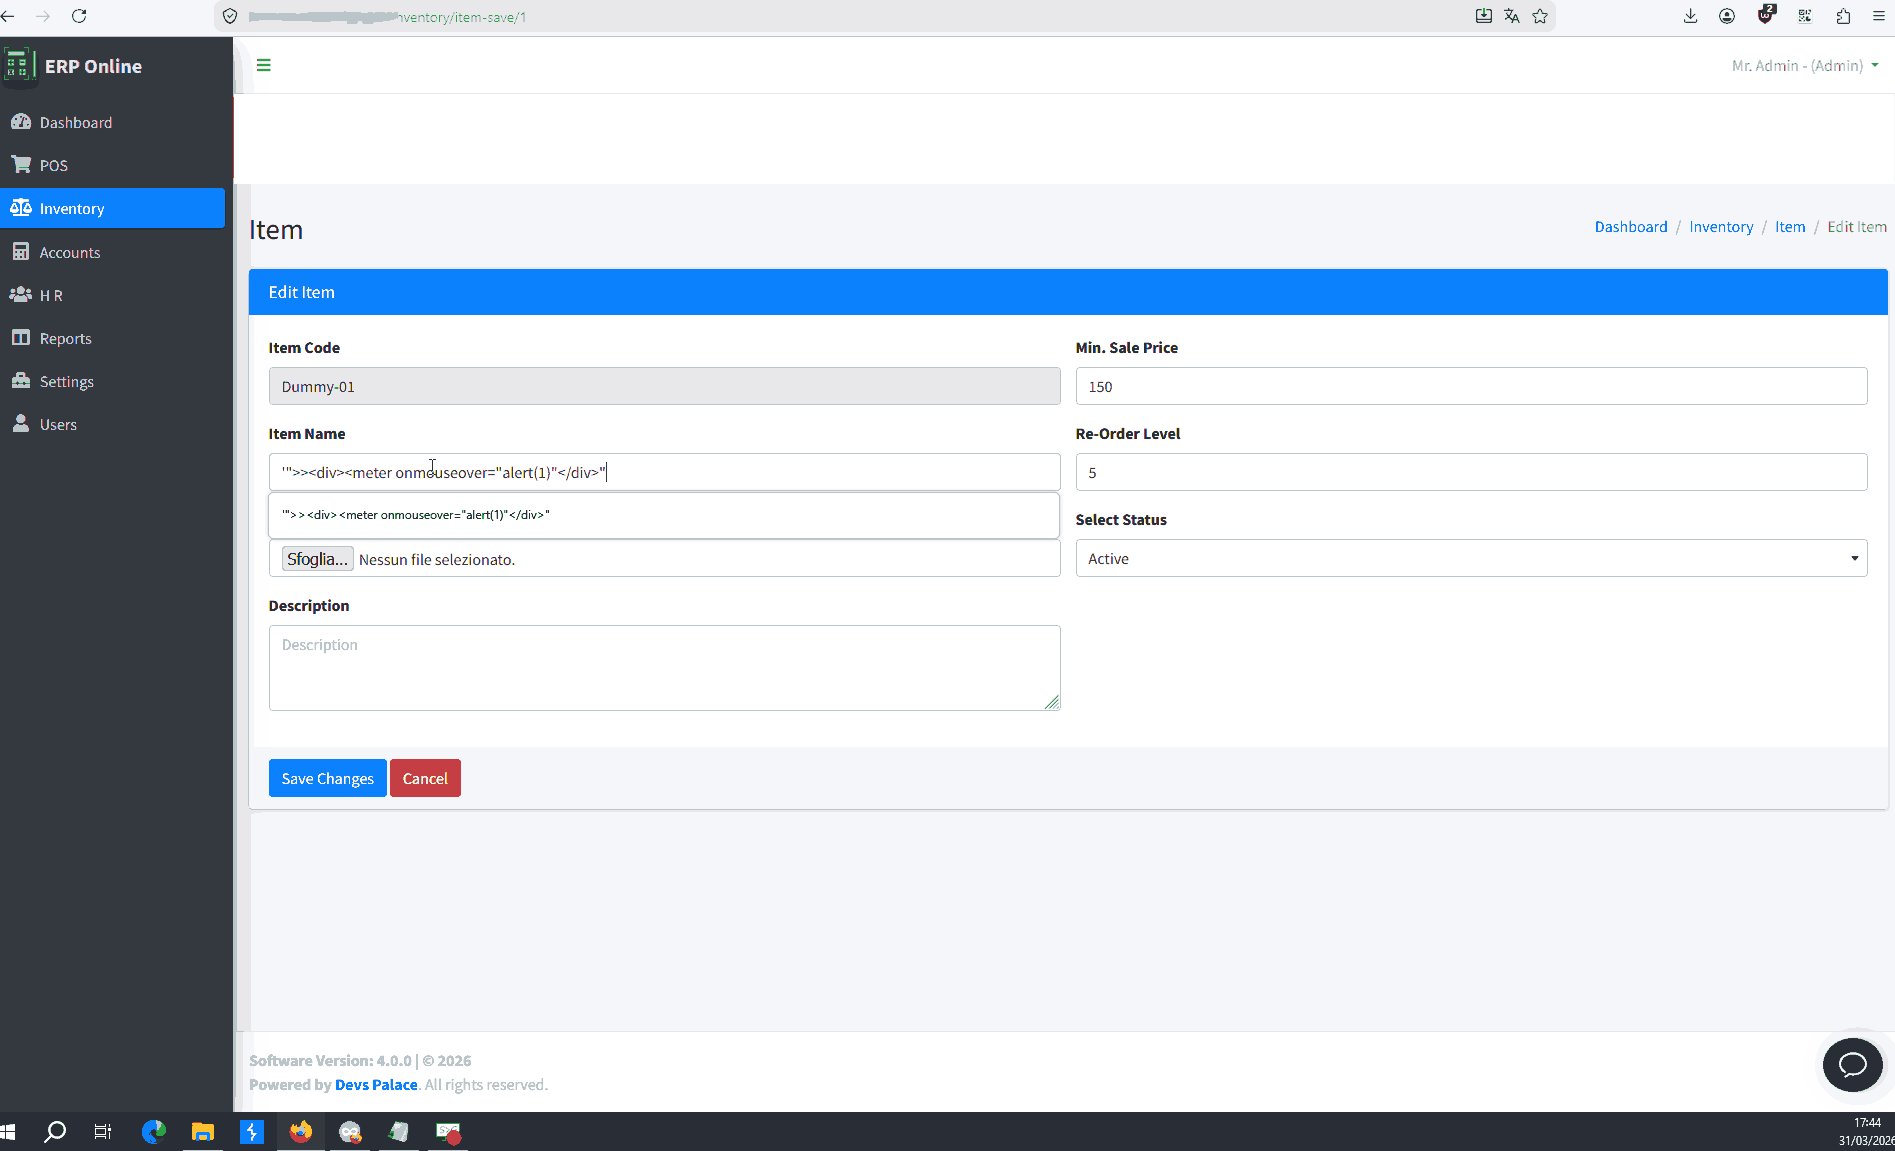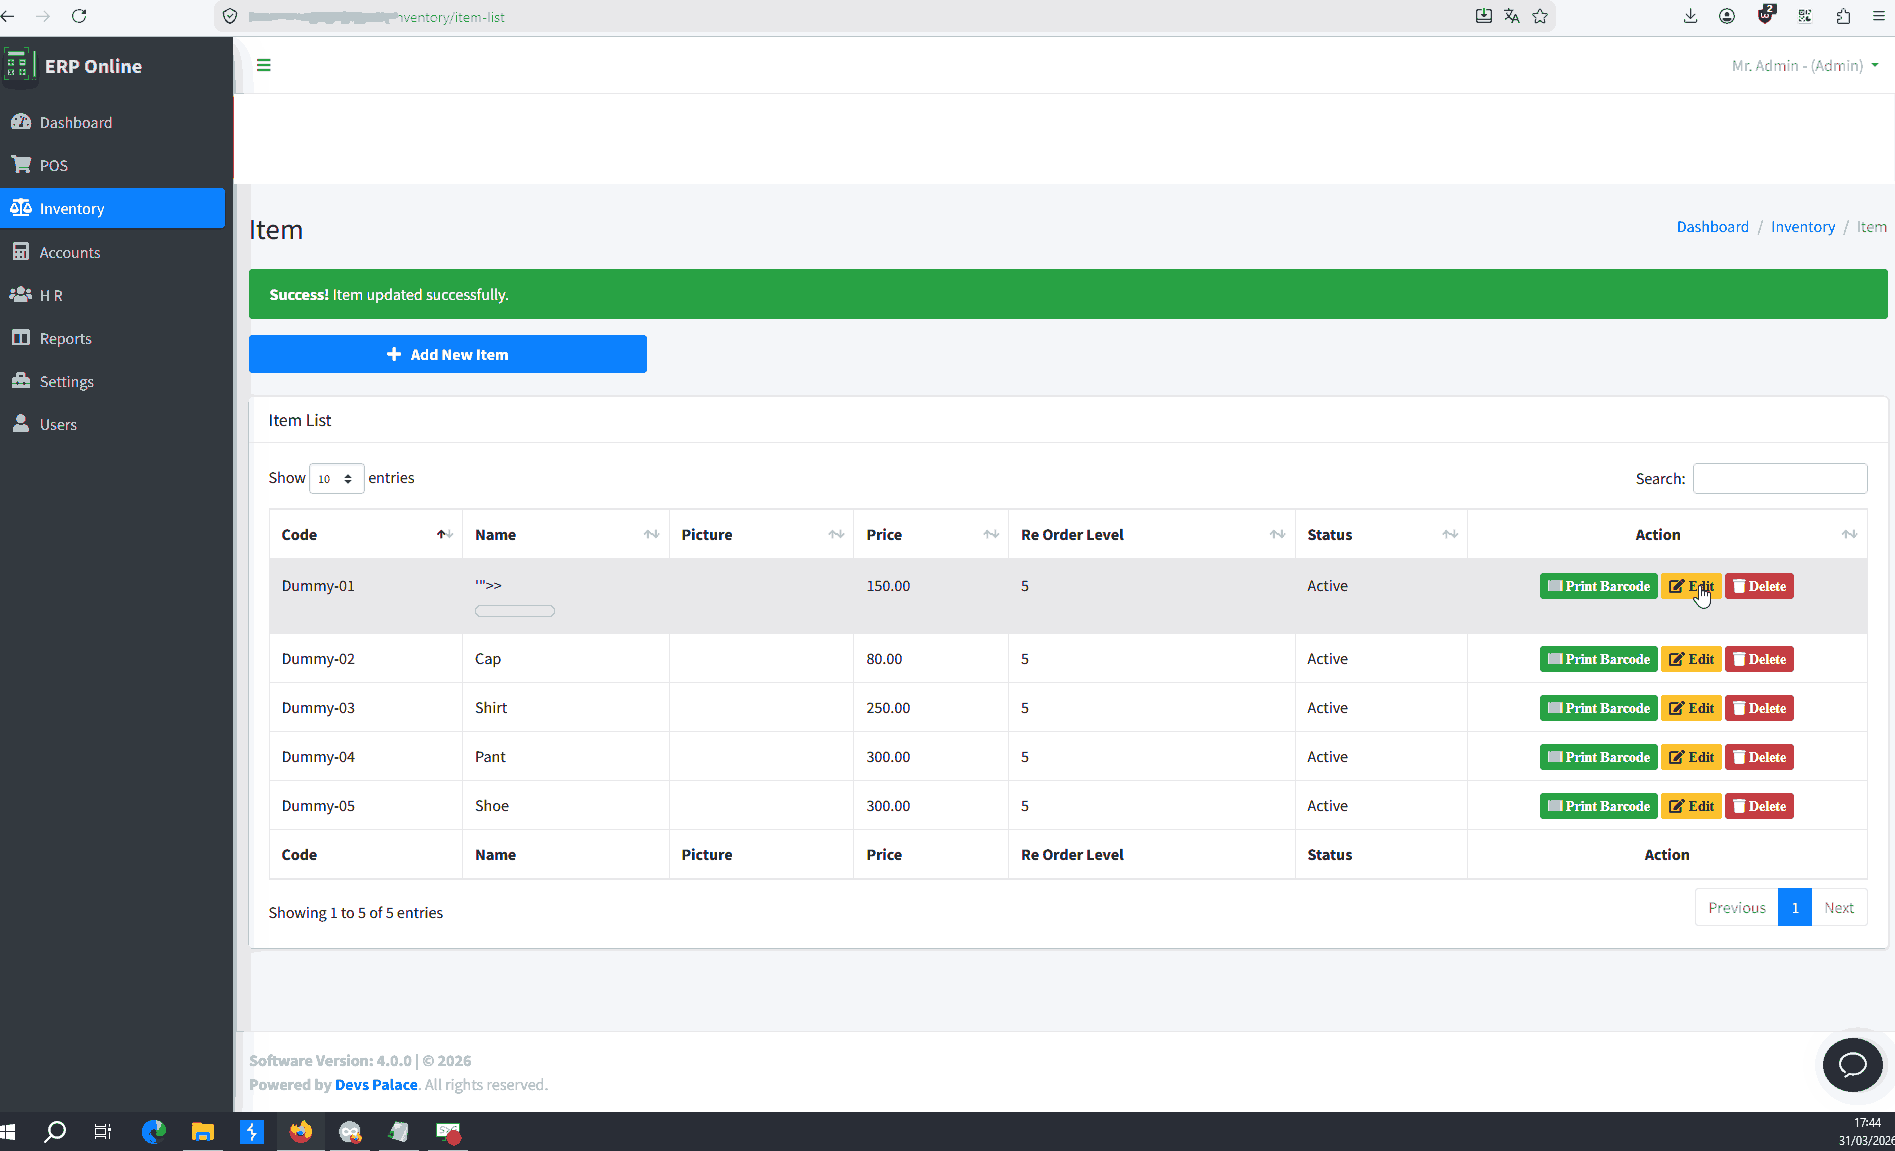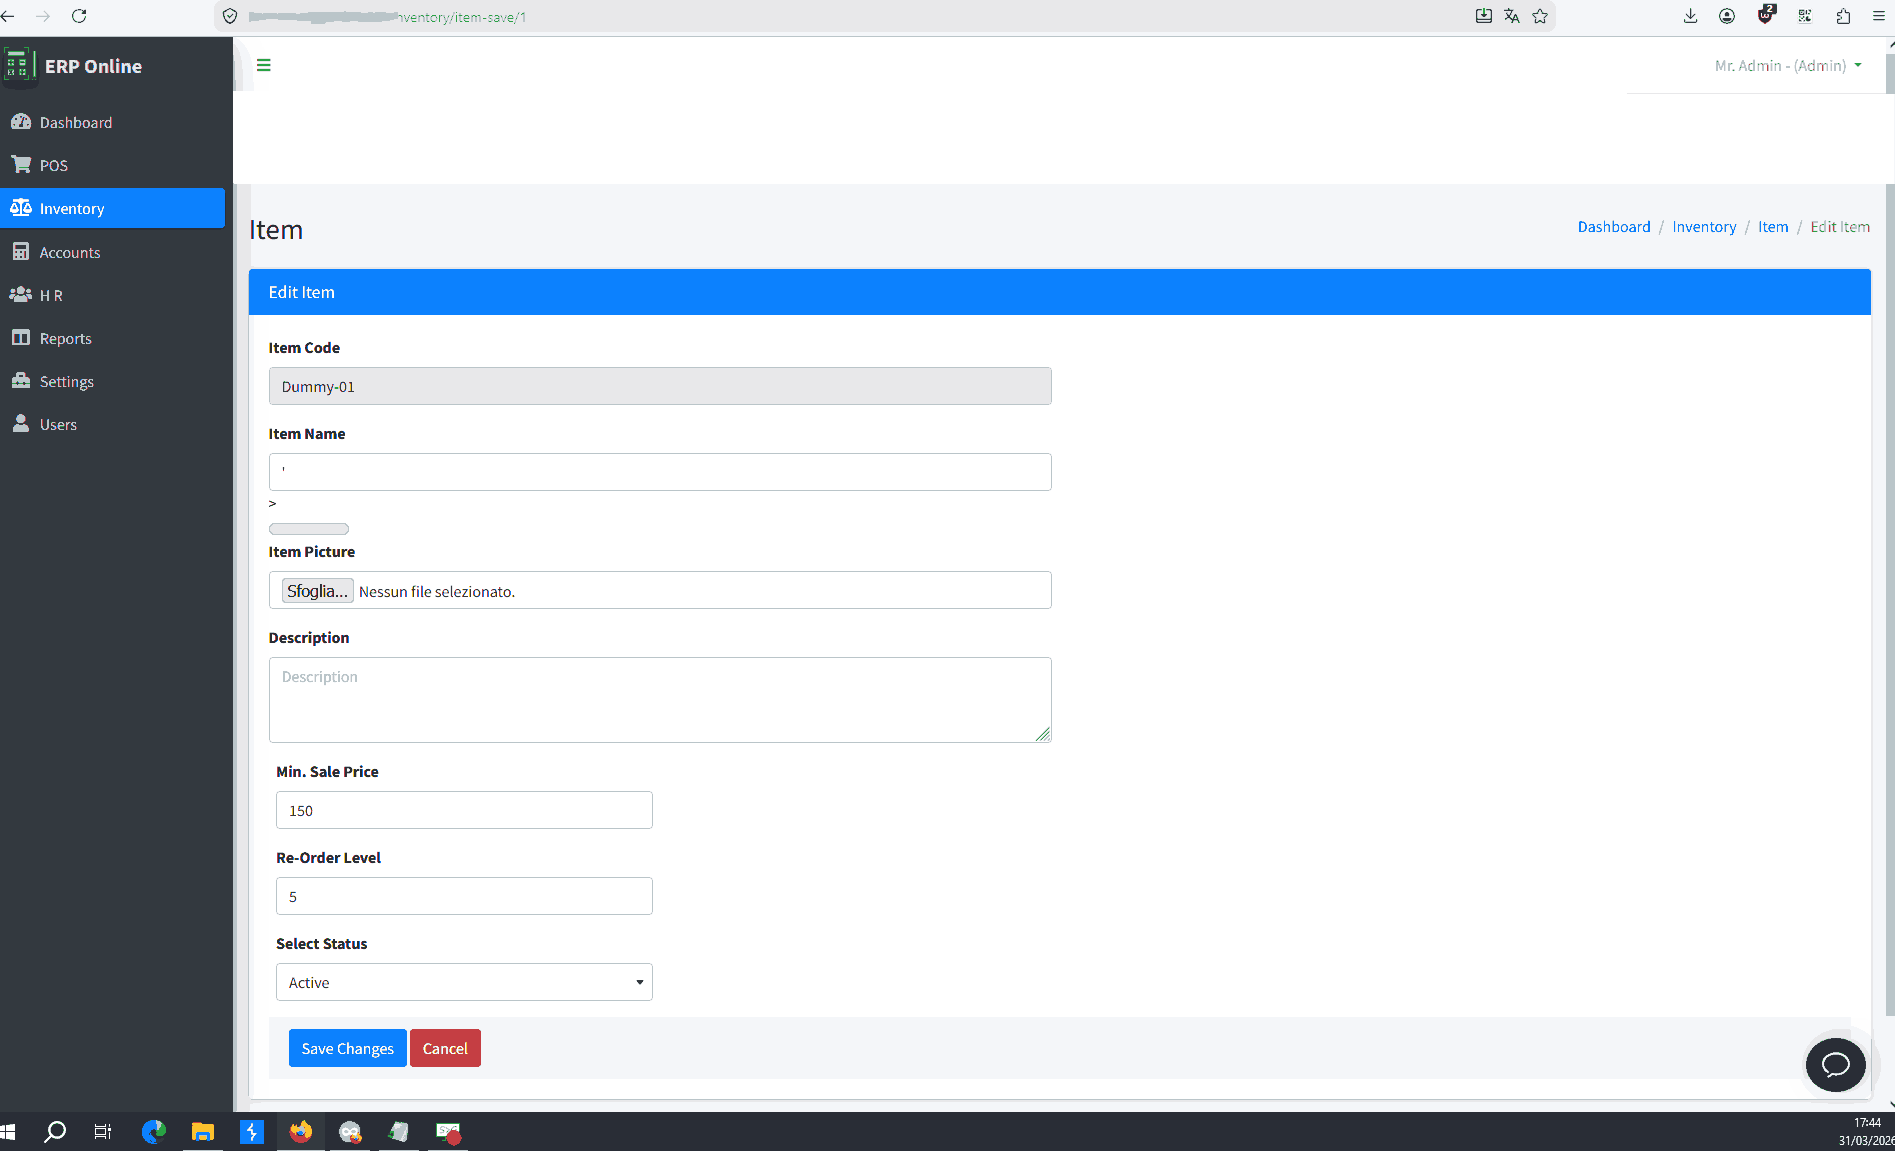
A stored cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online up to version 4.0.0. The flaw is located within the /accounts/chart-save file, where improper input neutralization allows for the injection of malicious web scripts. An attacker requires high privileges (PR:H) and network access to exploit this vulnerability. Successful exploitation requires a victim to interact with the manipulated page (UI:R), at which point the script executes in the context of the victim's session. A public proof-of-concept exists, and the vendor has reportedly not responded to disclosure attempts.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-11: disclosed: Initial public disclosure via VulDB and NVD
- 2026-05-11: advisory