Executive brief
Devs Palace ERP Online, a business management platform, contains a security vulnerability in its inventory management module. An attacker could exploit this flaw to inject malicious scripts into the application, potentially leading to unauthorized actions or data manipulation within a user's session. While the risk is mitigated by the requirement for high-level administrative privileges, a public exploit is currently available.
Technical details
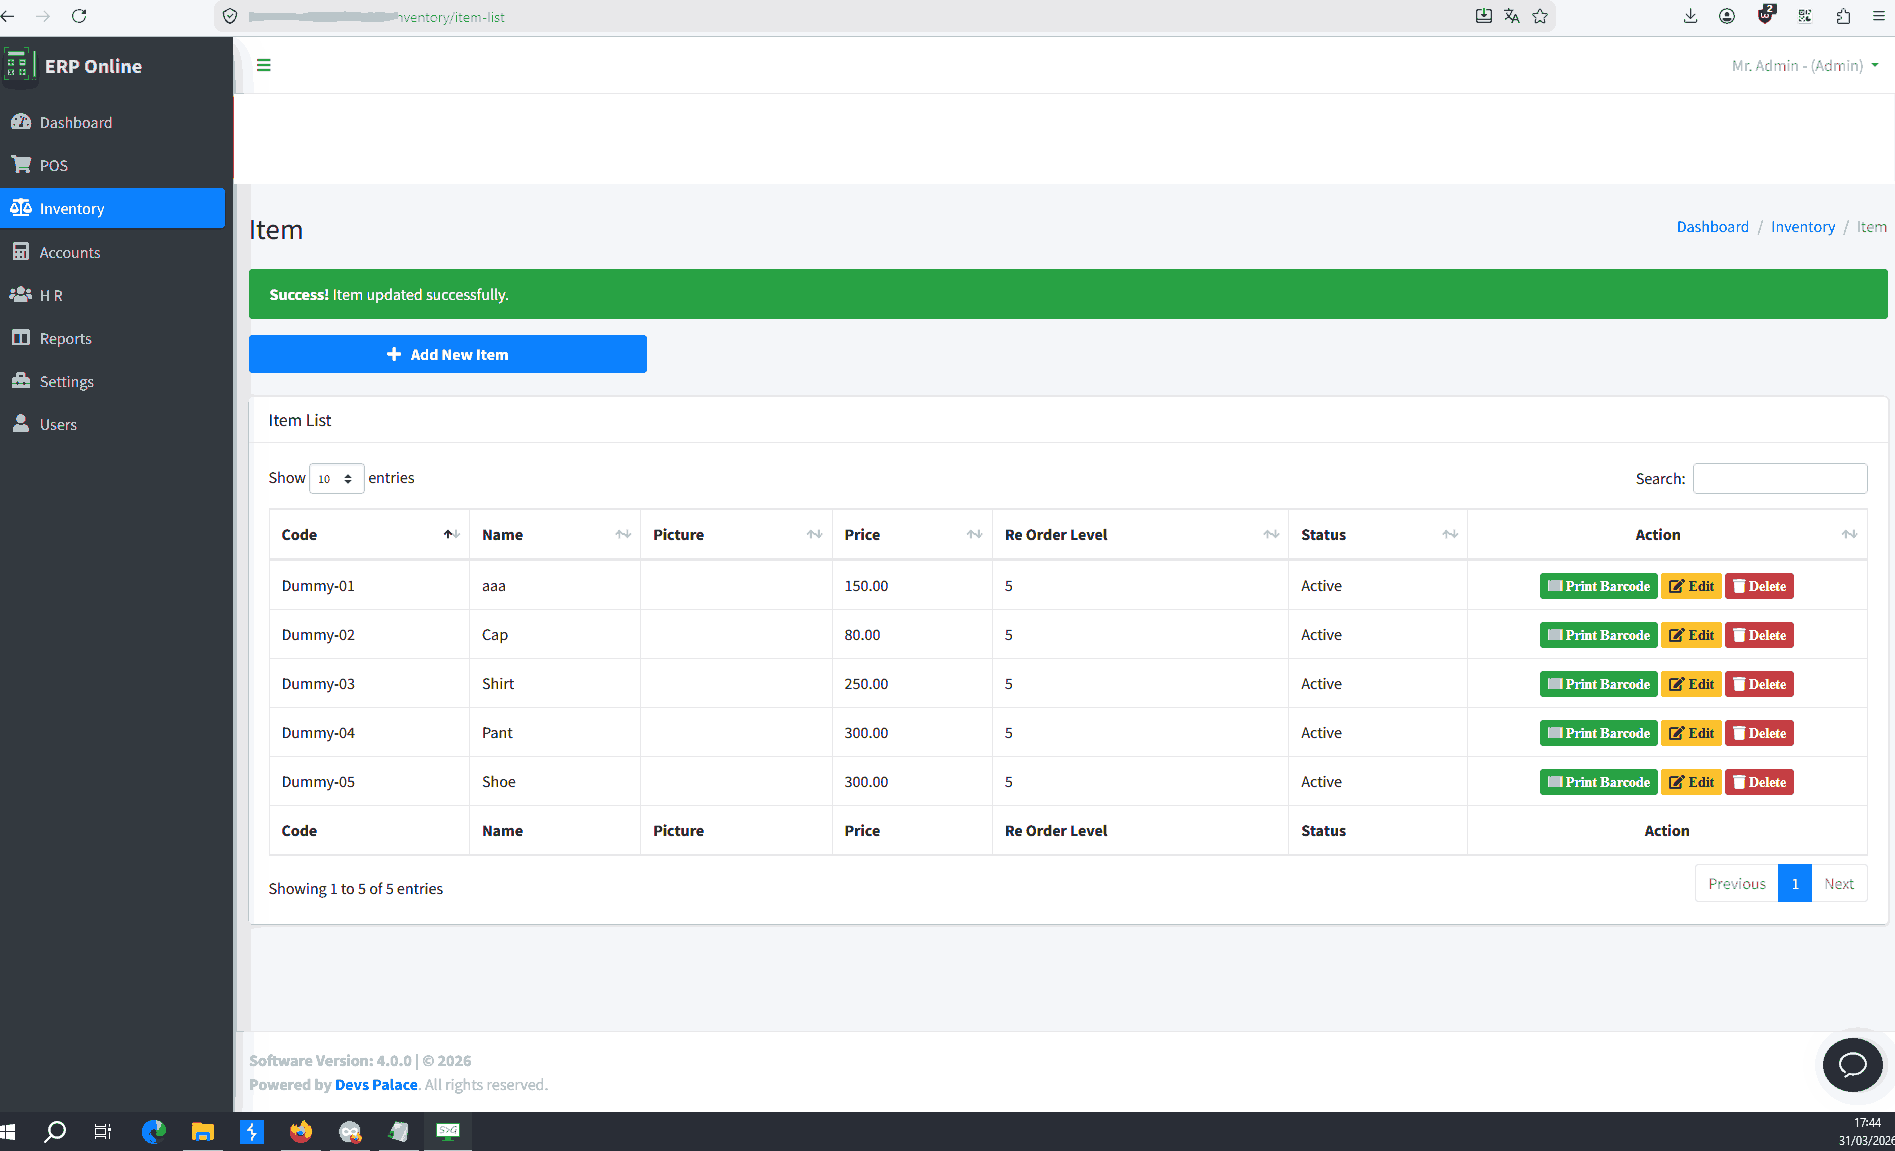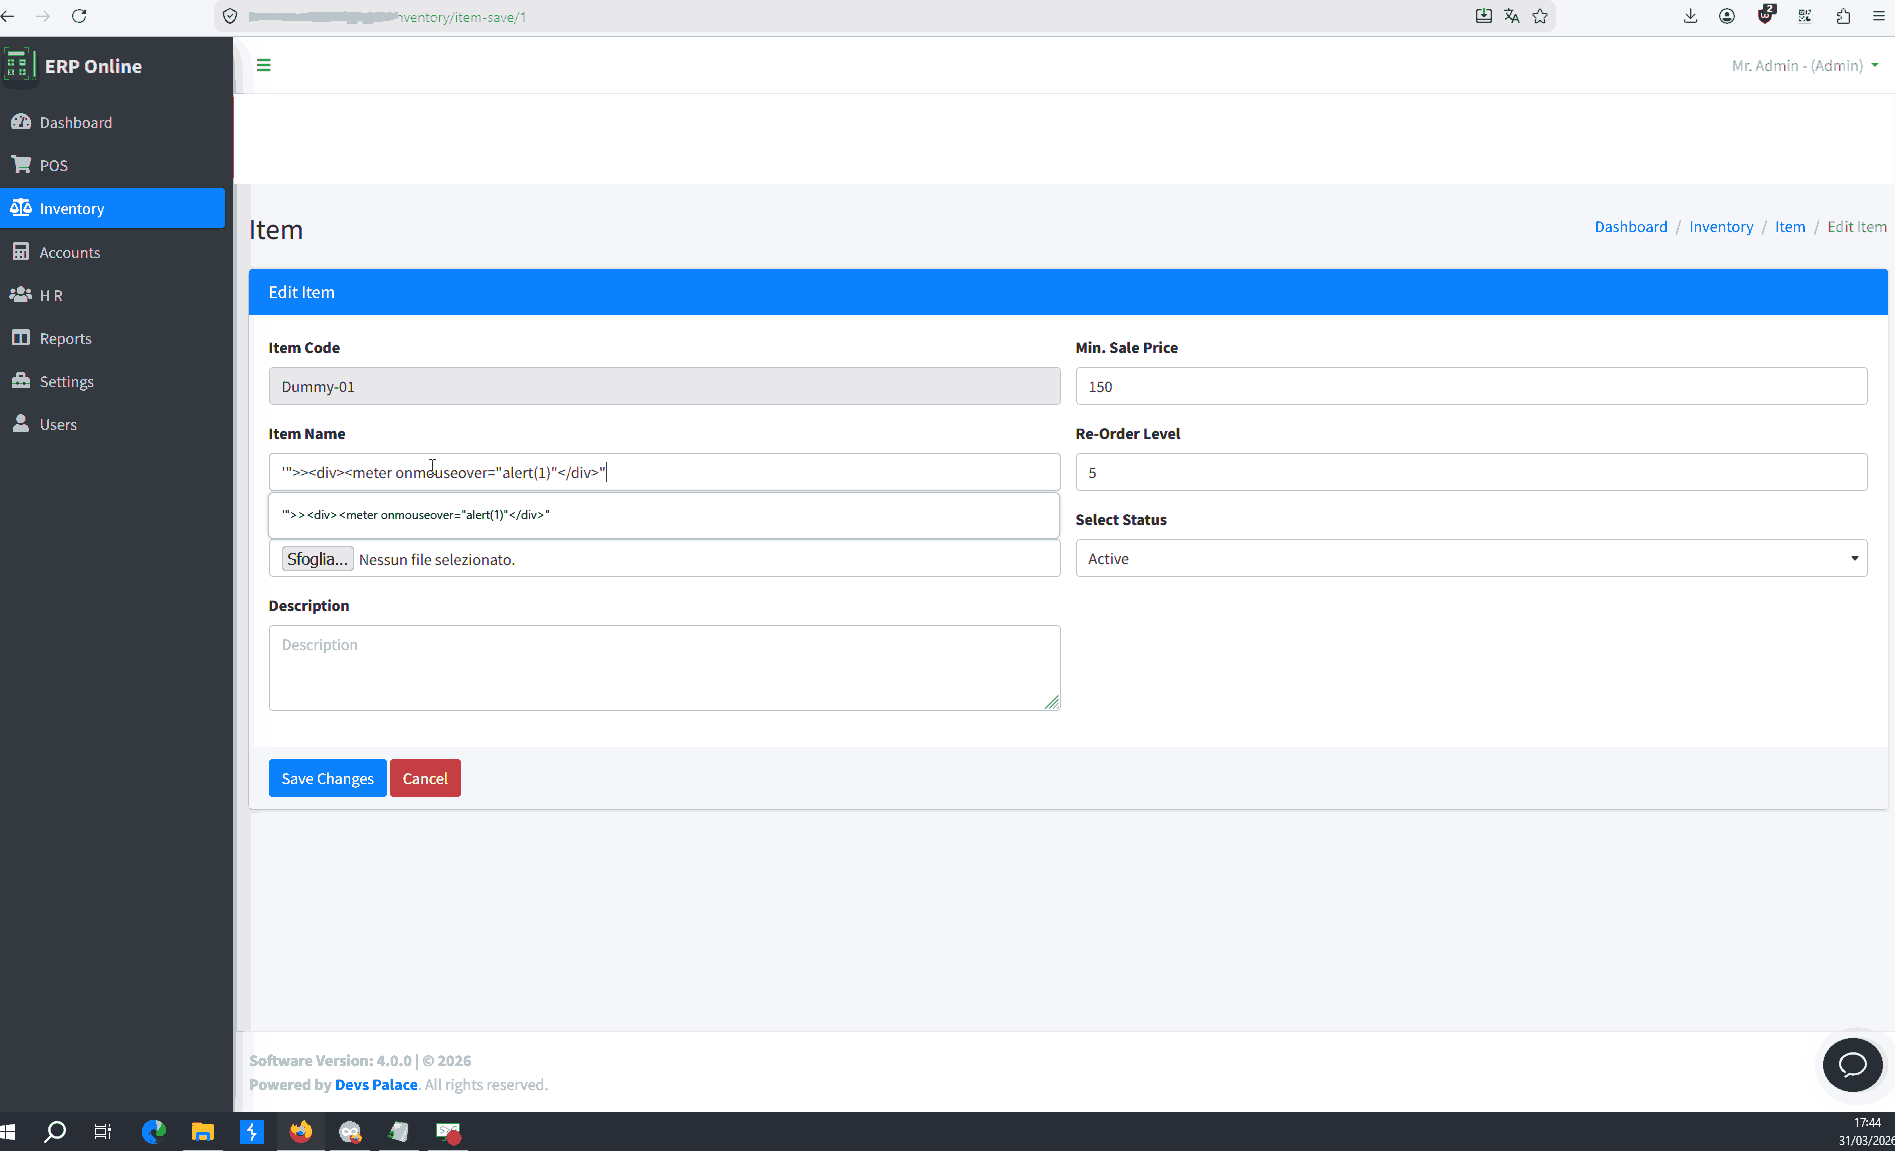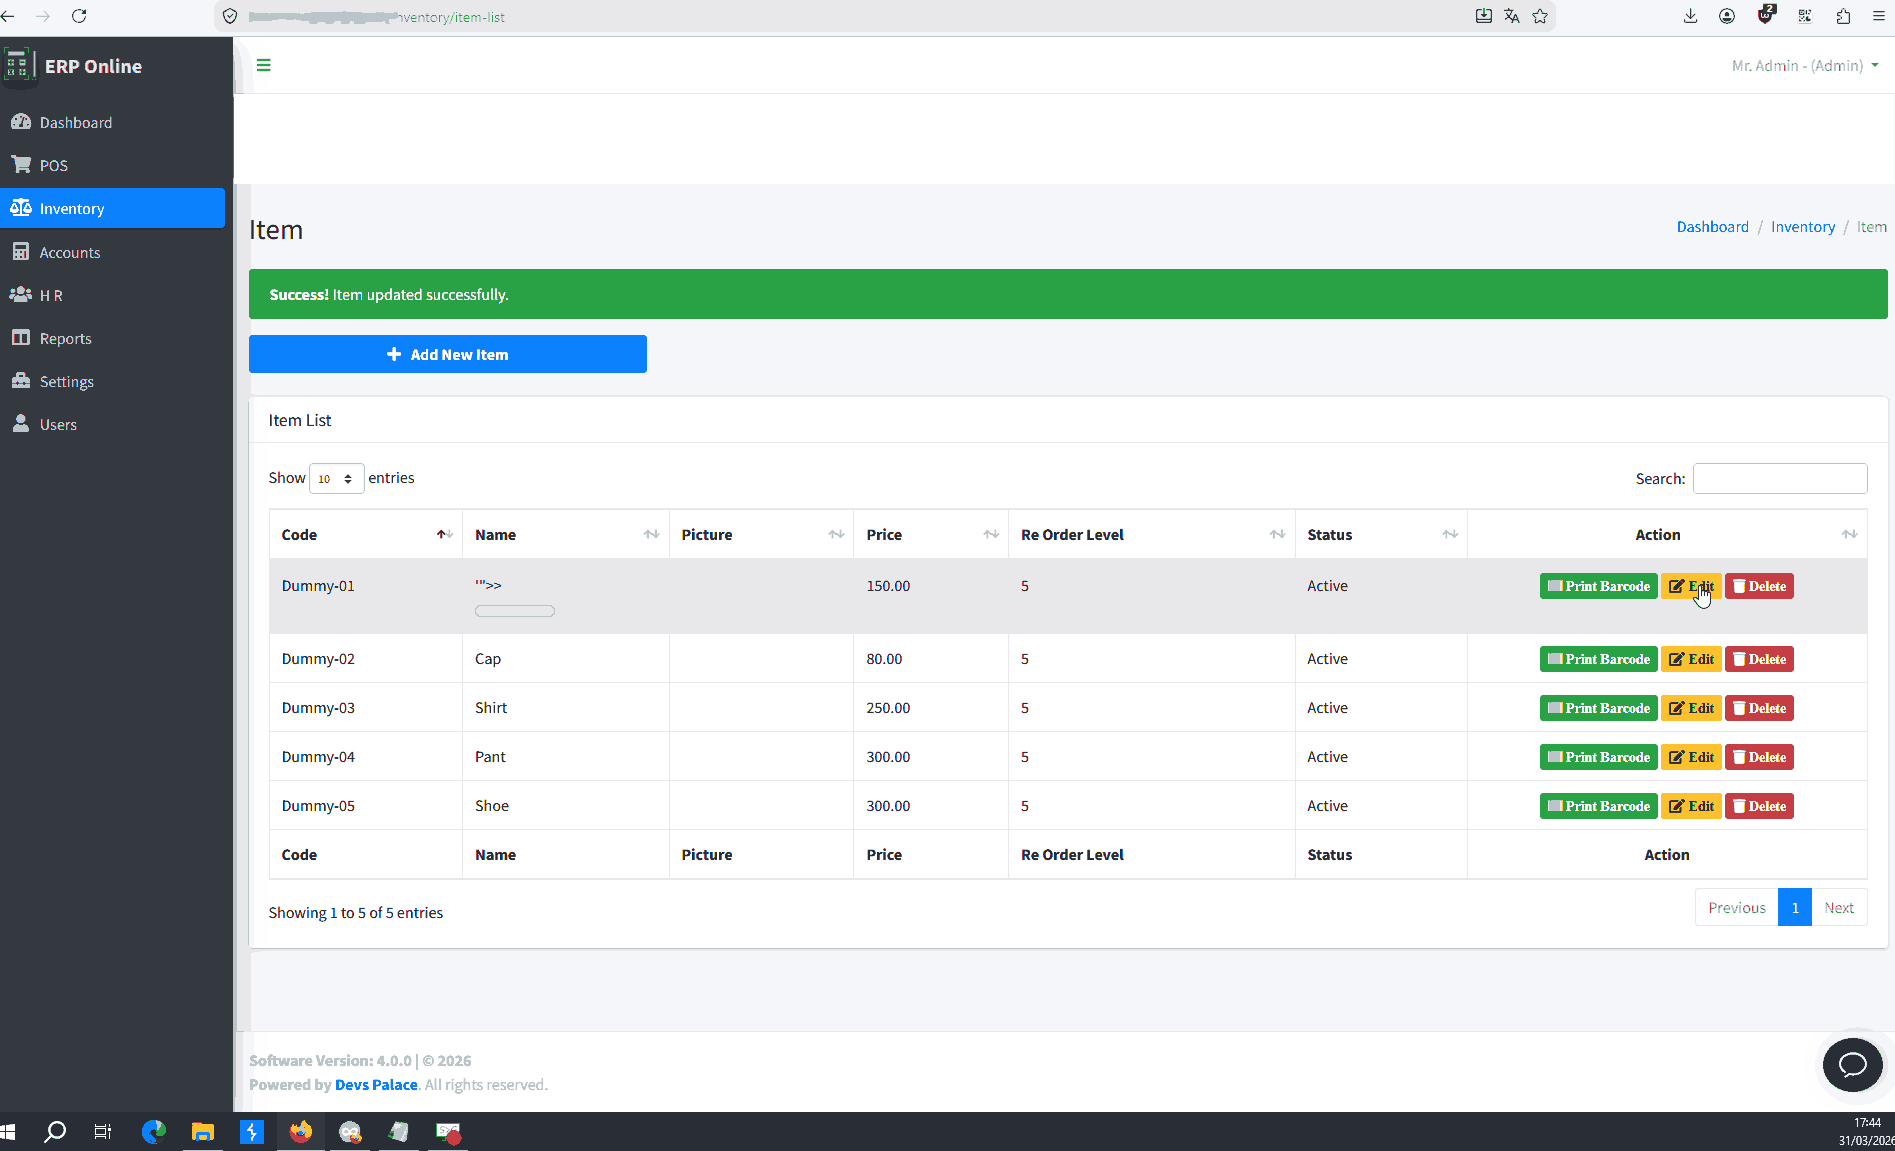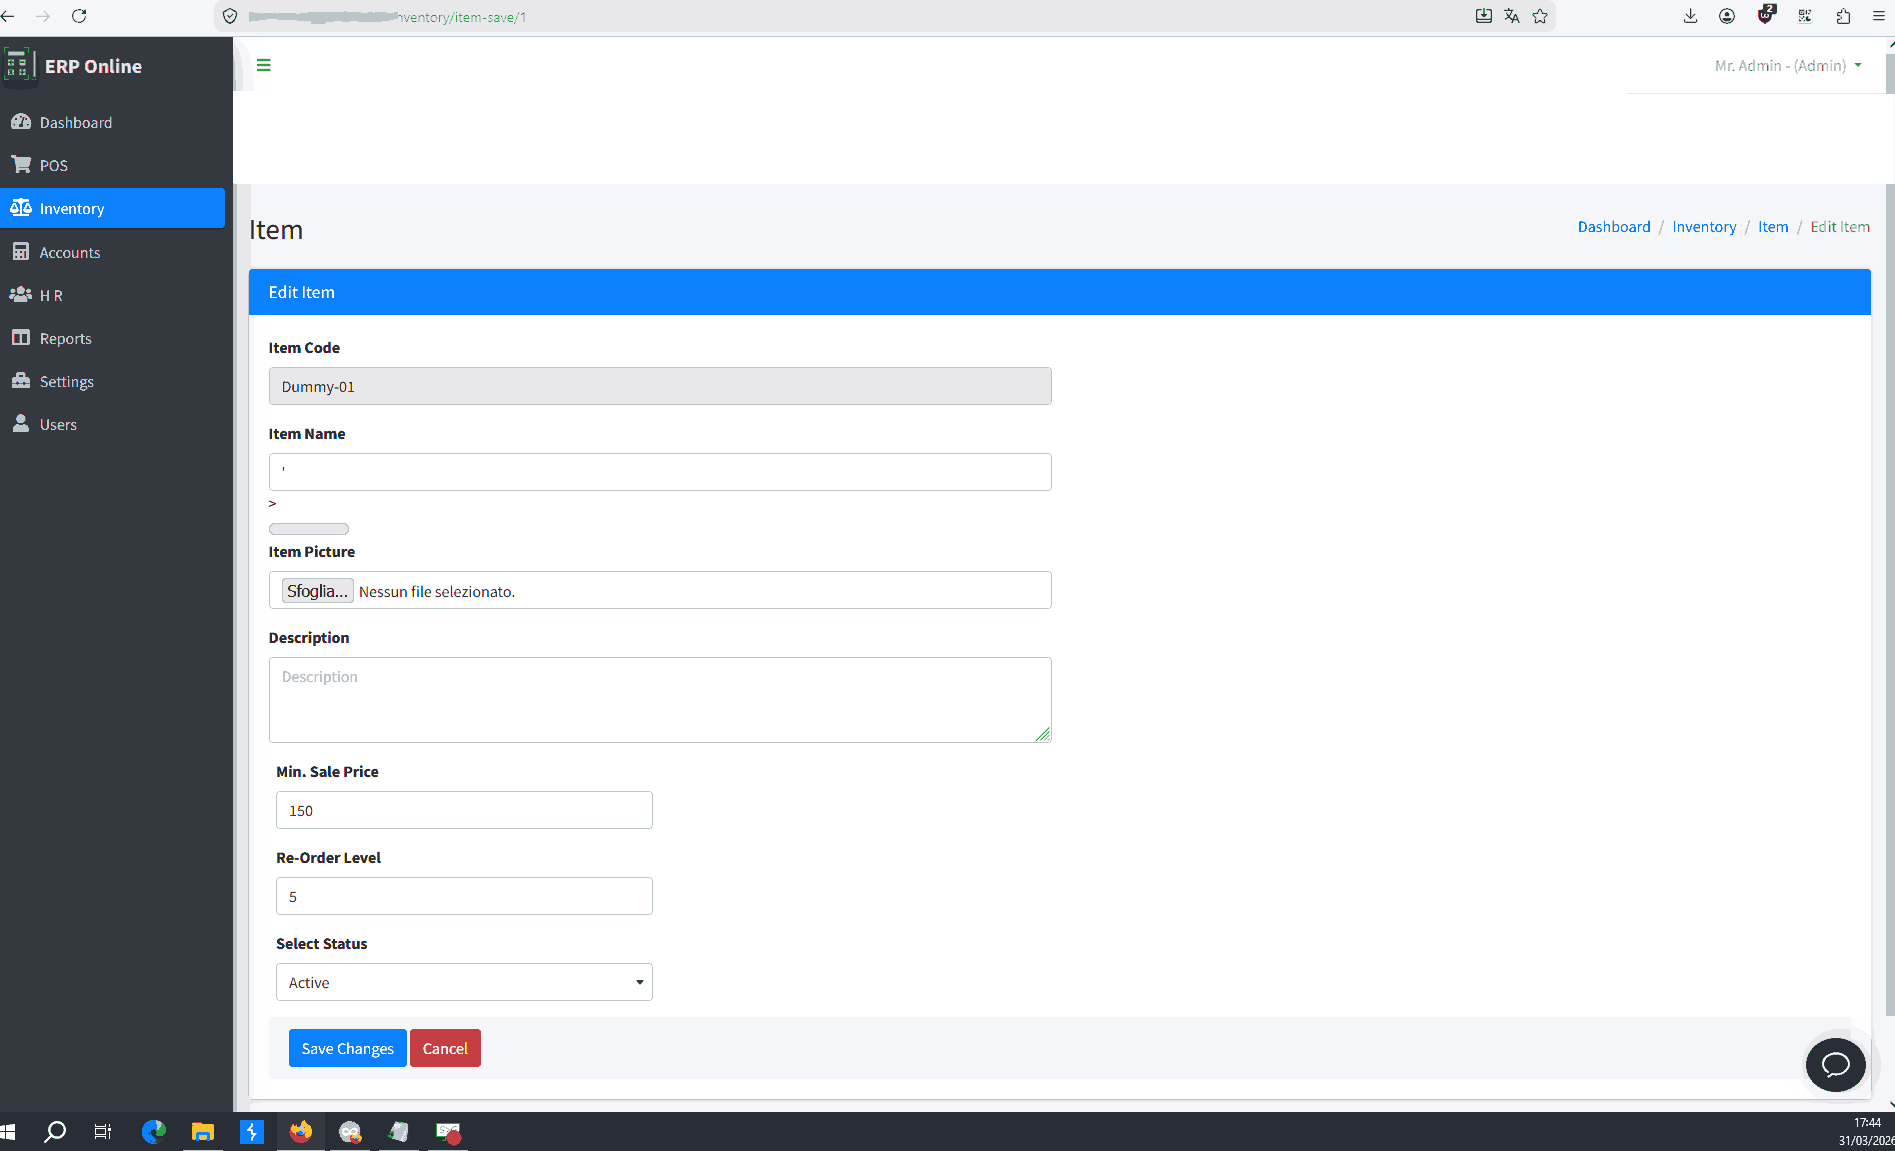
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online up to version 4.0.0 within the /inventory/sales_save file. The flaw stems from improper neutralization of input during web page generation (CWE-79) and potential code injection (CWE-94). An attacker with high-level privileges (PR:H) can remotely exploit this vulnerability, though it requires interaction from another user (UI:R). Successful exploitation allows the execution of arbitrary JavaScript in the context of the victim's browser session. A public proof-of-concept exploit has been released, and the vendor has reportedly not responded to disclosure attempts.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-11: advisory: NVD publication date
- 2026-05-11: disclosed: Public disclosure of the exploit code