Executive brief
Devs Palace ERP Online, a business management software suite, contains a security vulnerability in its customer management module. An attacker could use this flaw to execute malicious scripts in the browser of an authorized user, potentially leading to unauthorized actions or data manipulation within the application. While the risk is mitigated by the requirement for high-level administrative privileges, a public exploit exists and the vendor has not yet released a fix.
Technical details
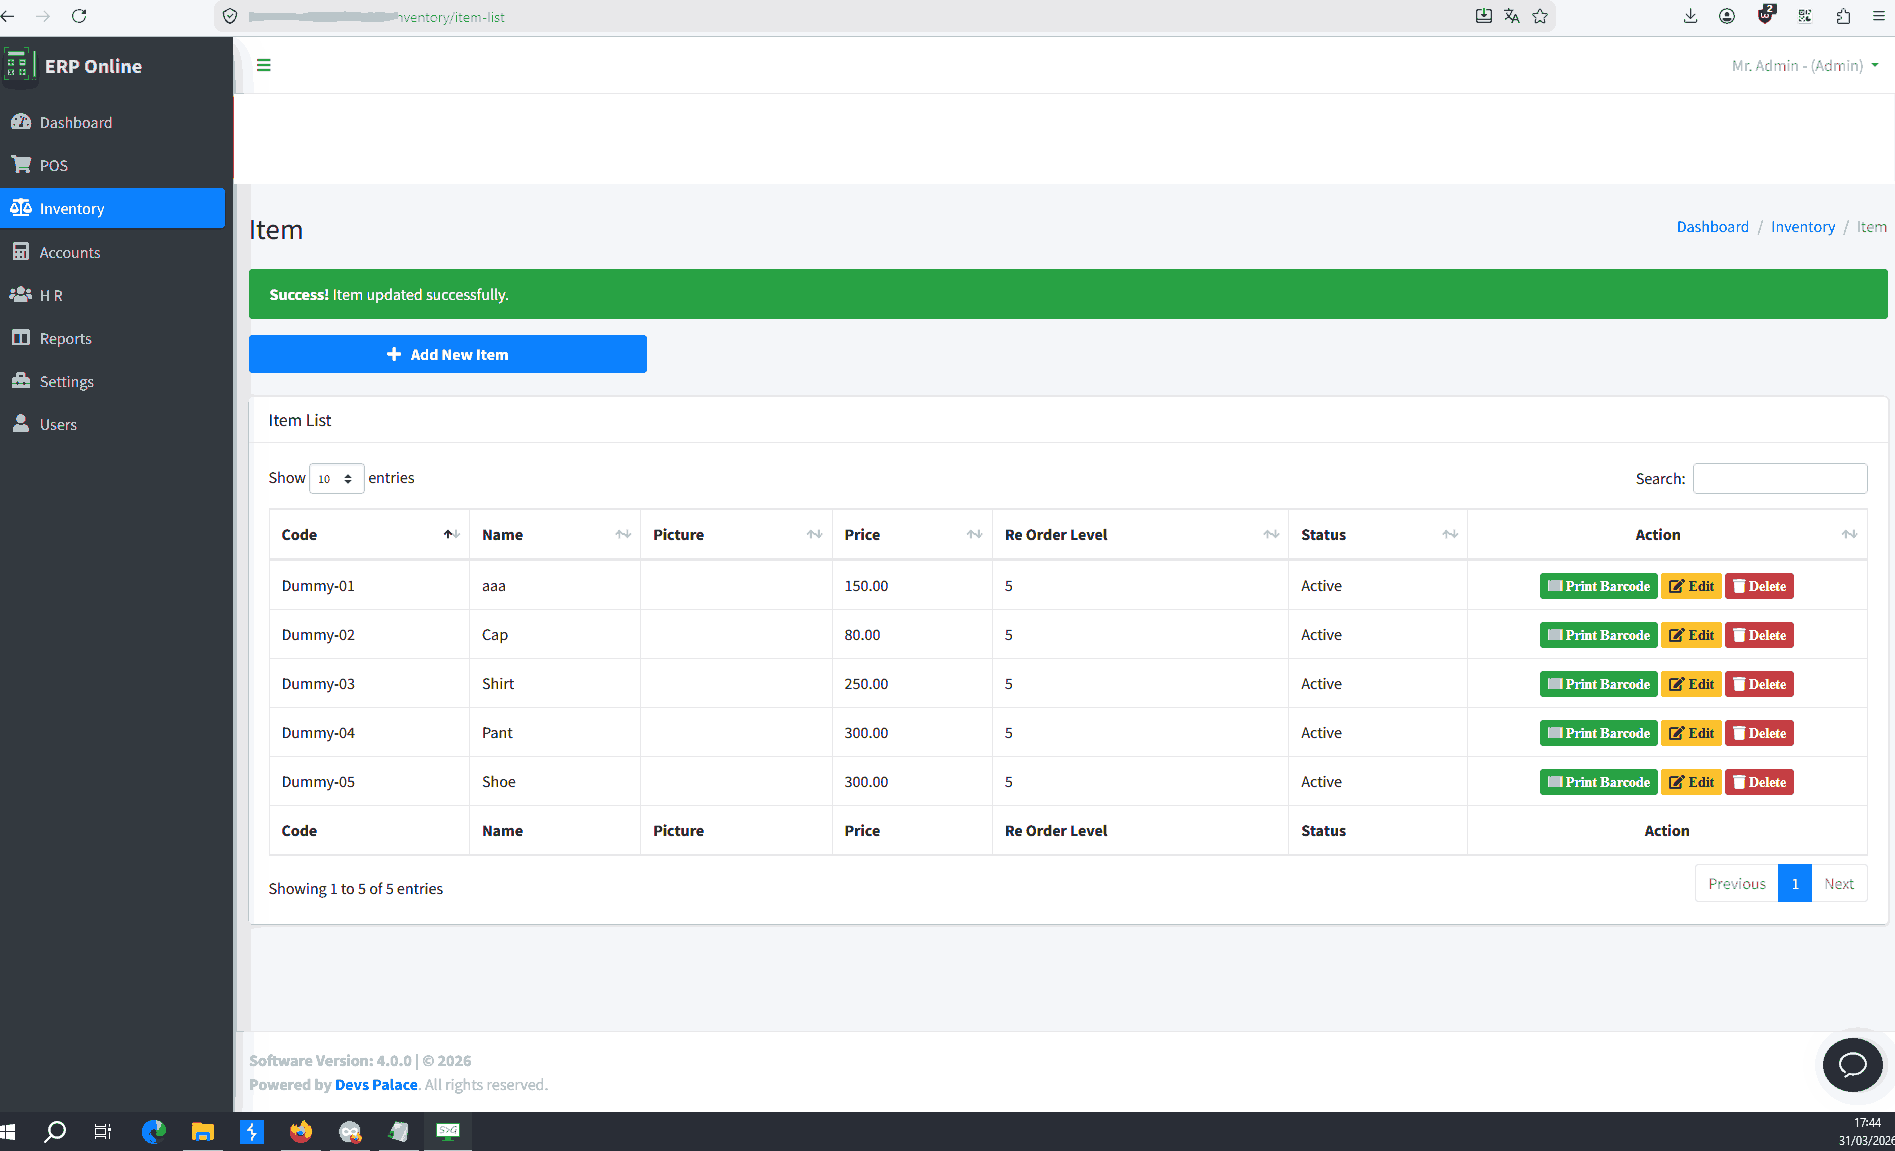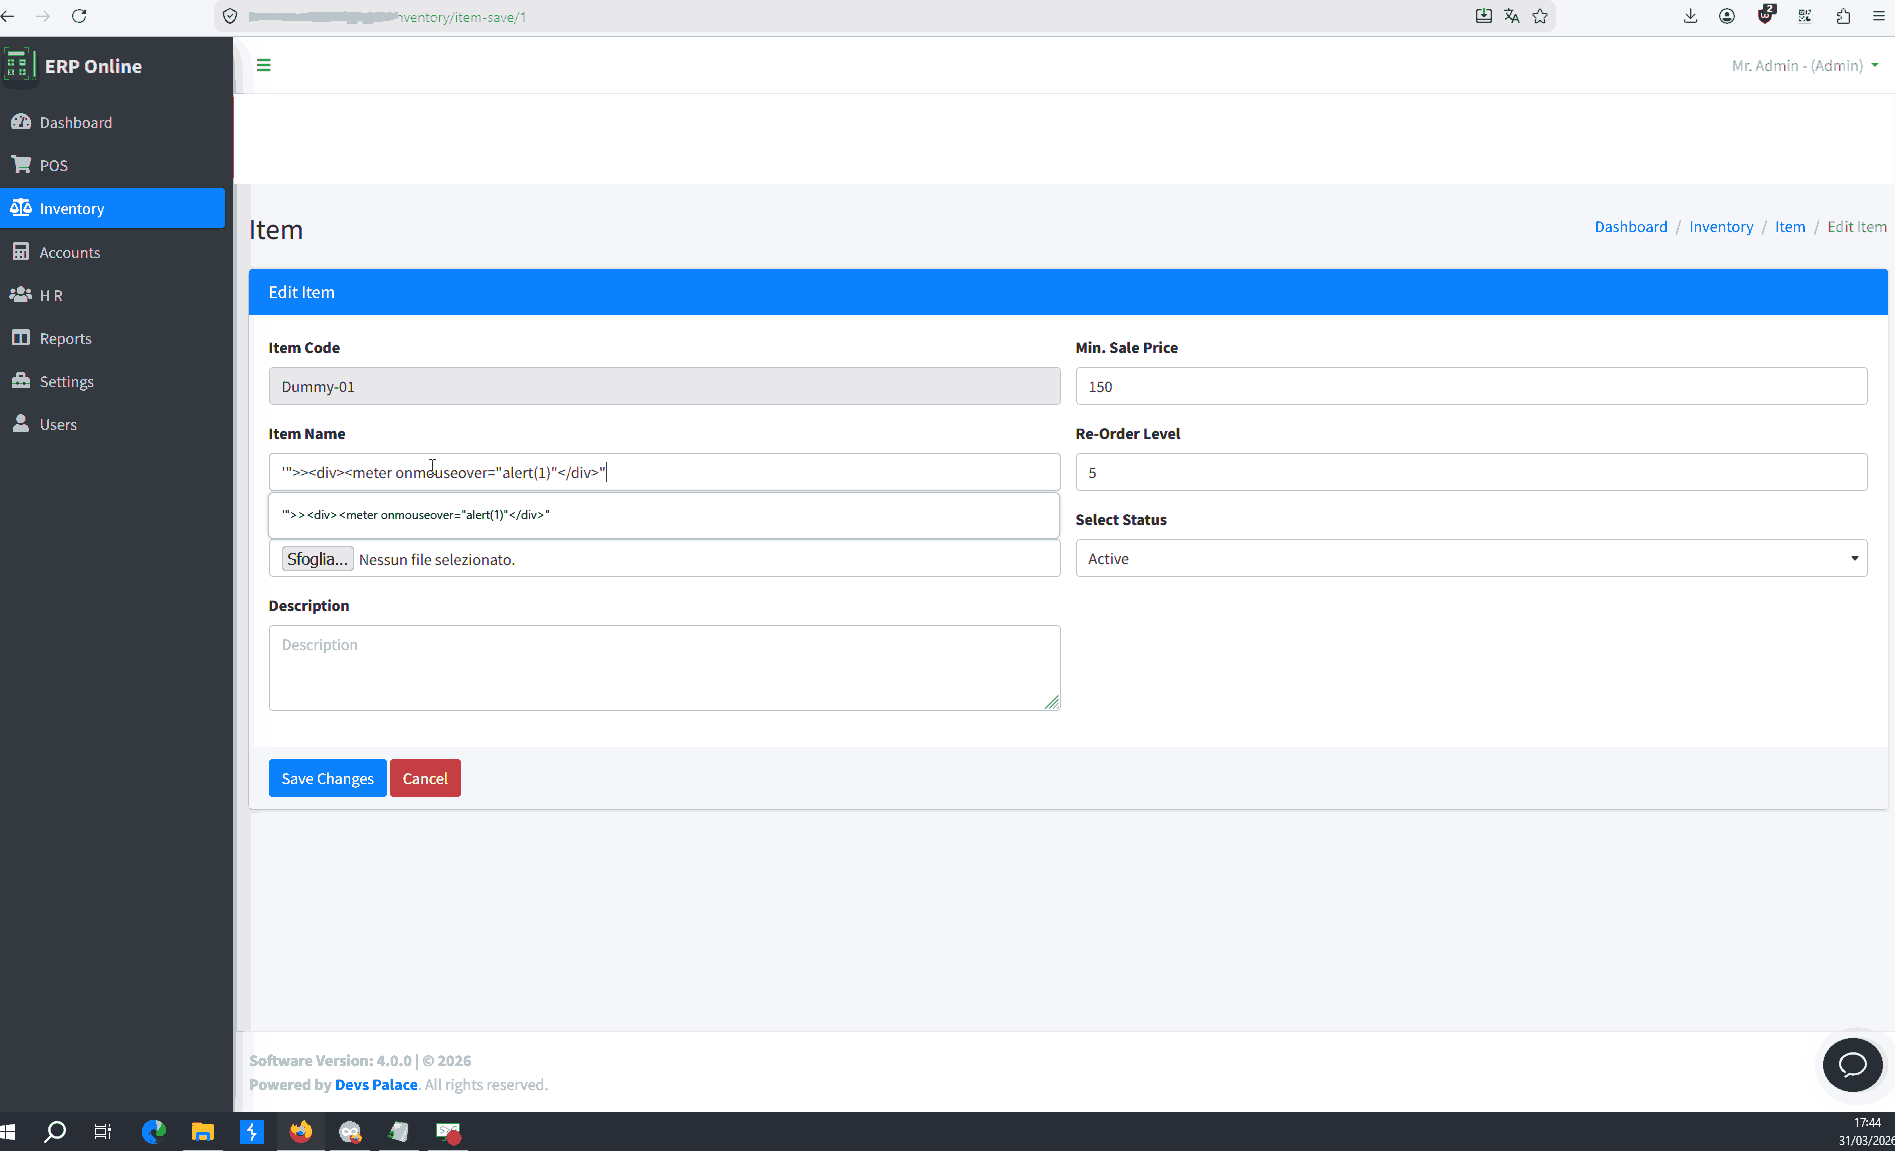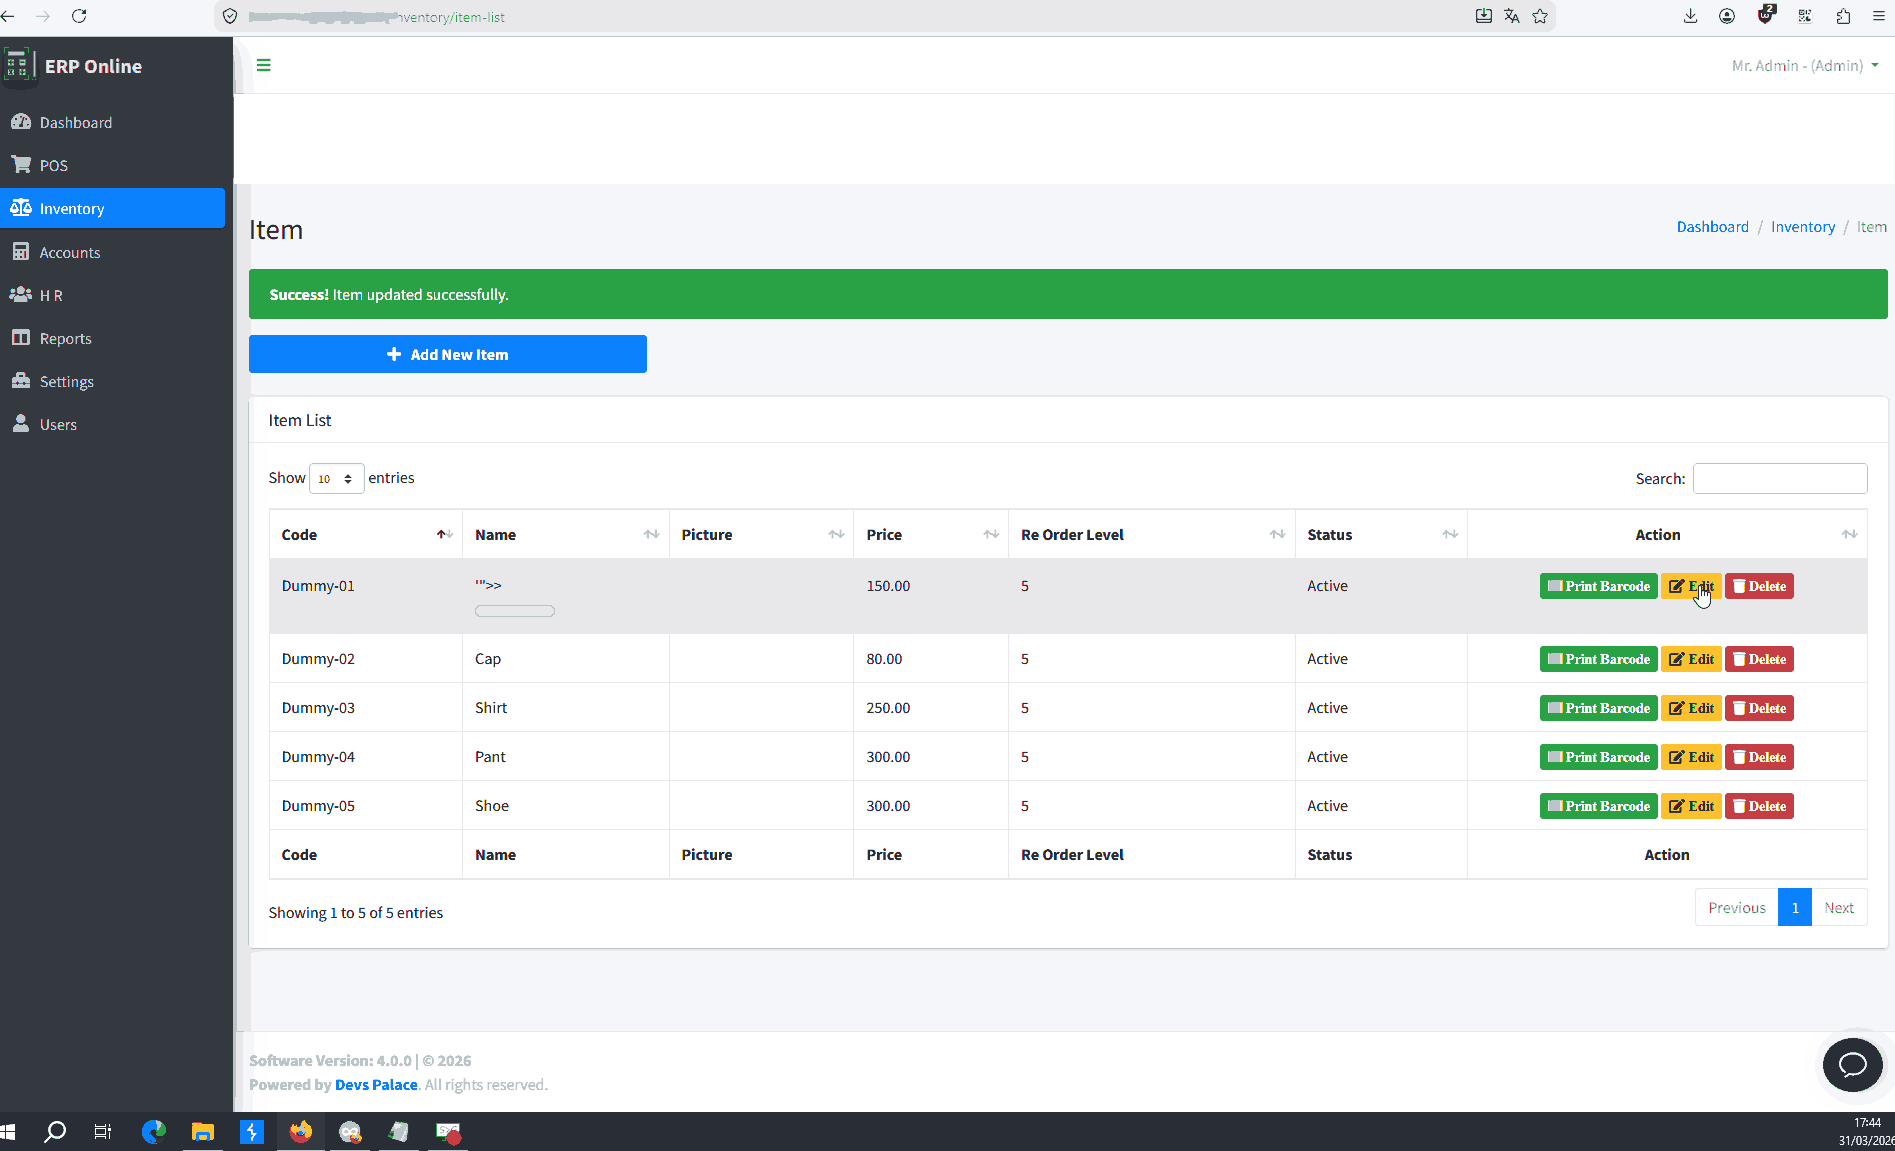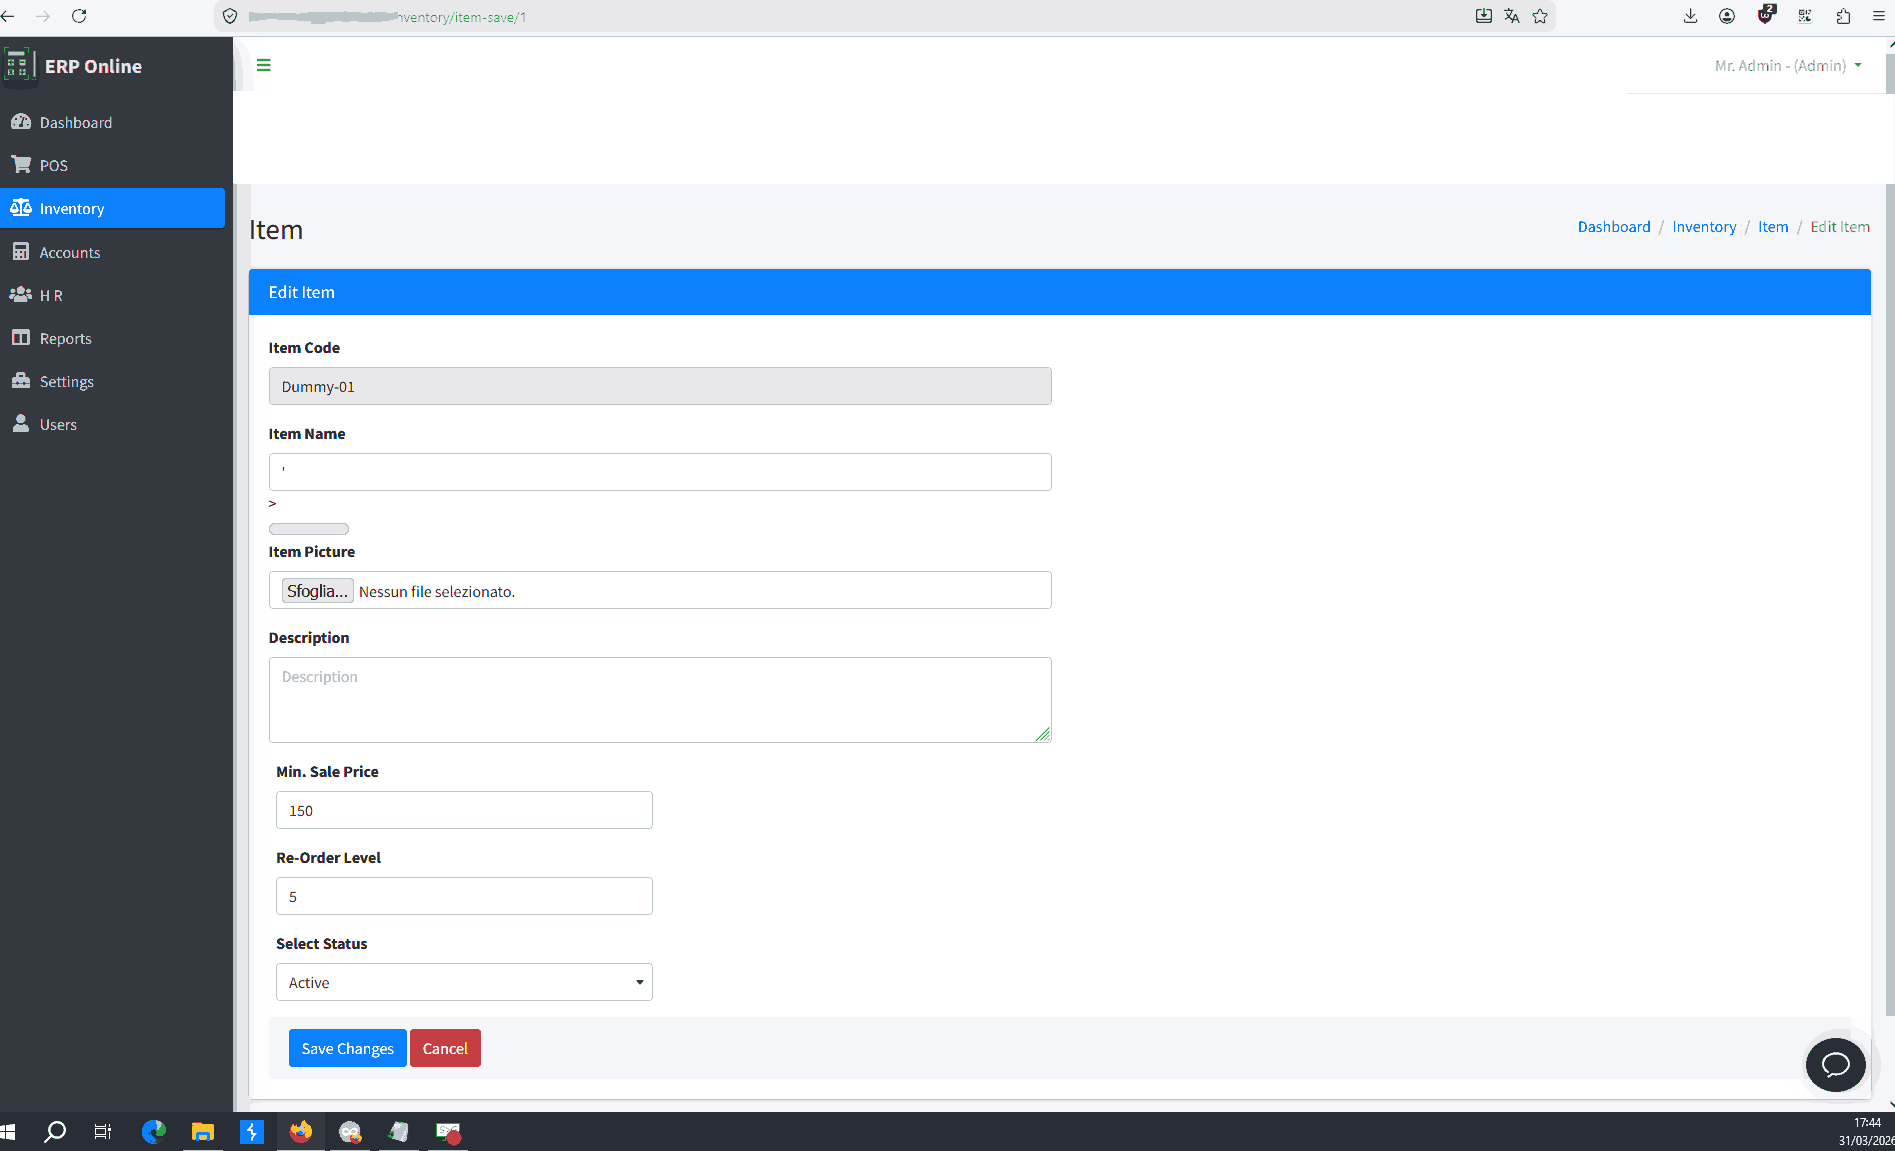
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online versions up to 4.0.0. The flaw is located within the /inventory/add_new_customer file, where improper input neutralization allows for the injection of malicious scripts. An attacker with high-level privileges can initiate this attack remotely, though it requires interaction from another user (typically an administrator) to execute. The vulnerability is also categorized under CWE-94 (Code Injection). A public proof-of-concept exploit is available, and as of the advisory date, the vendor has not responded to disclosure attempts or provided a patch.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-11: advisory: NVD publication date
- 2026-05-11: disclosed: Public disclosure of the vulnerability and exploit