Executive brief
Devs Palace ERP Online, a business management platform, is vulnerable to a security flaw in its inventory management module. An attacker with high-level access could inject malicious scripts that execute in the browsers of other users. This could lead to unauthorized actions being performed on behalf of legitimate users or the defacement of certain application pages.
Technical details
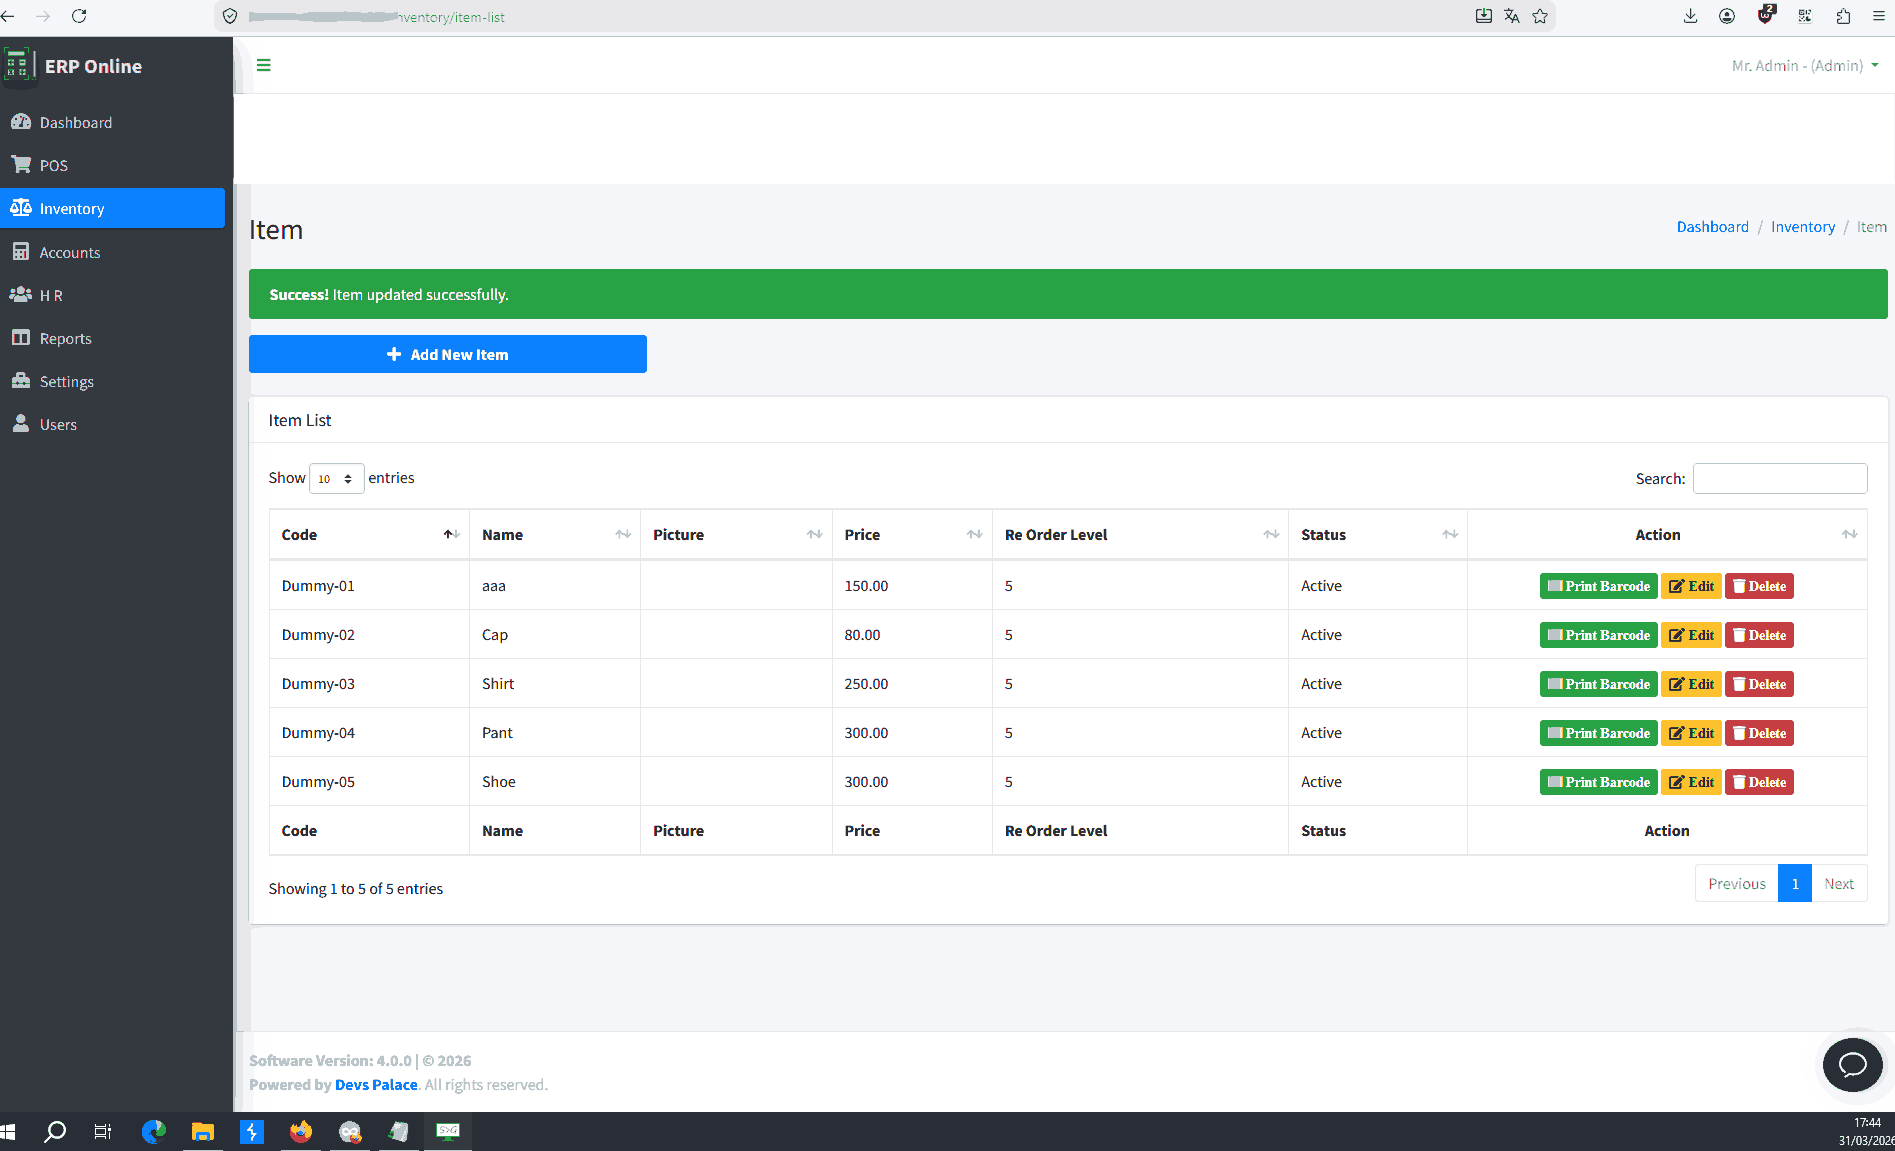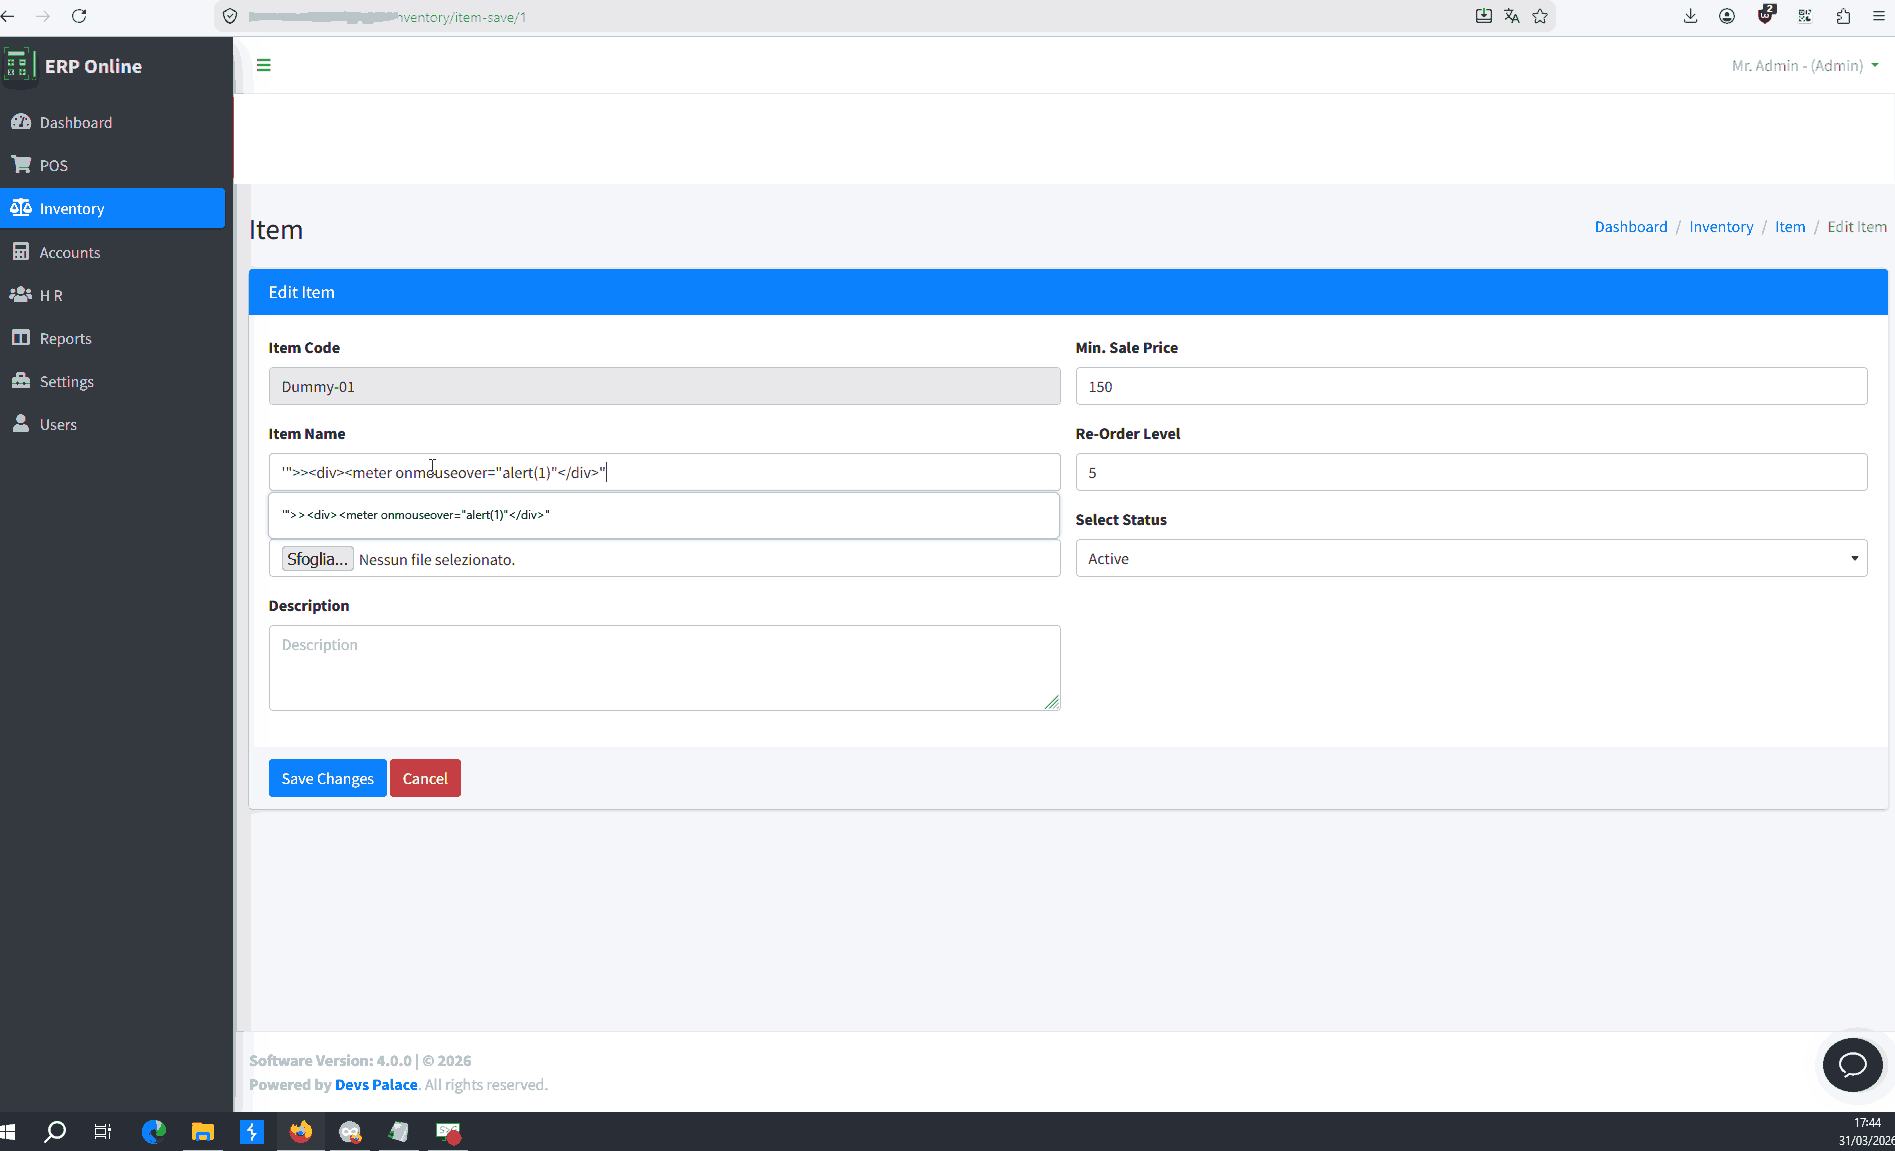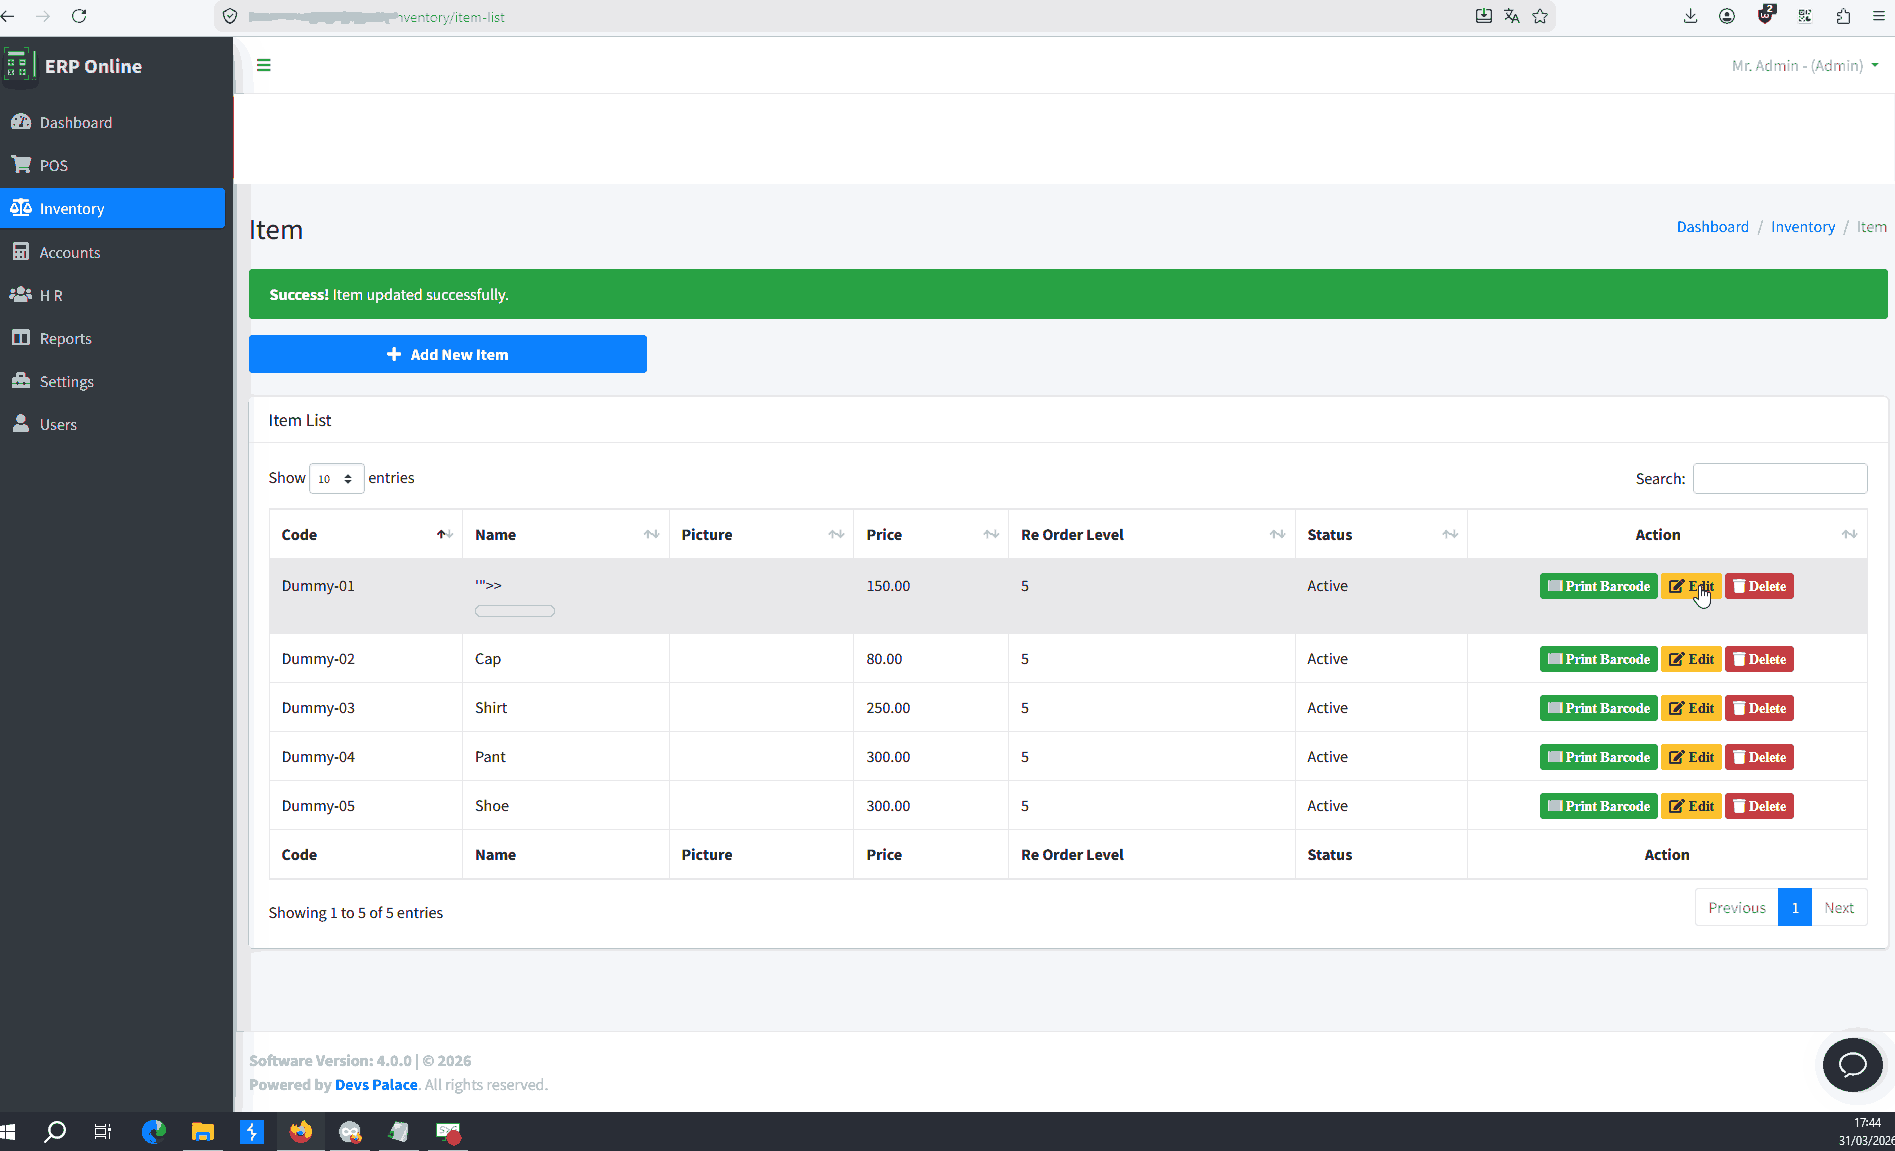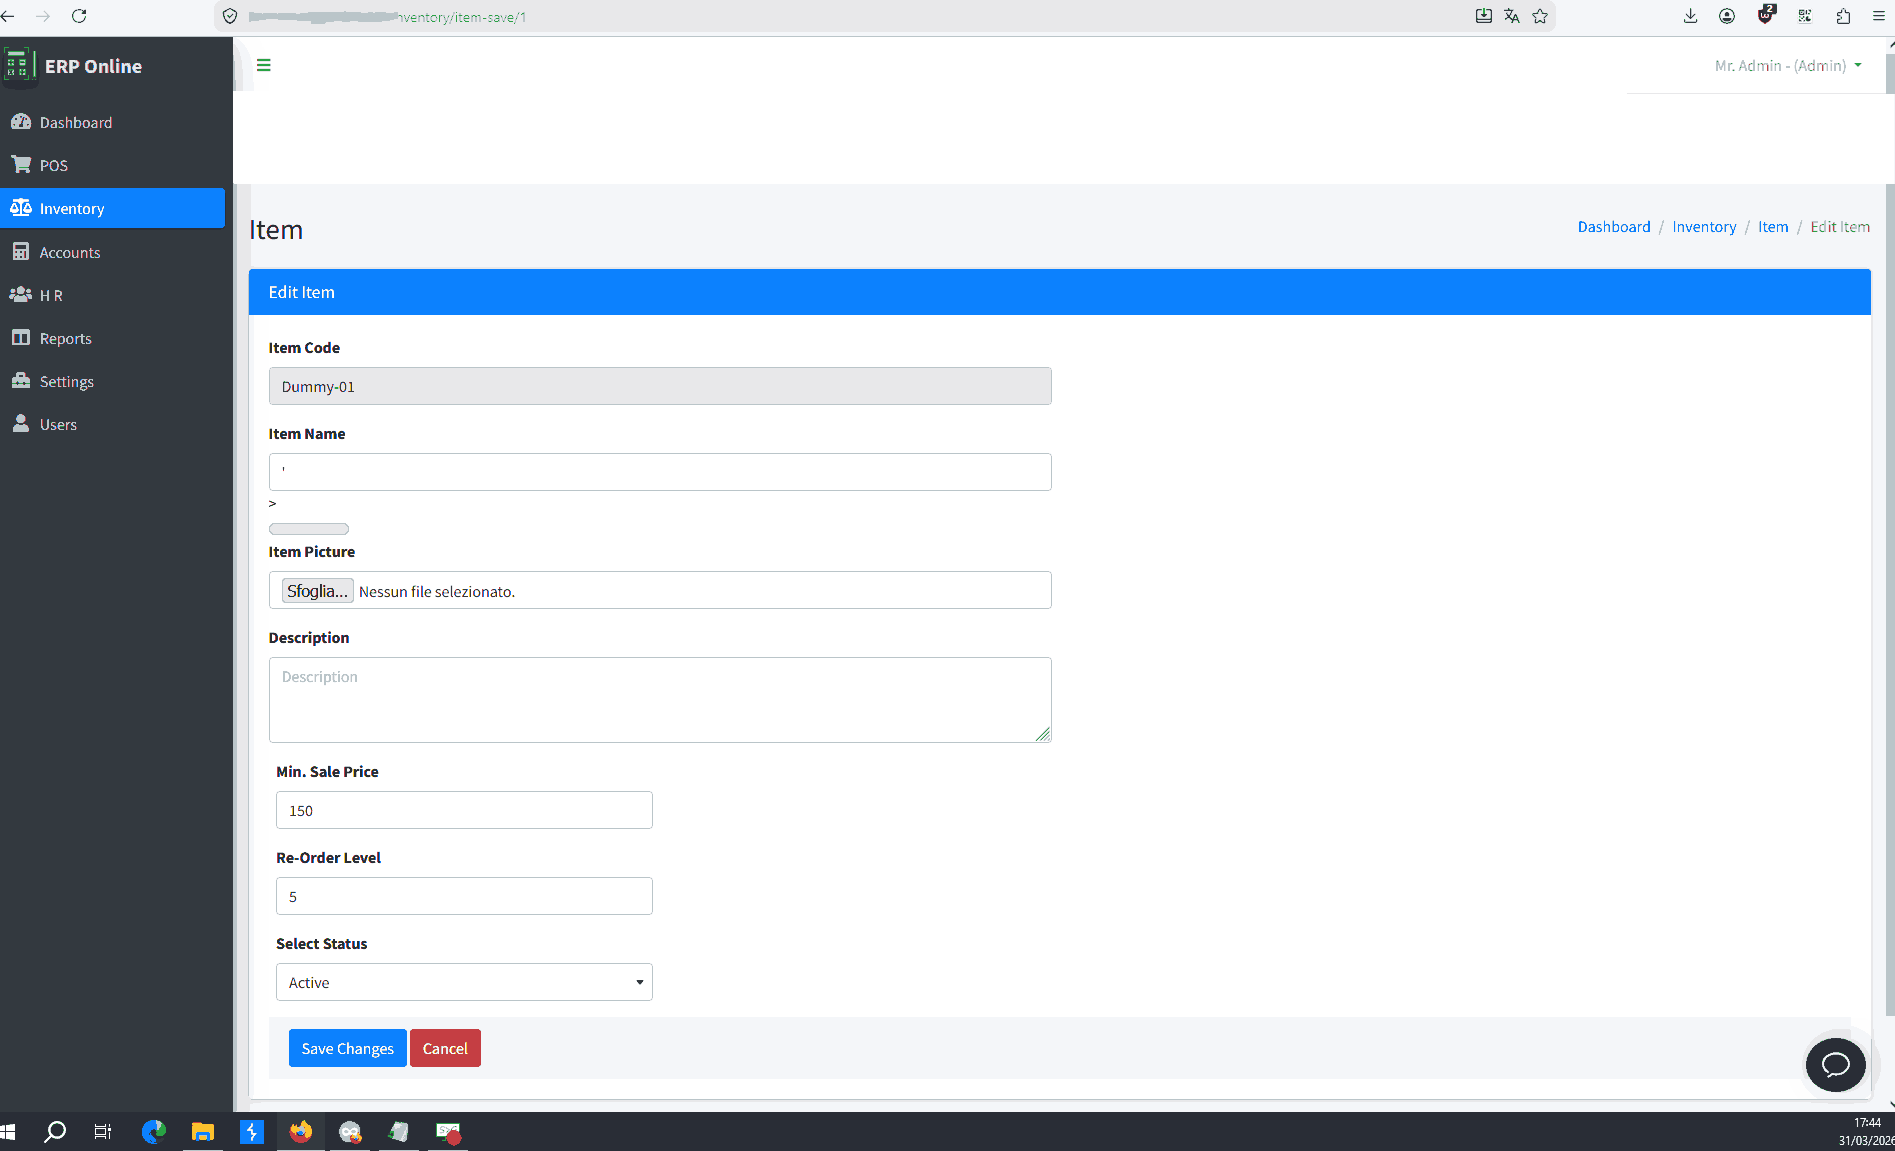
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online up to version 4.0.0. The flaw is located within the /inventory/purchase_save file due to improper neutralization of user-supplied input. A remote attacker with high privileges (PR:H) can exploit this by submitting malicious payloads that are subsequently executed in the context of a victim's browser session. While the impact is limited to low integrity loss and requires user interaction, a public exploit is available. The vendor has reportedly not responded to disclosure attempts.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-11: advisory: NVD publication date
- 2026-05-11: disclosed: Public disclosure of the vulnerability and exploit