Executive brief
Devs Palace ERP Online, a business management platform, contains a security flaw in its inventory management module. An attacker with high-level privileges can inject malicious scripts into the system, which could then execute in the browsers of other users. This could lead to unauthorized actions being performed on behalf of legitimate users or the defacement of internal management pages.
Technical details
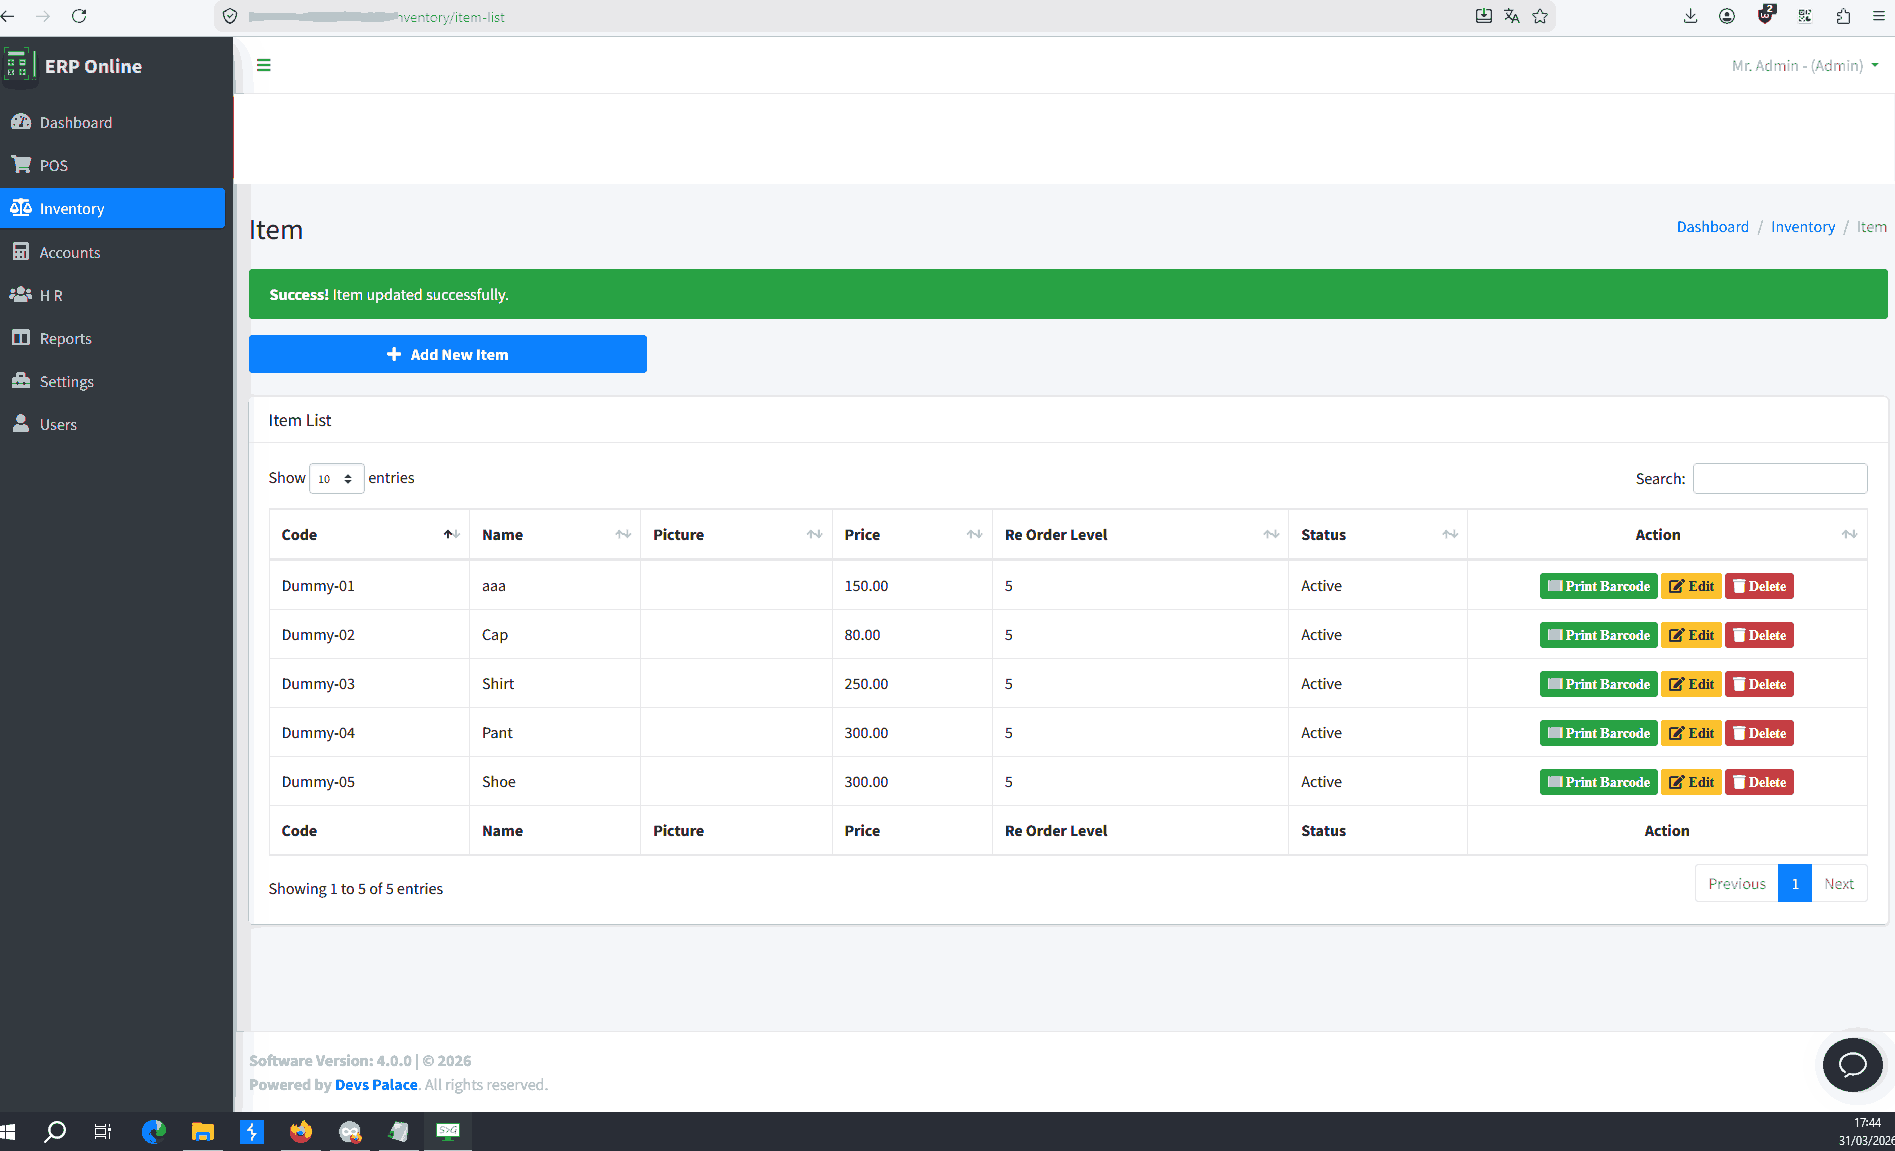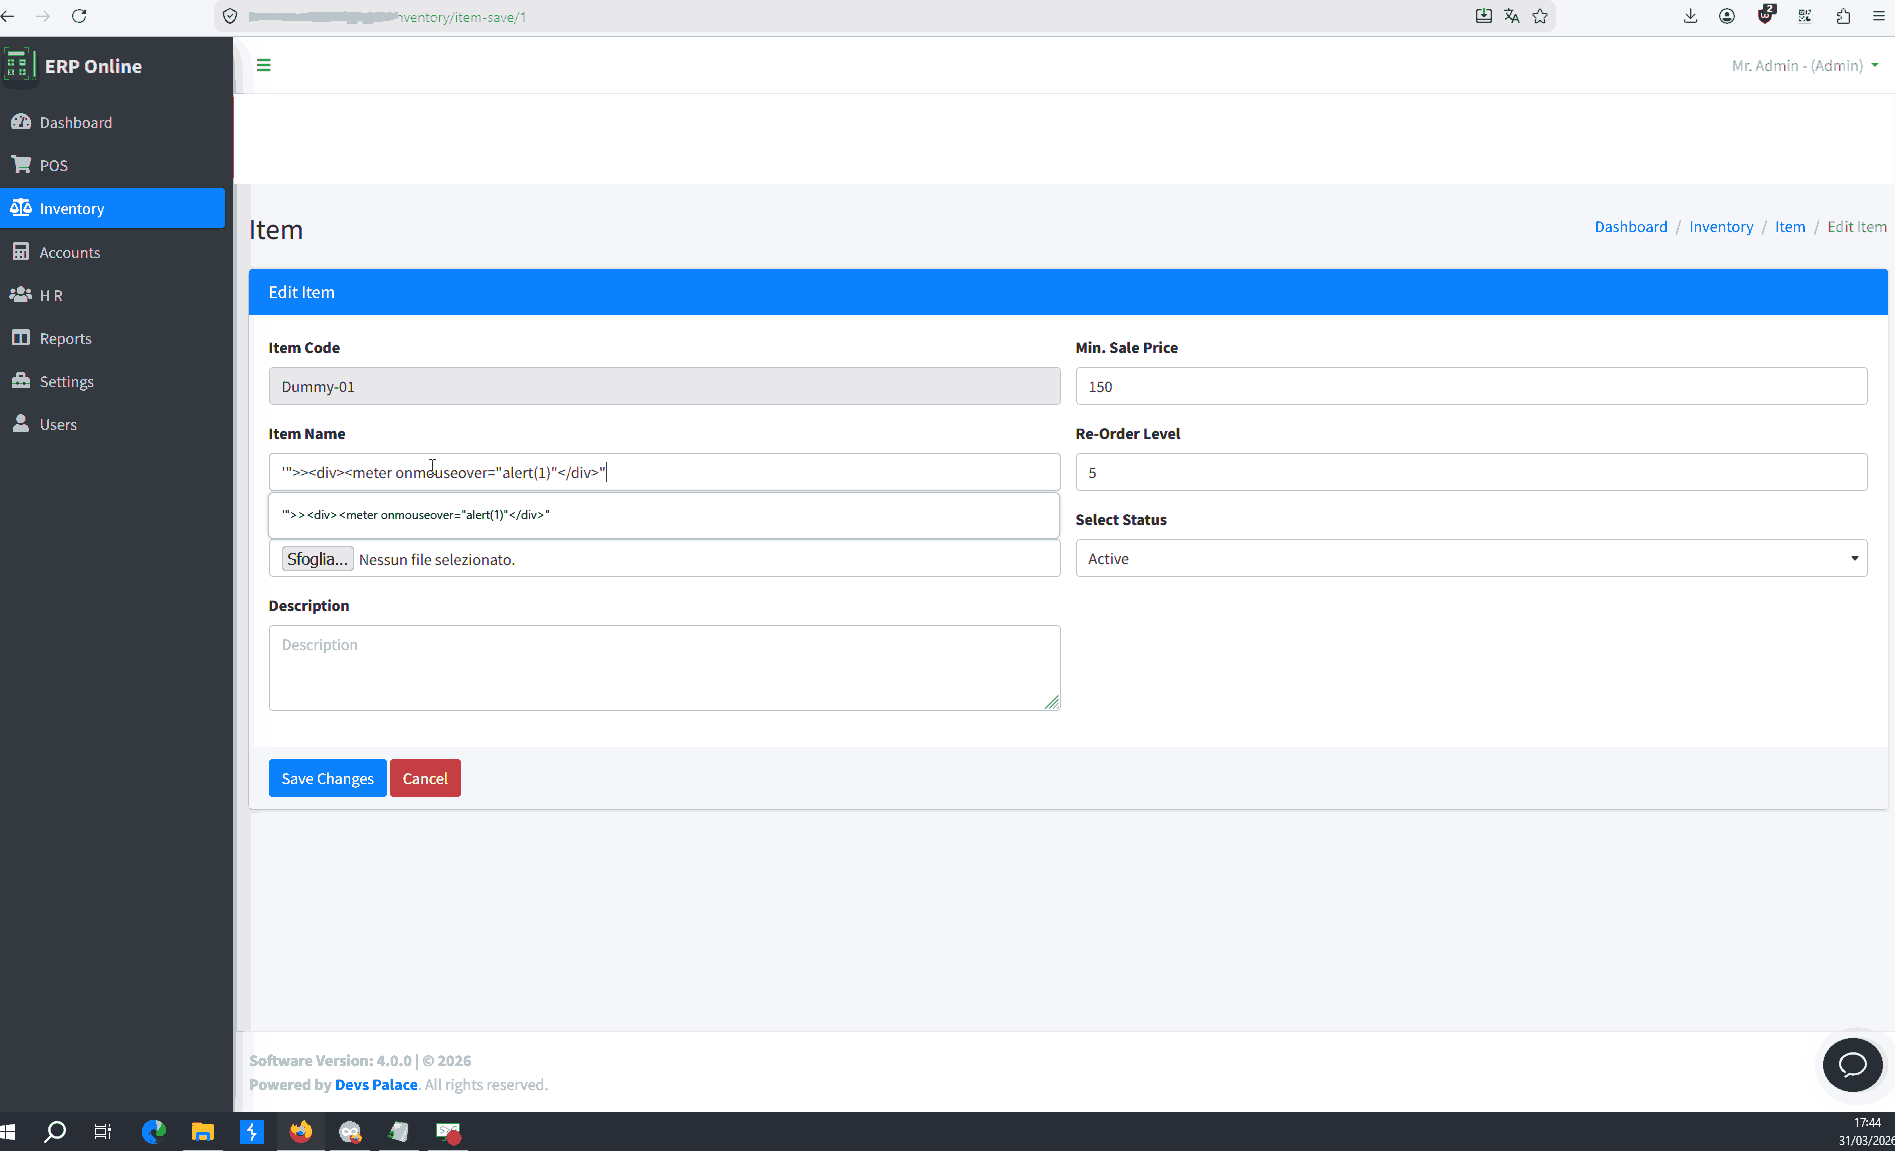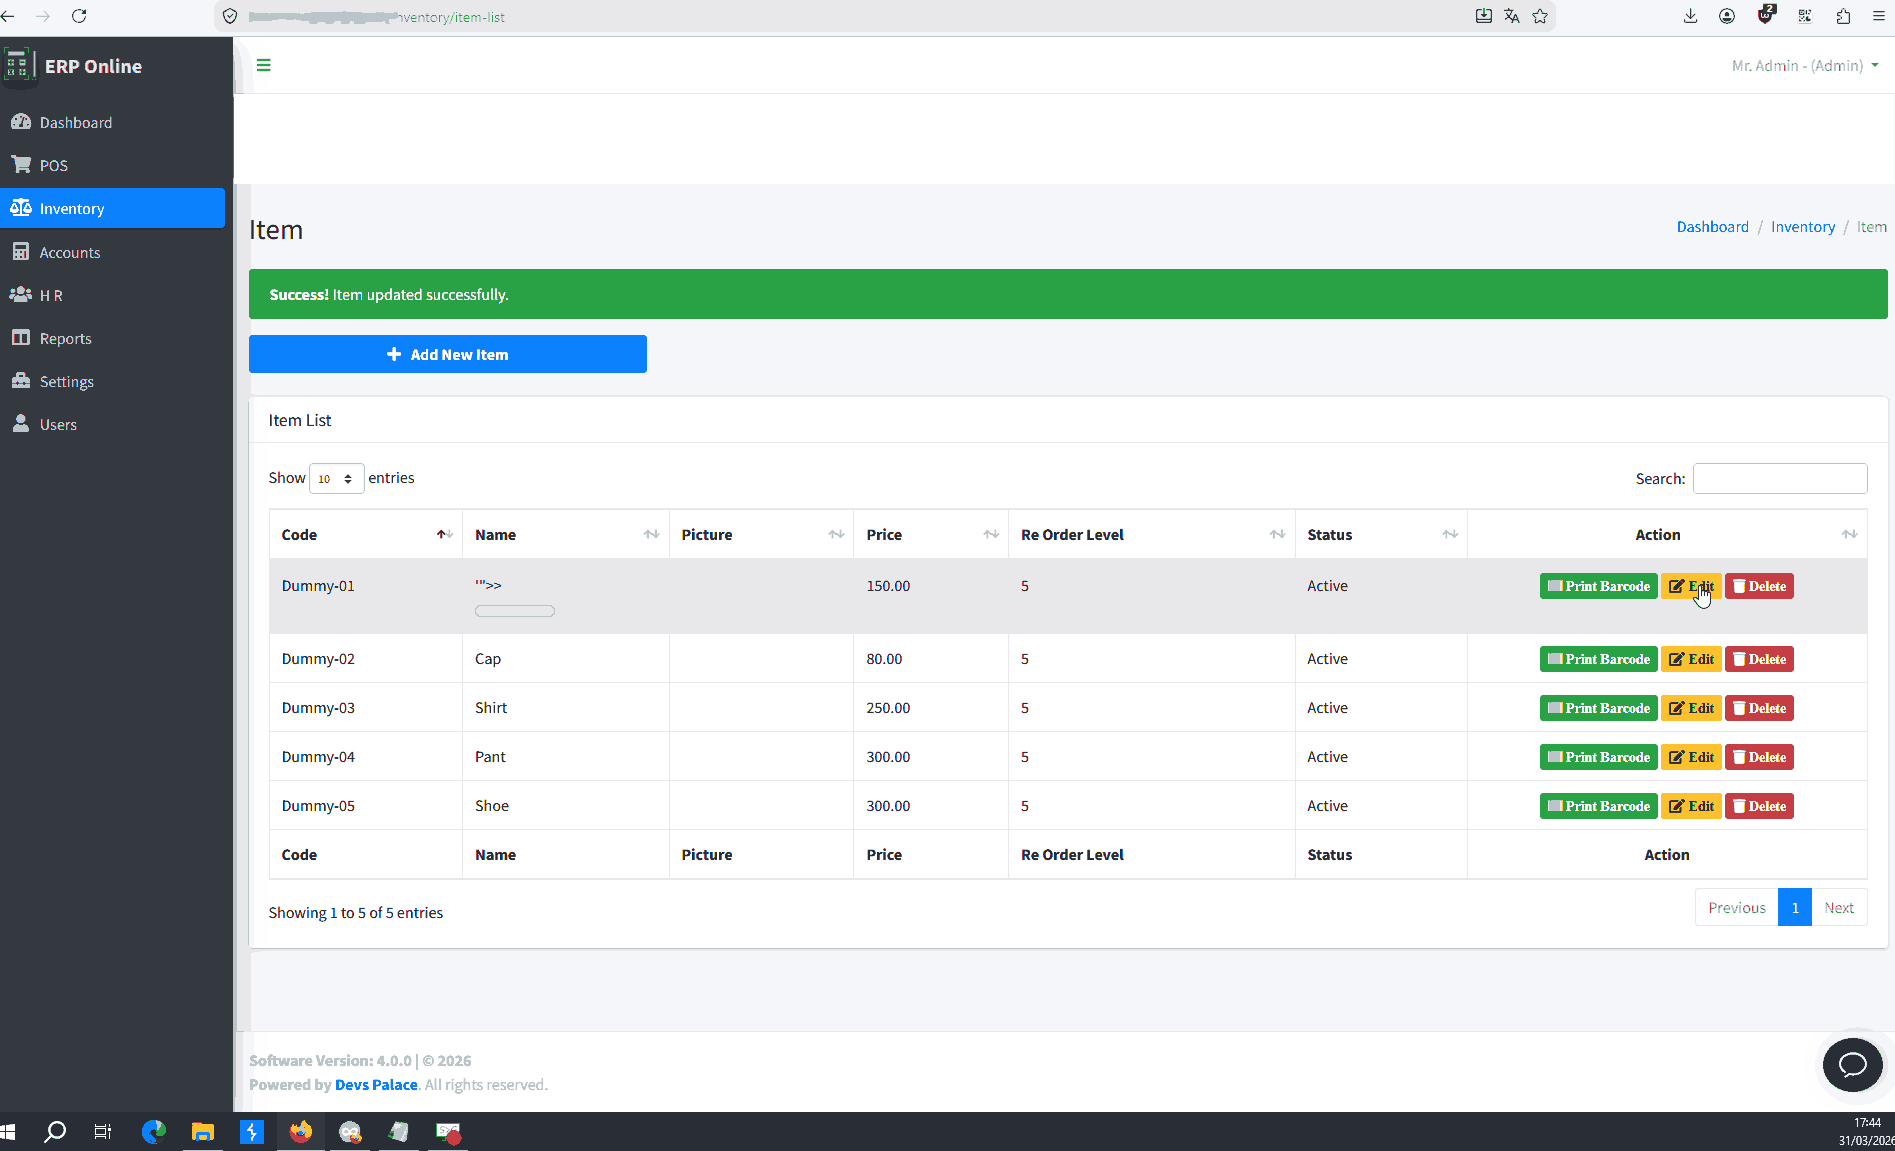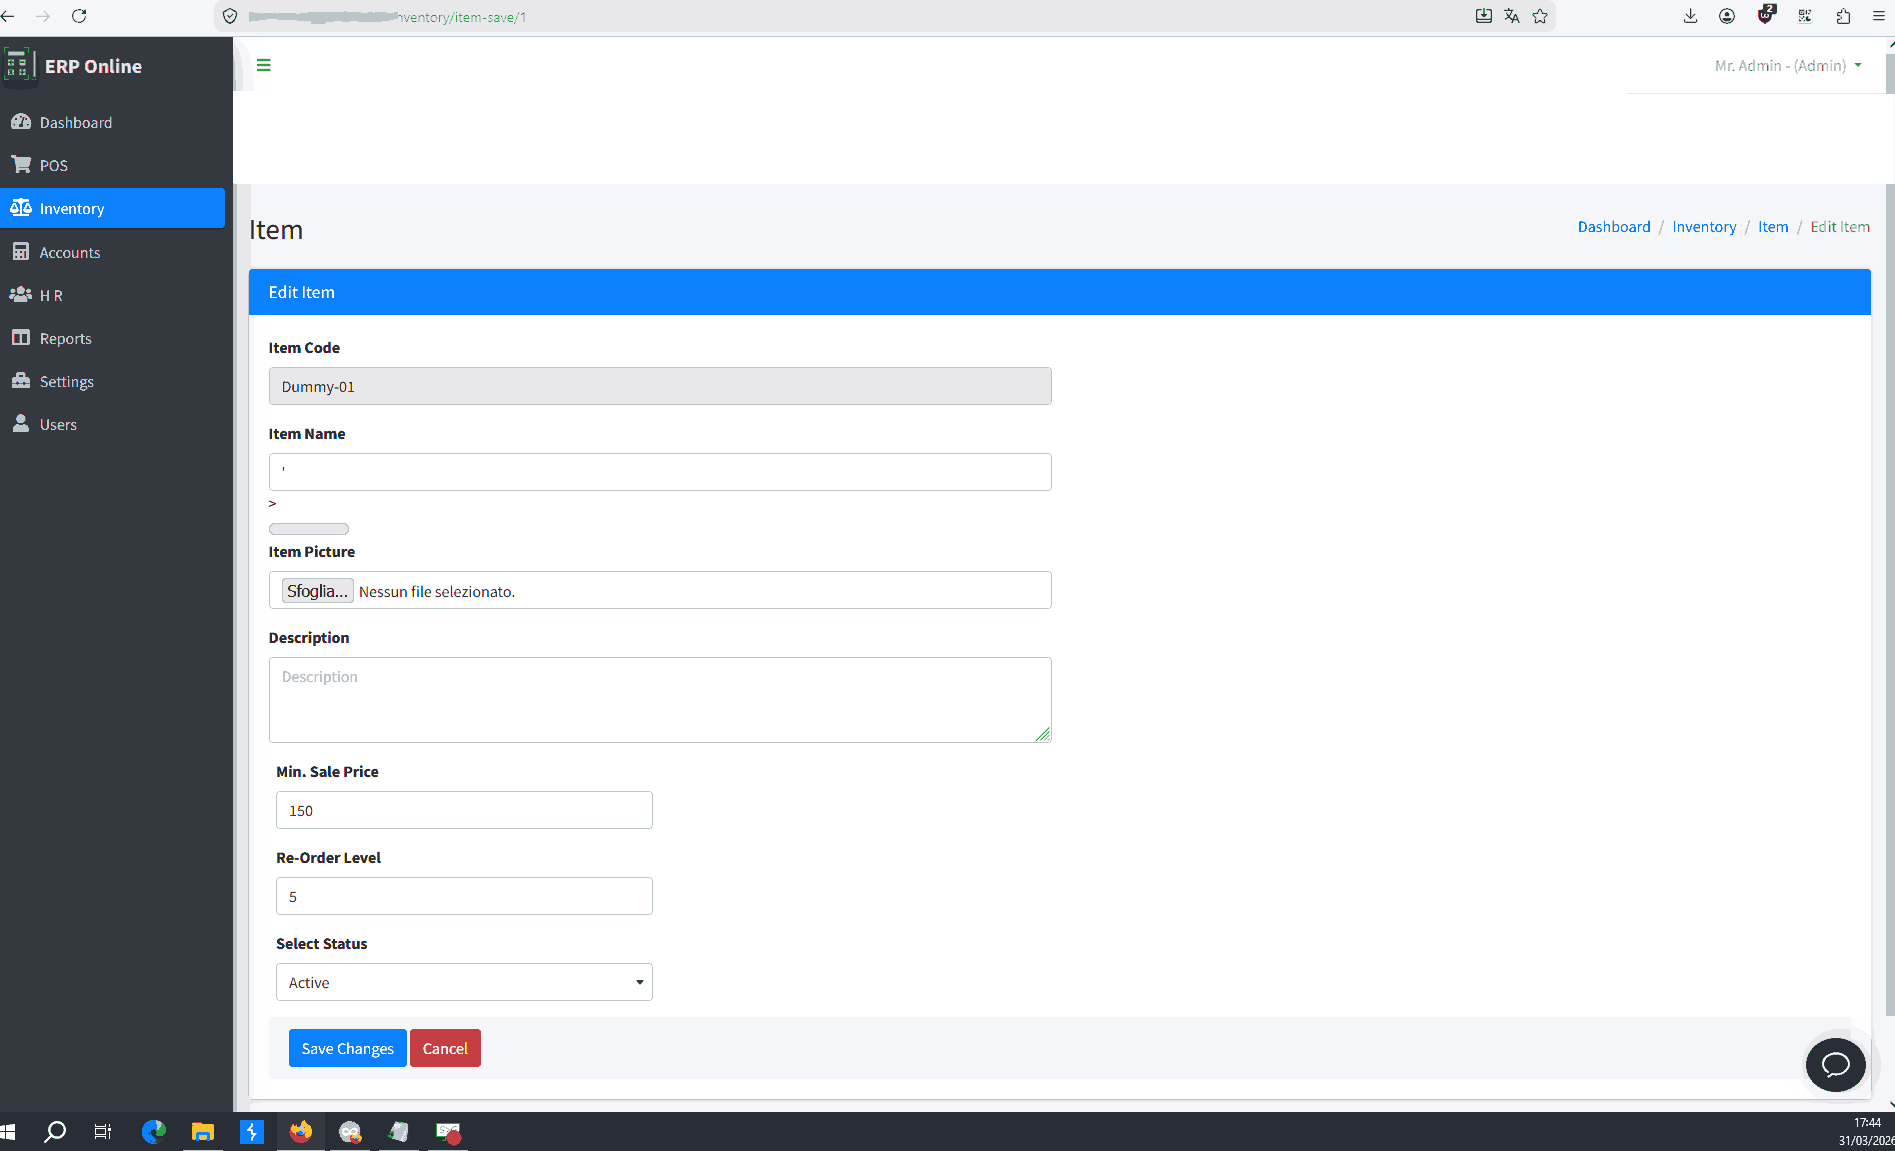
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online up to version 4.0.0. The flaw is located within the /inventory/supplier-save file, where improper input neutralization allows for the injection of malicious web scripts. An attacker with high privileges (PR:H) can trigger this vulnerability remotely. Successful exploitation requires a victim to interact with the affected page (UI:R), allowing the attacker to execute arbitrary script code in the context of the victim's session. A public proof-of-concept exists, and the vendor has reportedly not responded to disclosure attempts.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-10: disclosed: Public disclosure of the vulnerability and exploit.
- 2026-05-10: advisory