Quick answers
- Is CVE-2026-8256 exploited in the wild?
- No. Junglewise Threat Intelligence has no report of CVE-2026-8256 being exploited in the wild.
- How severe is CVE-2026-8256?
- Low severity, with a CVSS score of 2.4, published 11 May 2026.
- Which products and versions are affected?
- Devs Palace ERP Online up to 4.0.0.
- Is there a fix for CVE-2026-8256?
- No fixed version is recorded yet. Check the vendor's advisory in the references below. If you run it, Junglewise drafts a mitigation that fits your setup and applies it once you approve, with senior security engineers behind it.
- How is CVE-2026-8256 attacked?
- It is attacked over the network, in a network appliance.
- Am I affected by CVE-2026-8256?
- Check whether you run Devs Palace ERP Online at an affected version. Junglewise does that check for you around the clock: connect your code, cloud and domains, and it matches new vulnerabilities like this one against what you actually run and tells you when one reaches you.
Technical details
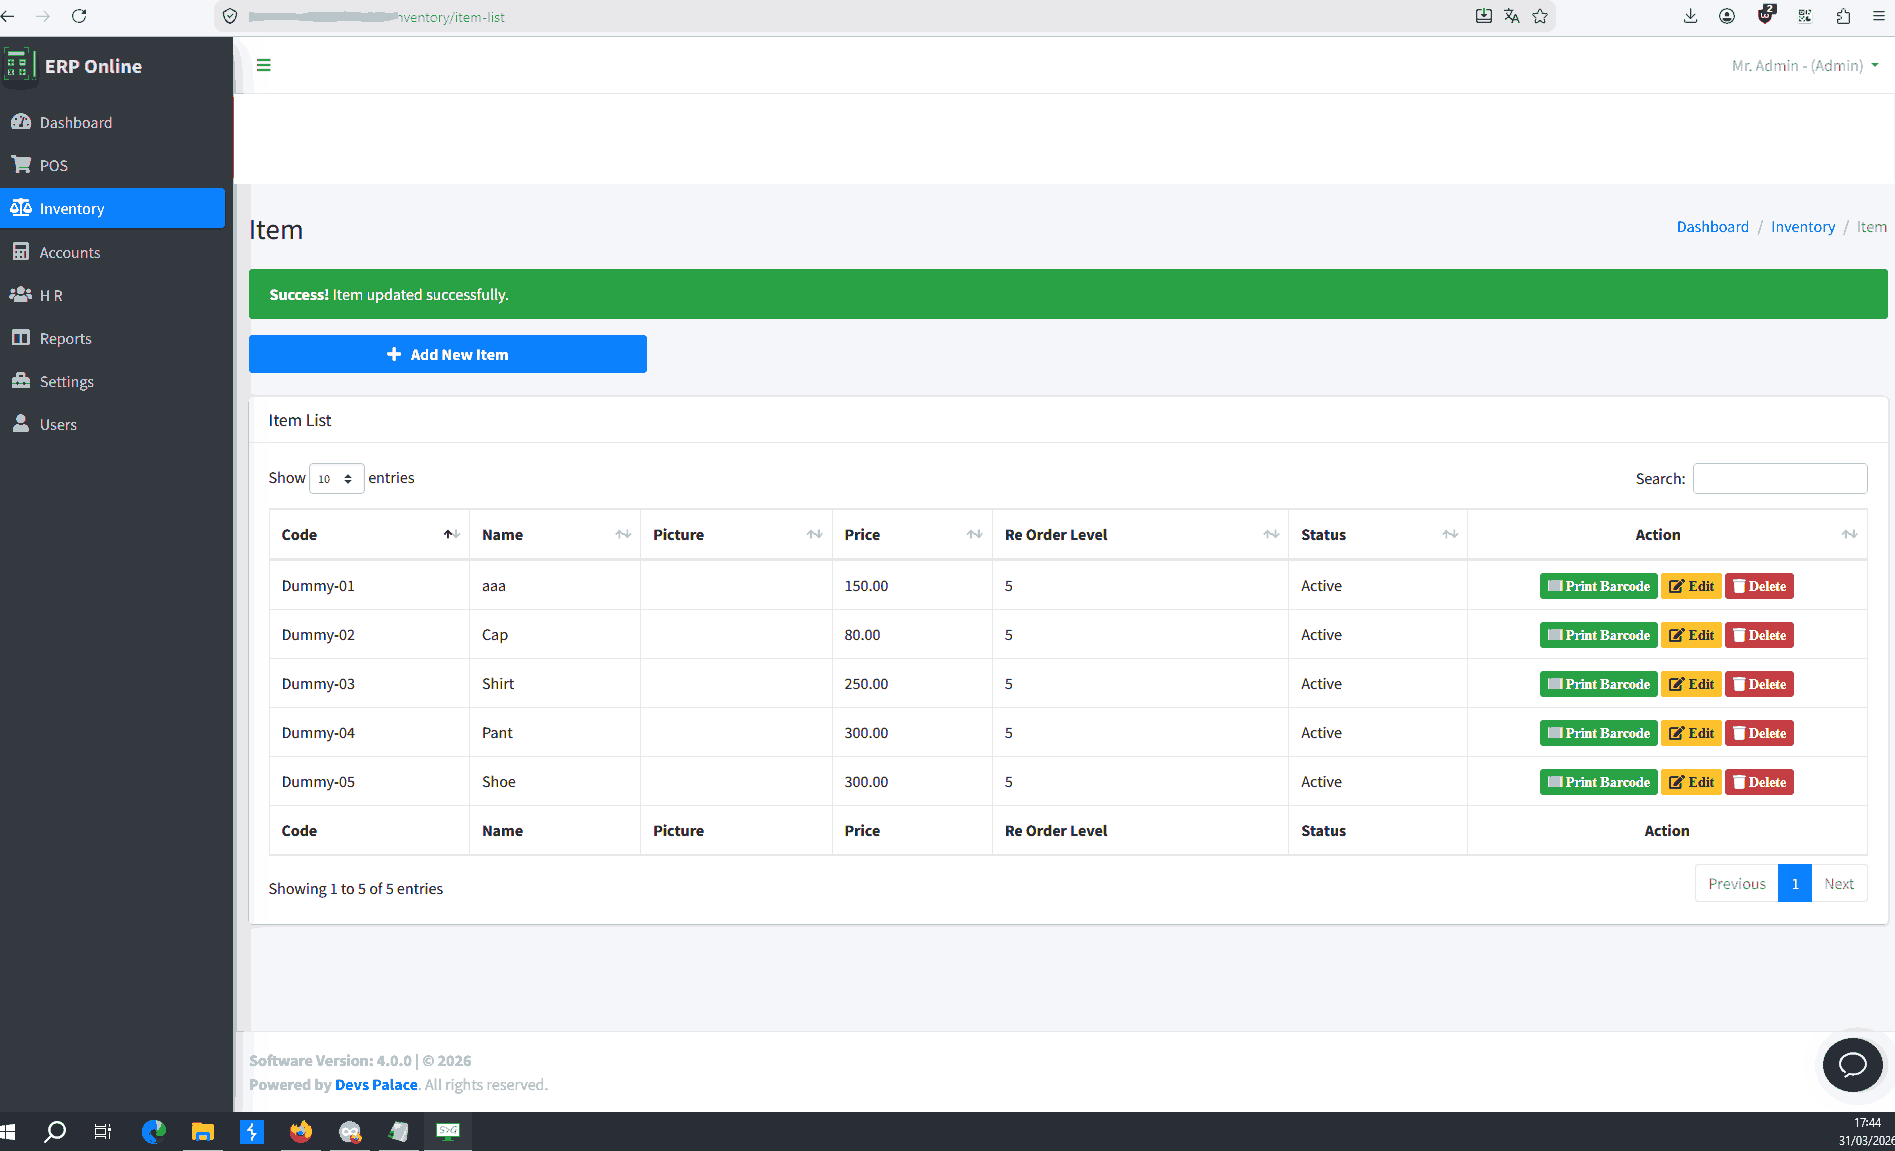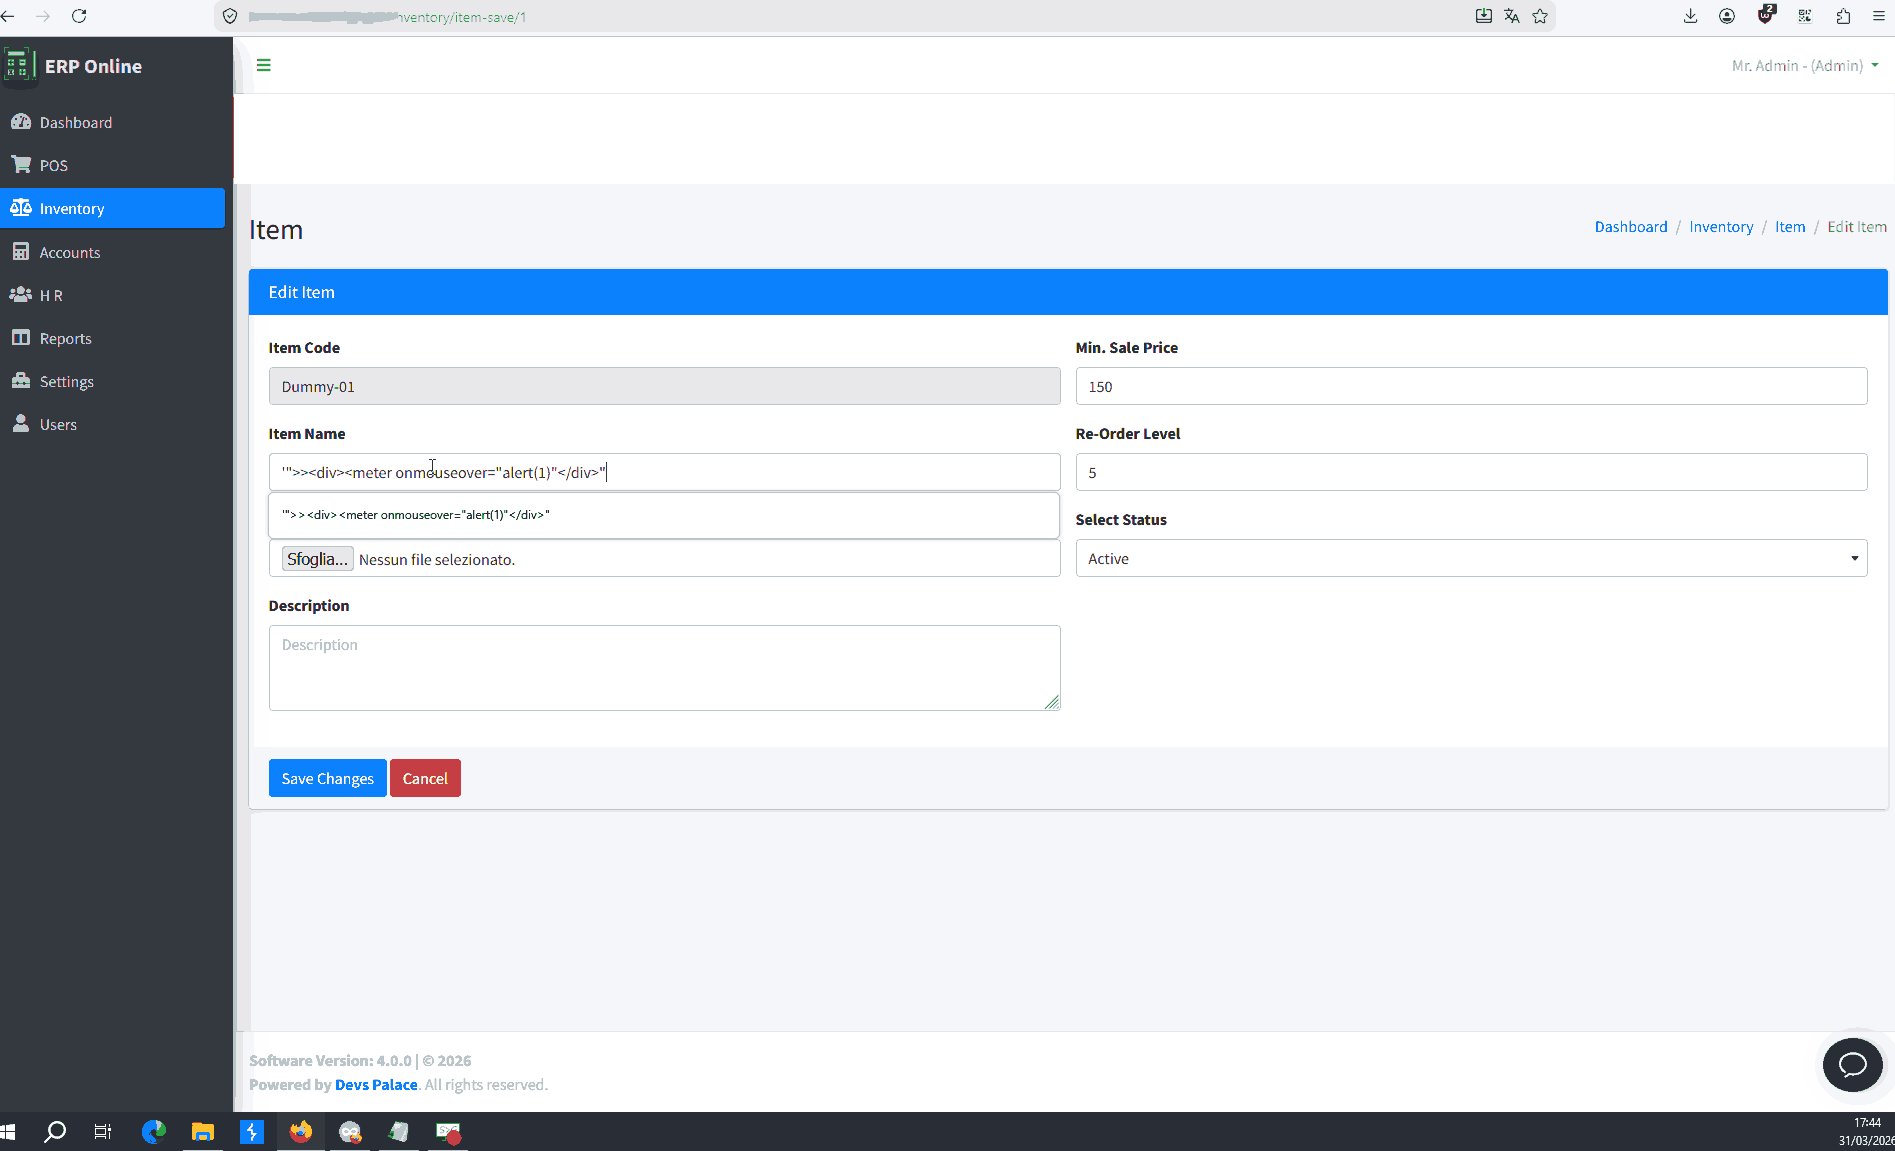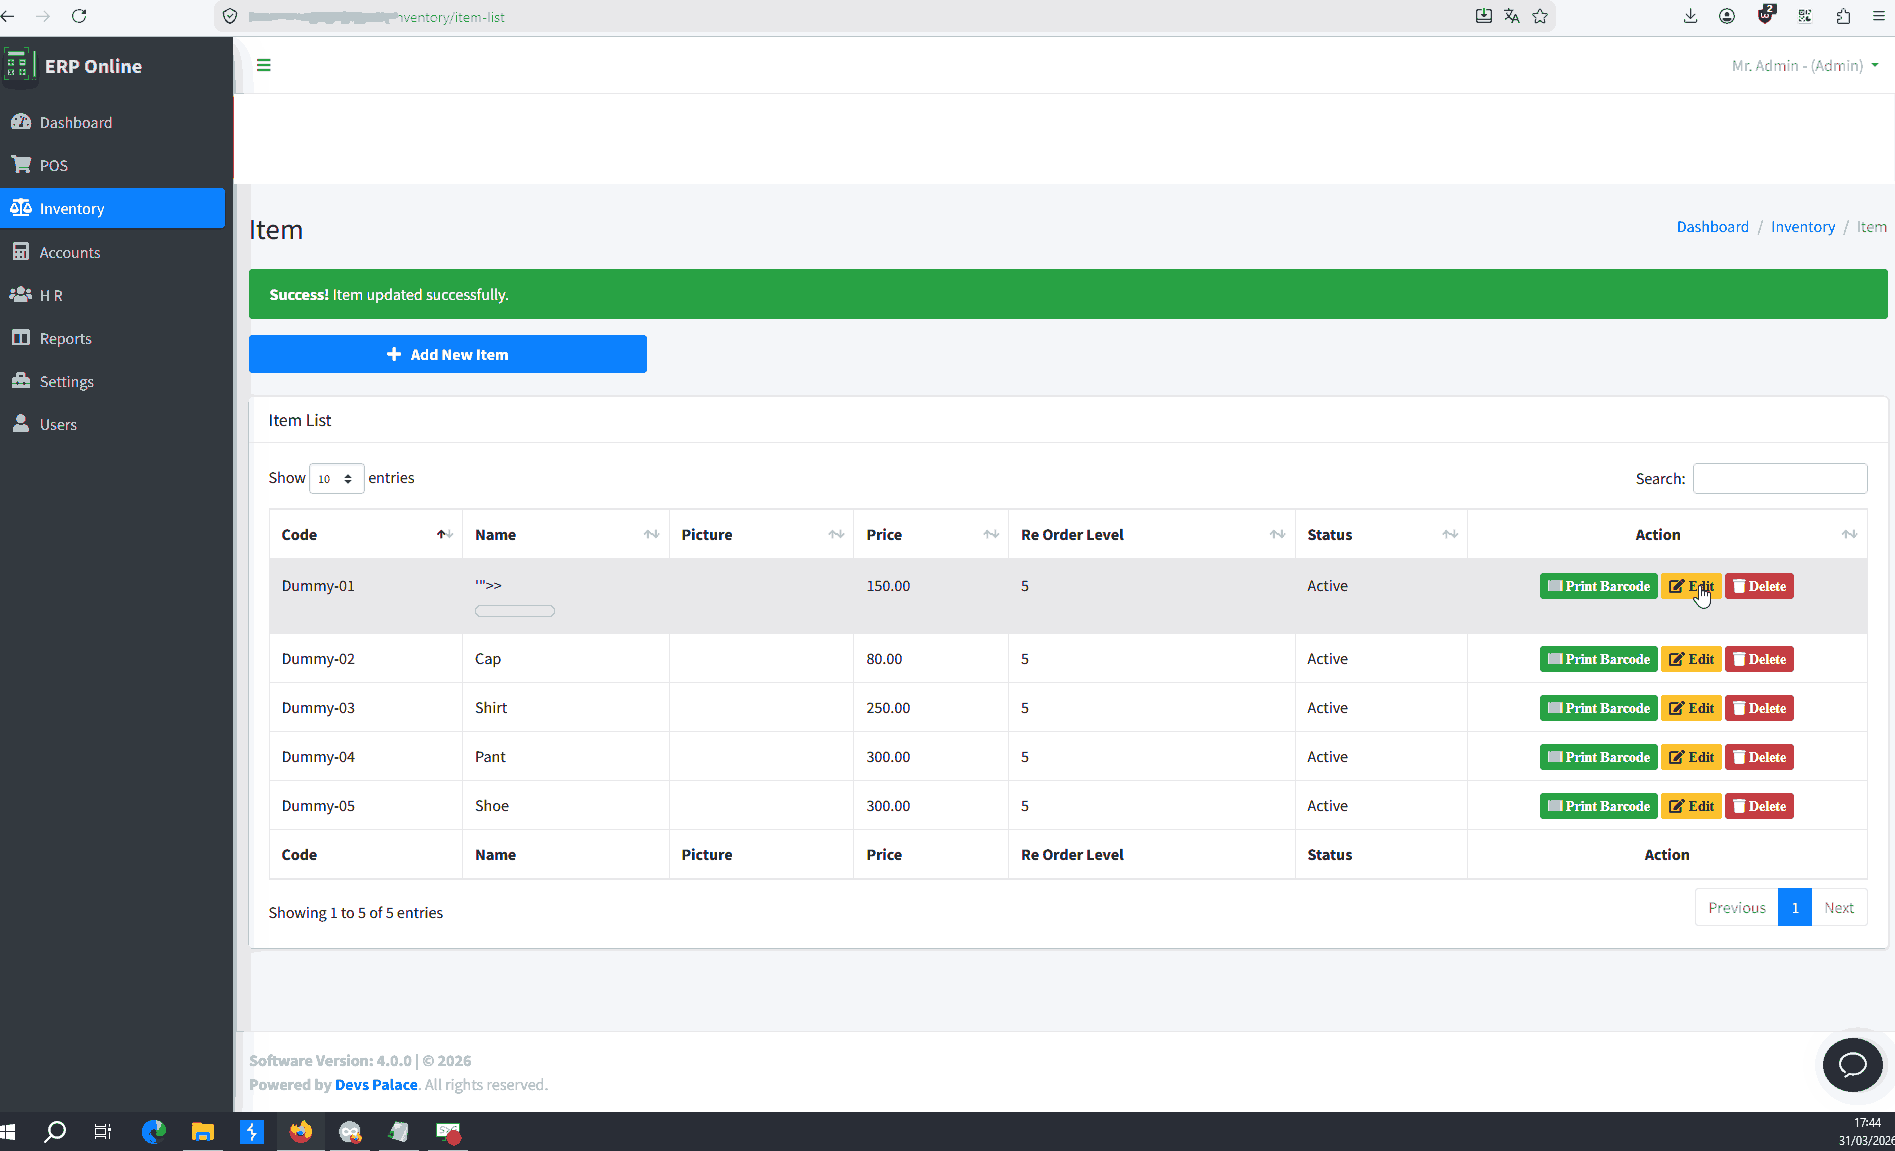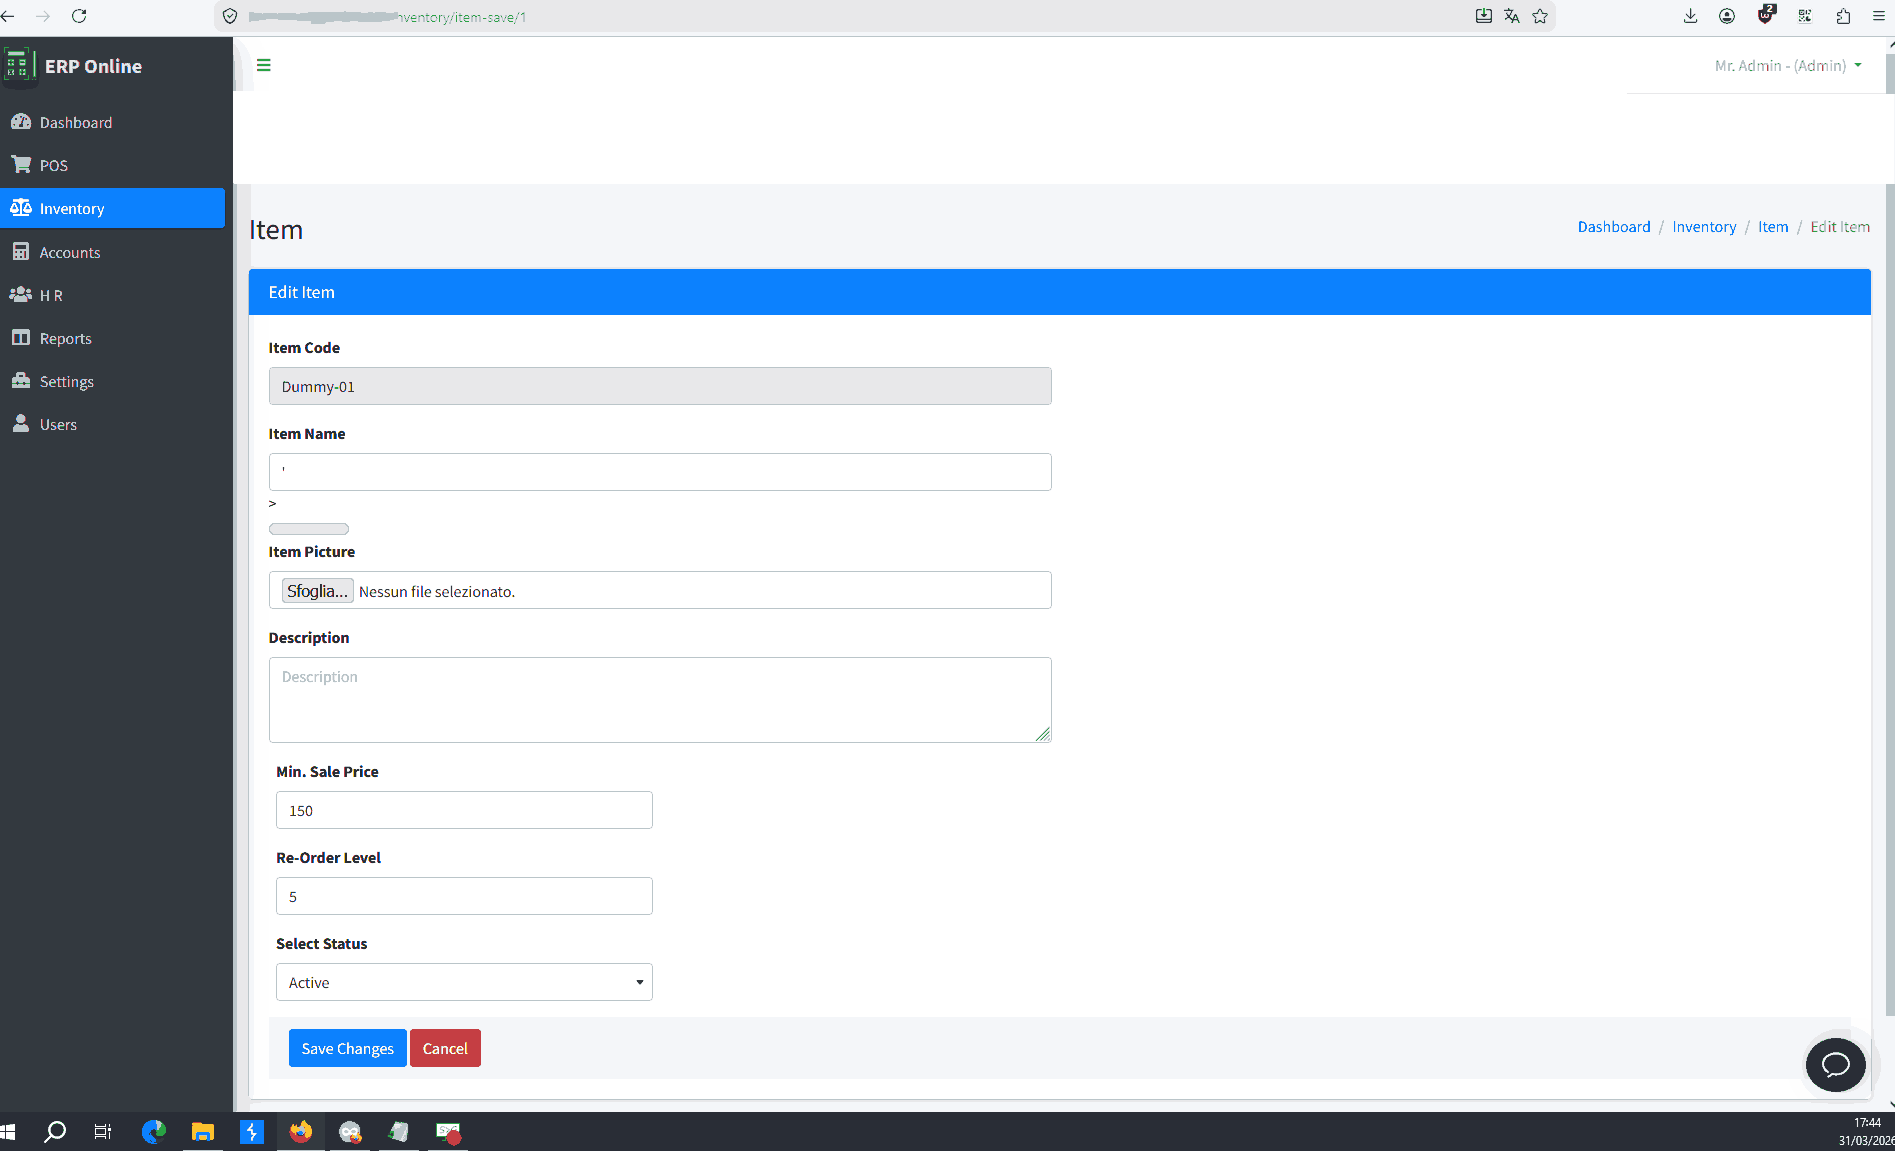
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online versions up to 4.0.0. The flaw is located within the /accounts/mr-save endpoint due to improper neutralization of user-supplied input (CWE-79). An attacker with high-level privileges (PR:H) can exploit this vulnerability remotely by submitting crafted data that is subsequently executed as JavaScript in the victim's browser. Although the vendor was notified, no patch has been released, and a public exploit (PoC) is currently available. The vulnerability also carries implications of code injection (CWE-94).
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-11: advisory: NVD publication date
- 2026-05-11: disclosed: Public disclosure of the exploit