Quick answers
- Is CVE-2026-8218 exploited in the wild?
- No. Junglewise Threat Intelligence has no report of CVE-2026-8218 being exploited in the wild.
- How severe is CVE-2026-8218?
- Low severity, with a CVSS score of 2.4, published 10 May 2026.
- Which products and versions are affected?
- Devs Palace ERP Online up to 4.0.0.
- Is there a fix for CVE-2026-8218?
- No fixed version is recorded yet. Check the vendor's advisory in the references below. If you run it, Junglewise drafts a mitigation that fits your setup and applies it once you approve, with senior security engineers behind it.
- How is CVE-2026-8218 attacked?
- It is attacked over the network, in a web application.
- Am I affected by CVE-2026-8218?
- Check whether you run Devs Palace ERP Online at an affected version. Junglewise does that check for you around the clock: connect your code, cloud and domains, and it matches new vulnerabilities like this one against what you actually run and tells you when one reaches you.
Technical details
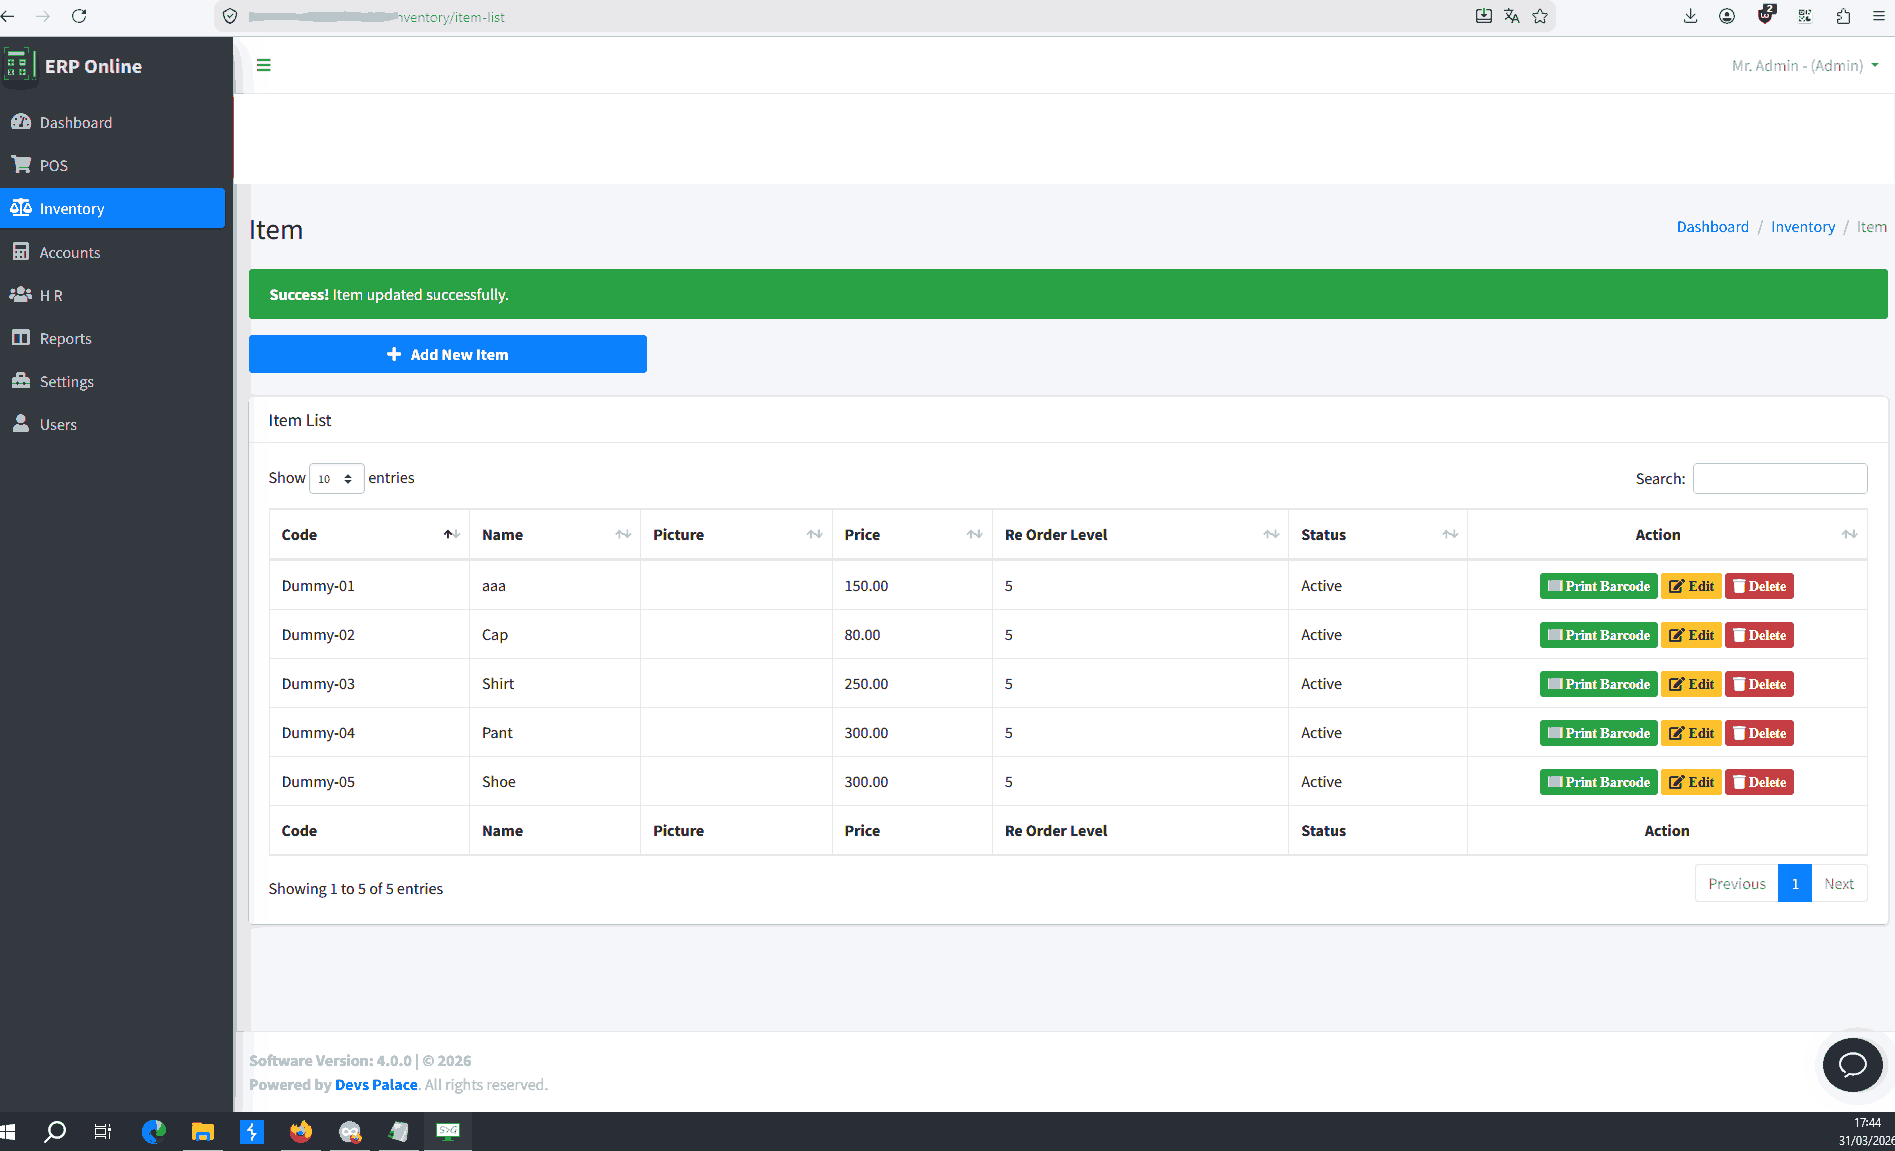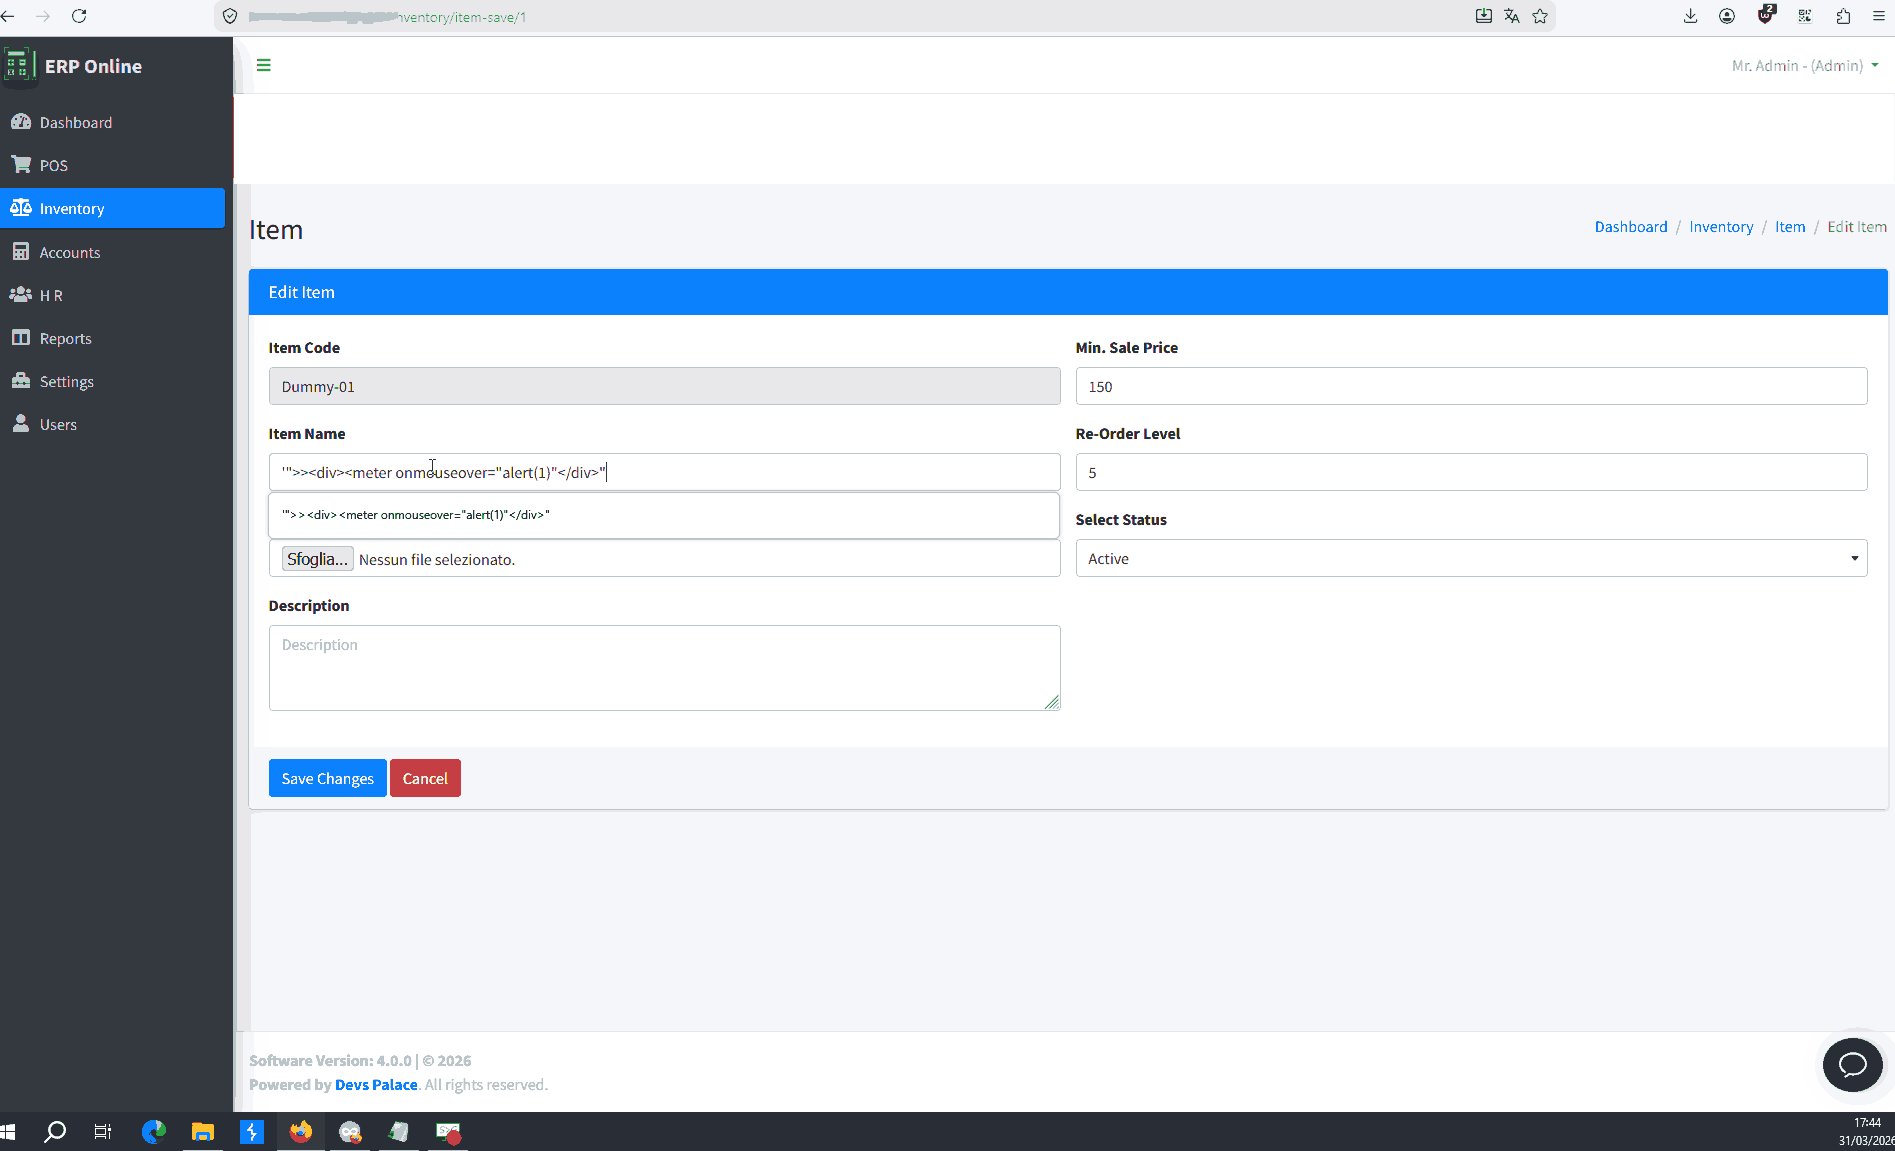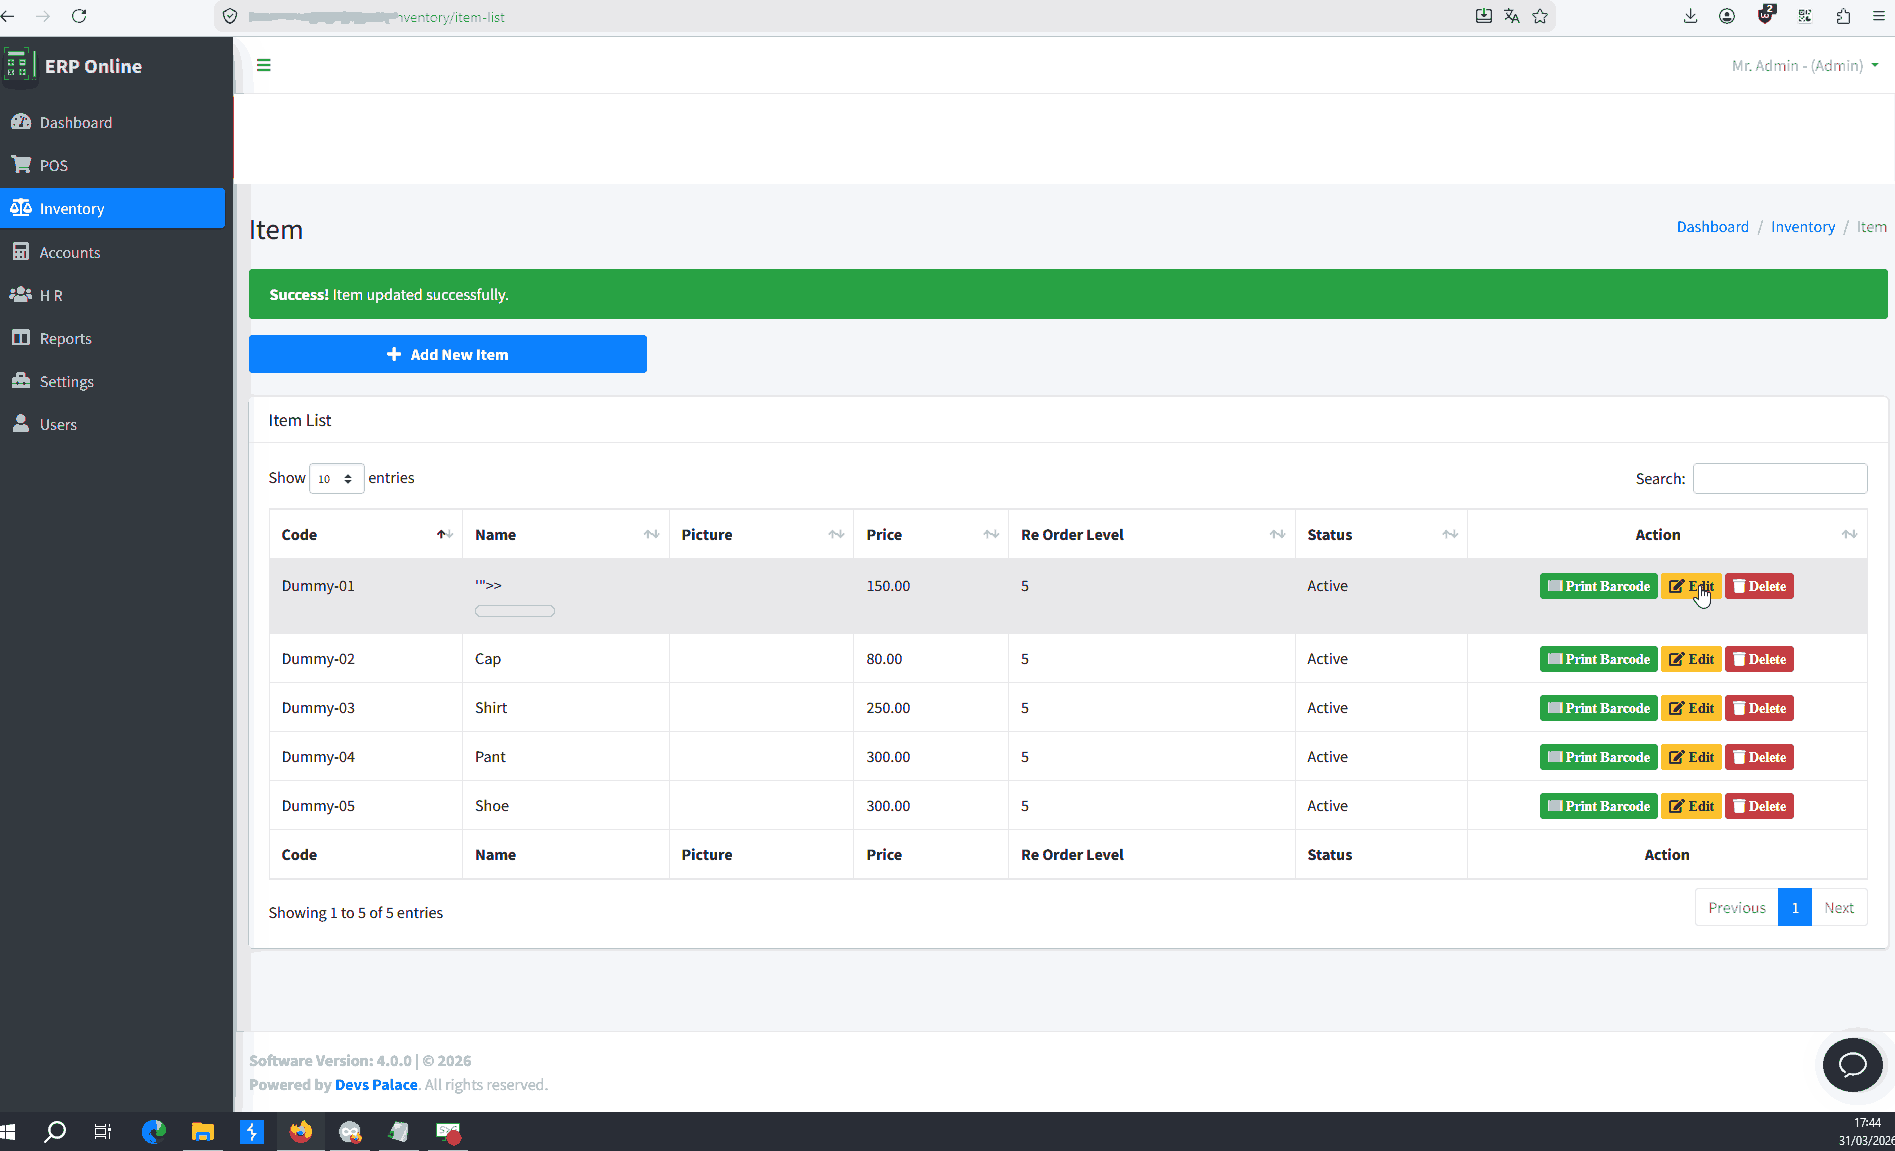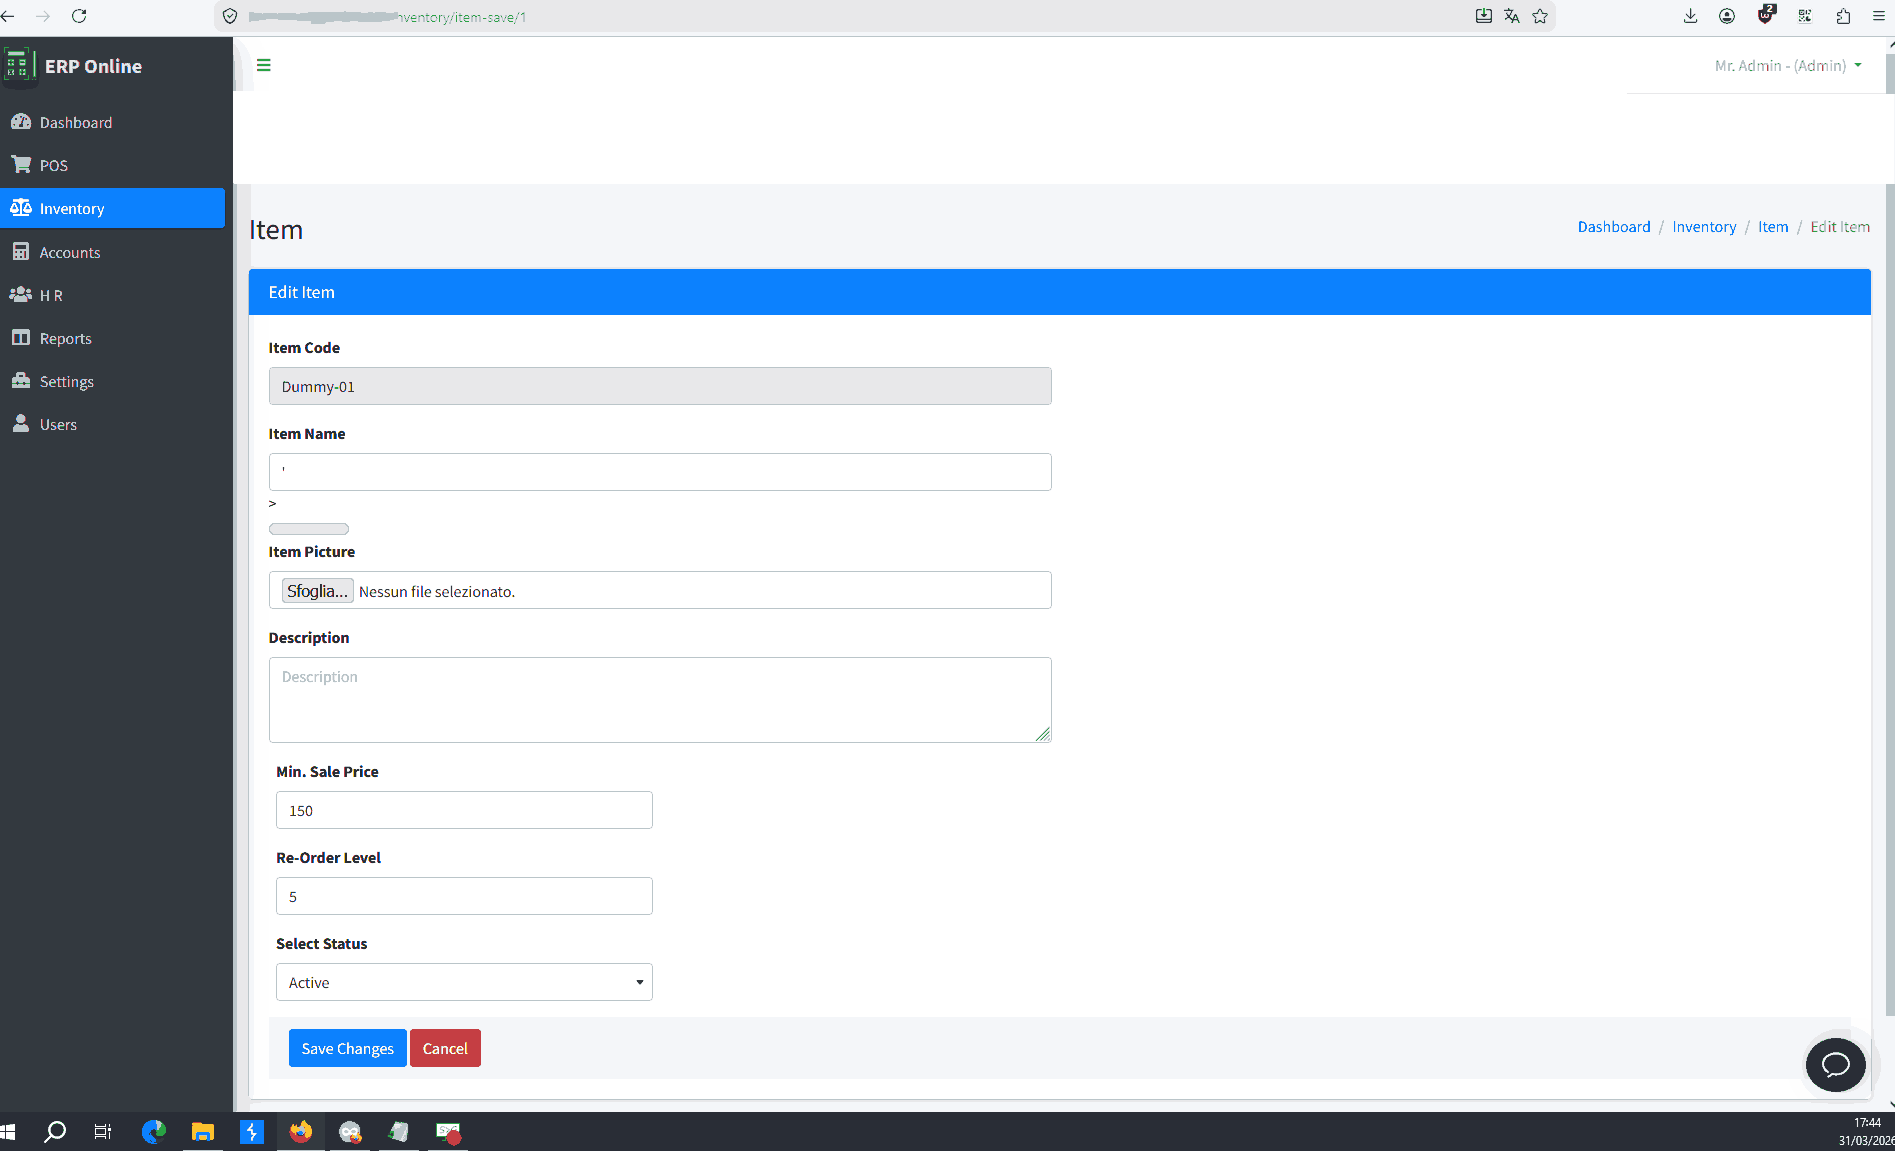
A cross-site scripting (XSS) vulnerability exists in Devs Palace ERP Online up to version 4.0.0. The flaw is located within the /inventory/purchase_return_save file, where improper input neutralization allows for the injection of malicious web scripts. An attacker with high privileges can exploit this remotely by submitting crafted data that is later rendered in a victim's browser. Successful exploitation requires user interaction (UI:R) and can lead to unauthorized manipulation of web content. A public proof-of-concept (PoC) exists, but the vendor has not responded to disclosure attempts.
Affected products
- Devs Palace ERP Online up to 4.0.0
Timeline
- 2026-05-10: disclosed: Initial public disclosure via VulDB and NVD
- 2026-05-10: advisory
- 2026-05-11: other: CISA-ADP SSVC assessment performed