CVE-2024-26152: Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config

CVE-2024-26152 · Severity: low · CVSS 3.1 · Published 2024-02-22

### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.

### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.

### PoC

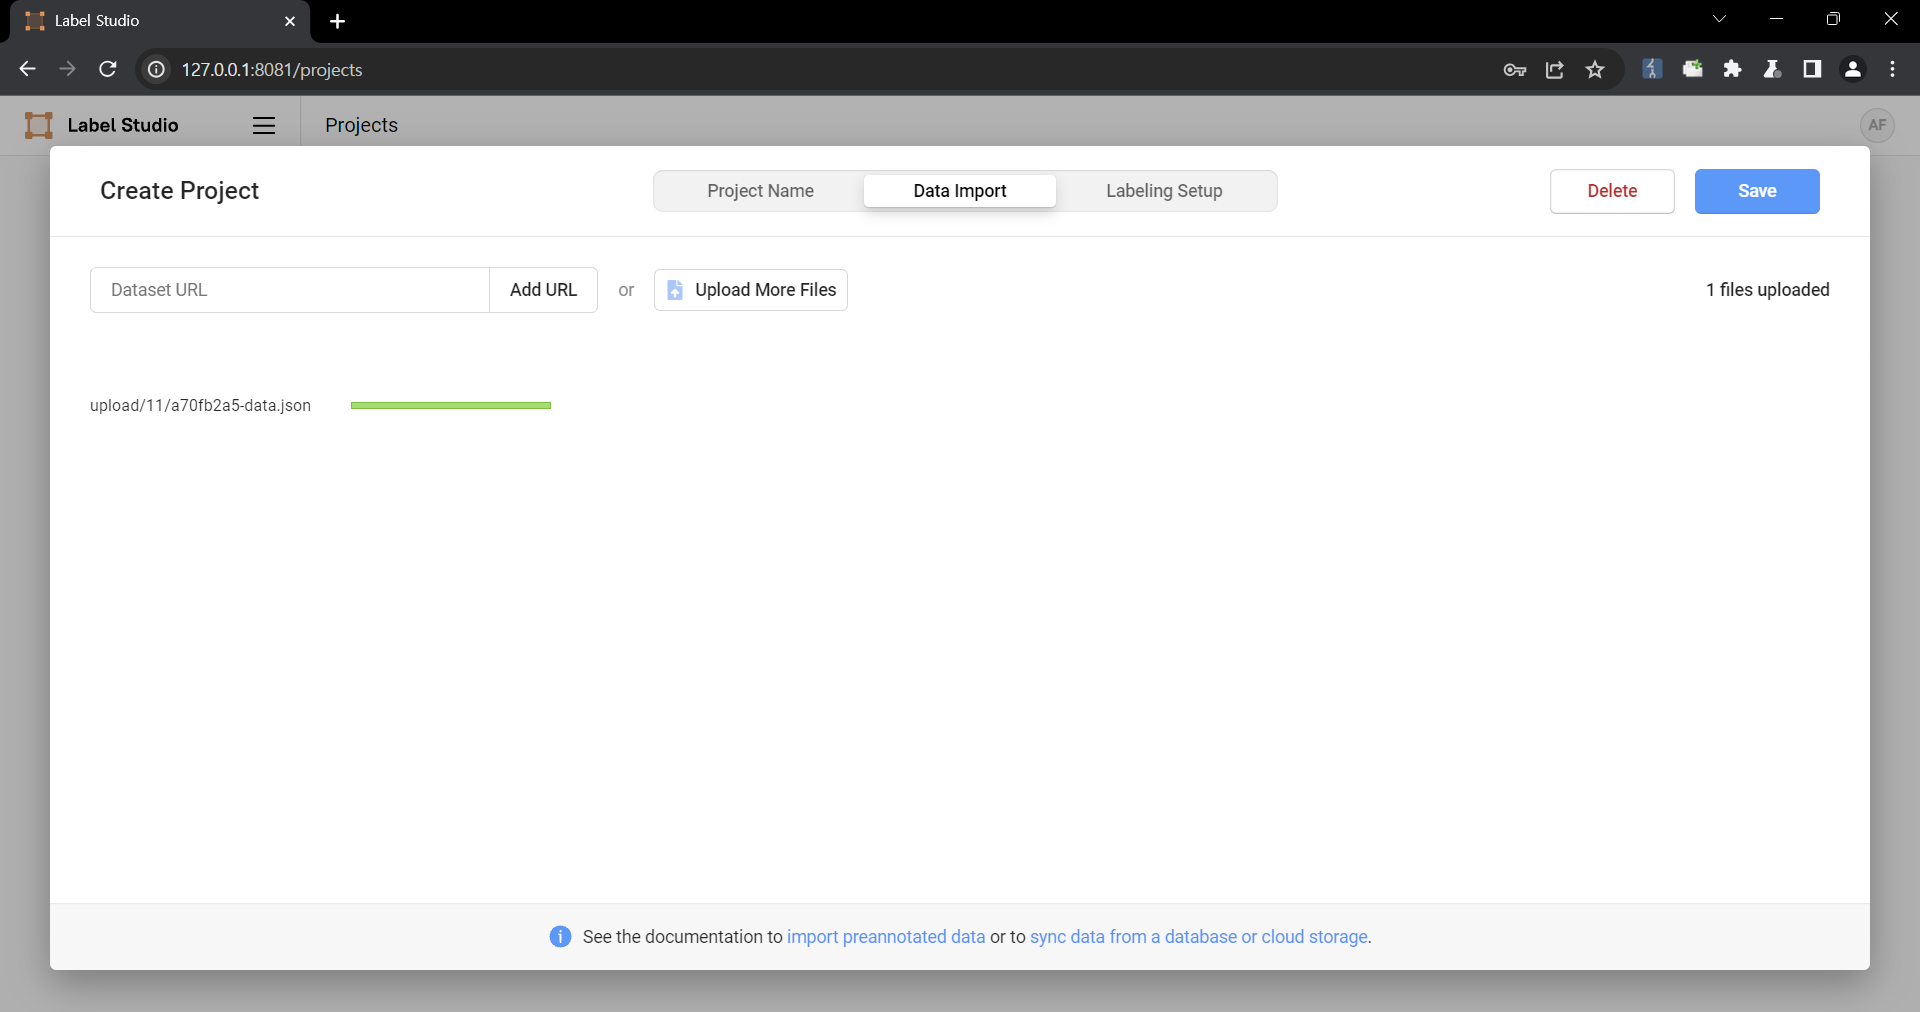
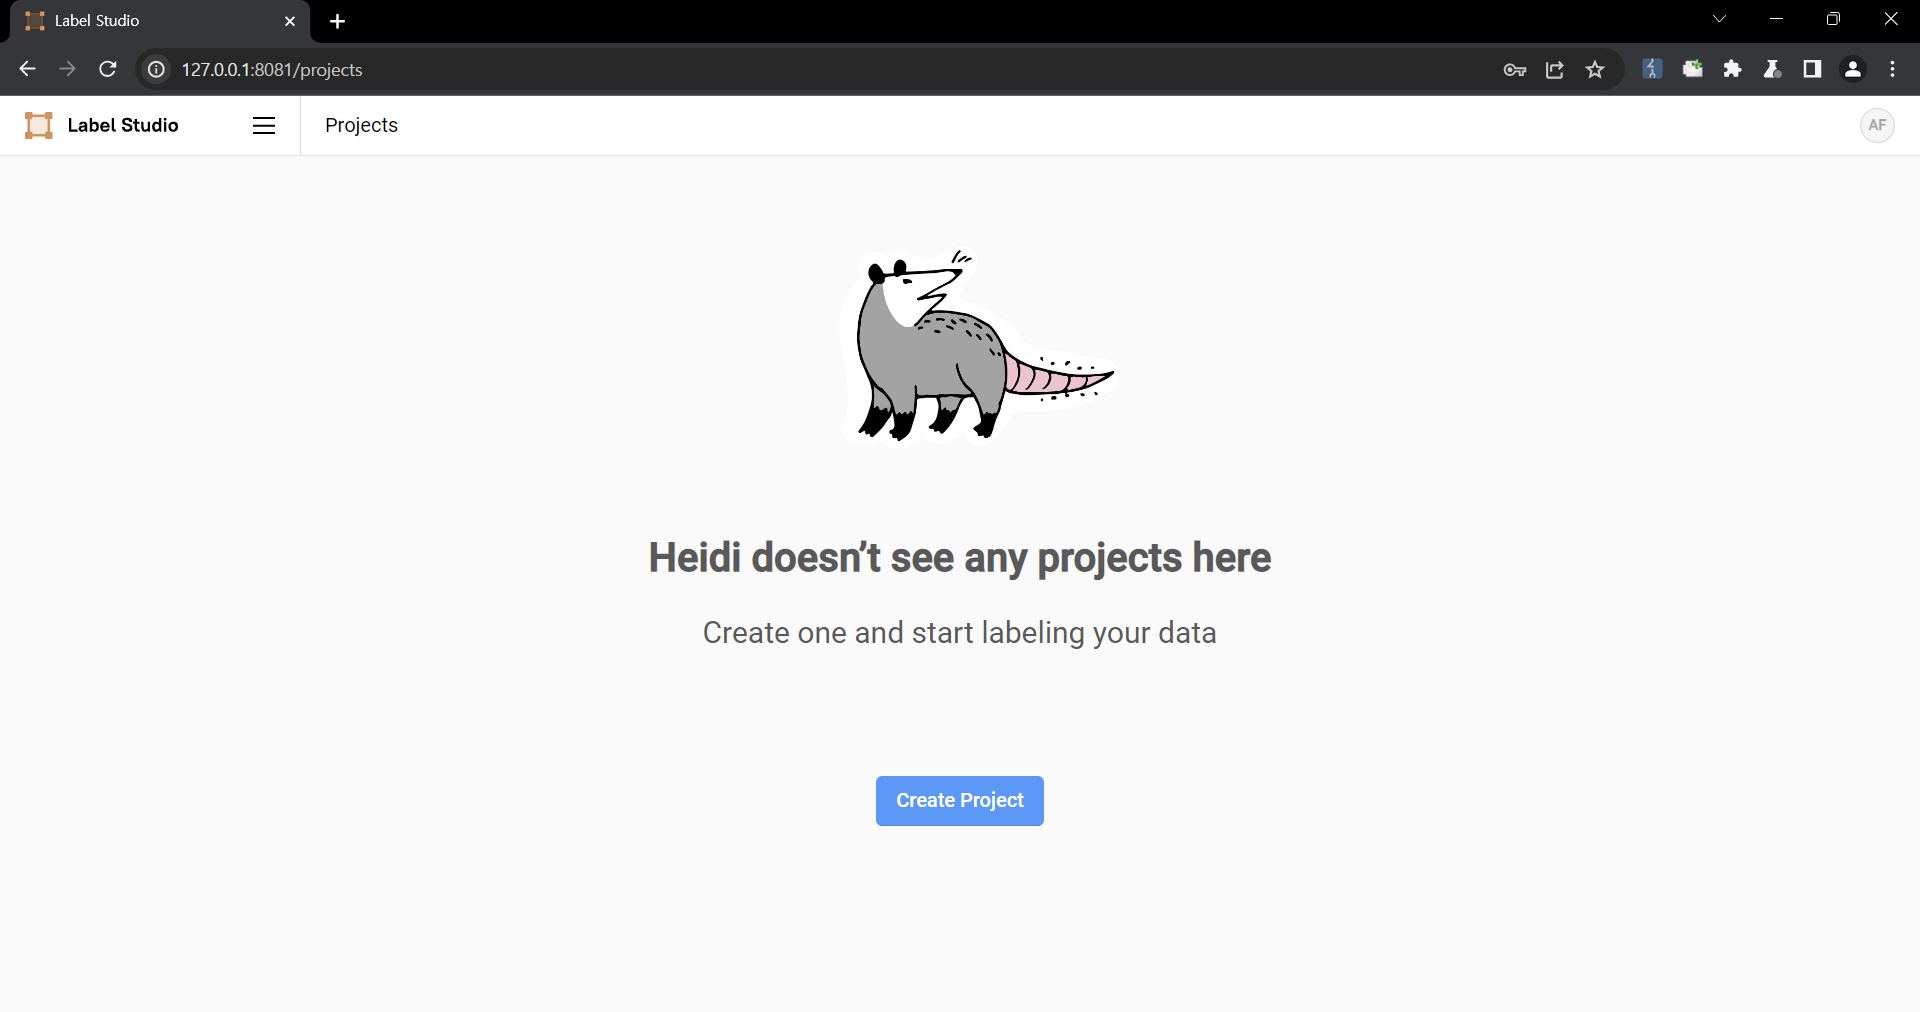
1. Create a project. ![Create a project](https://github.com/HumanSignal/label-studio/assets/3943358/9b1536ad-feac-4238-a1bd-ca9b1b798673)
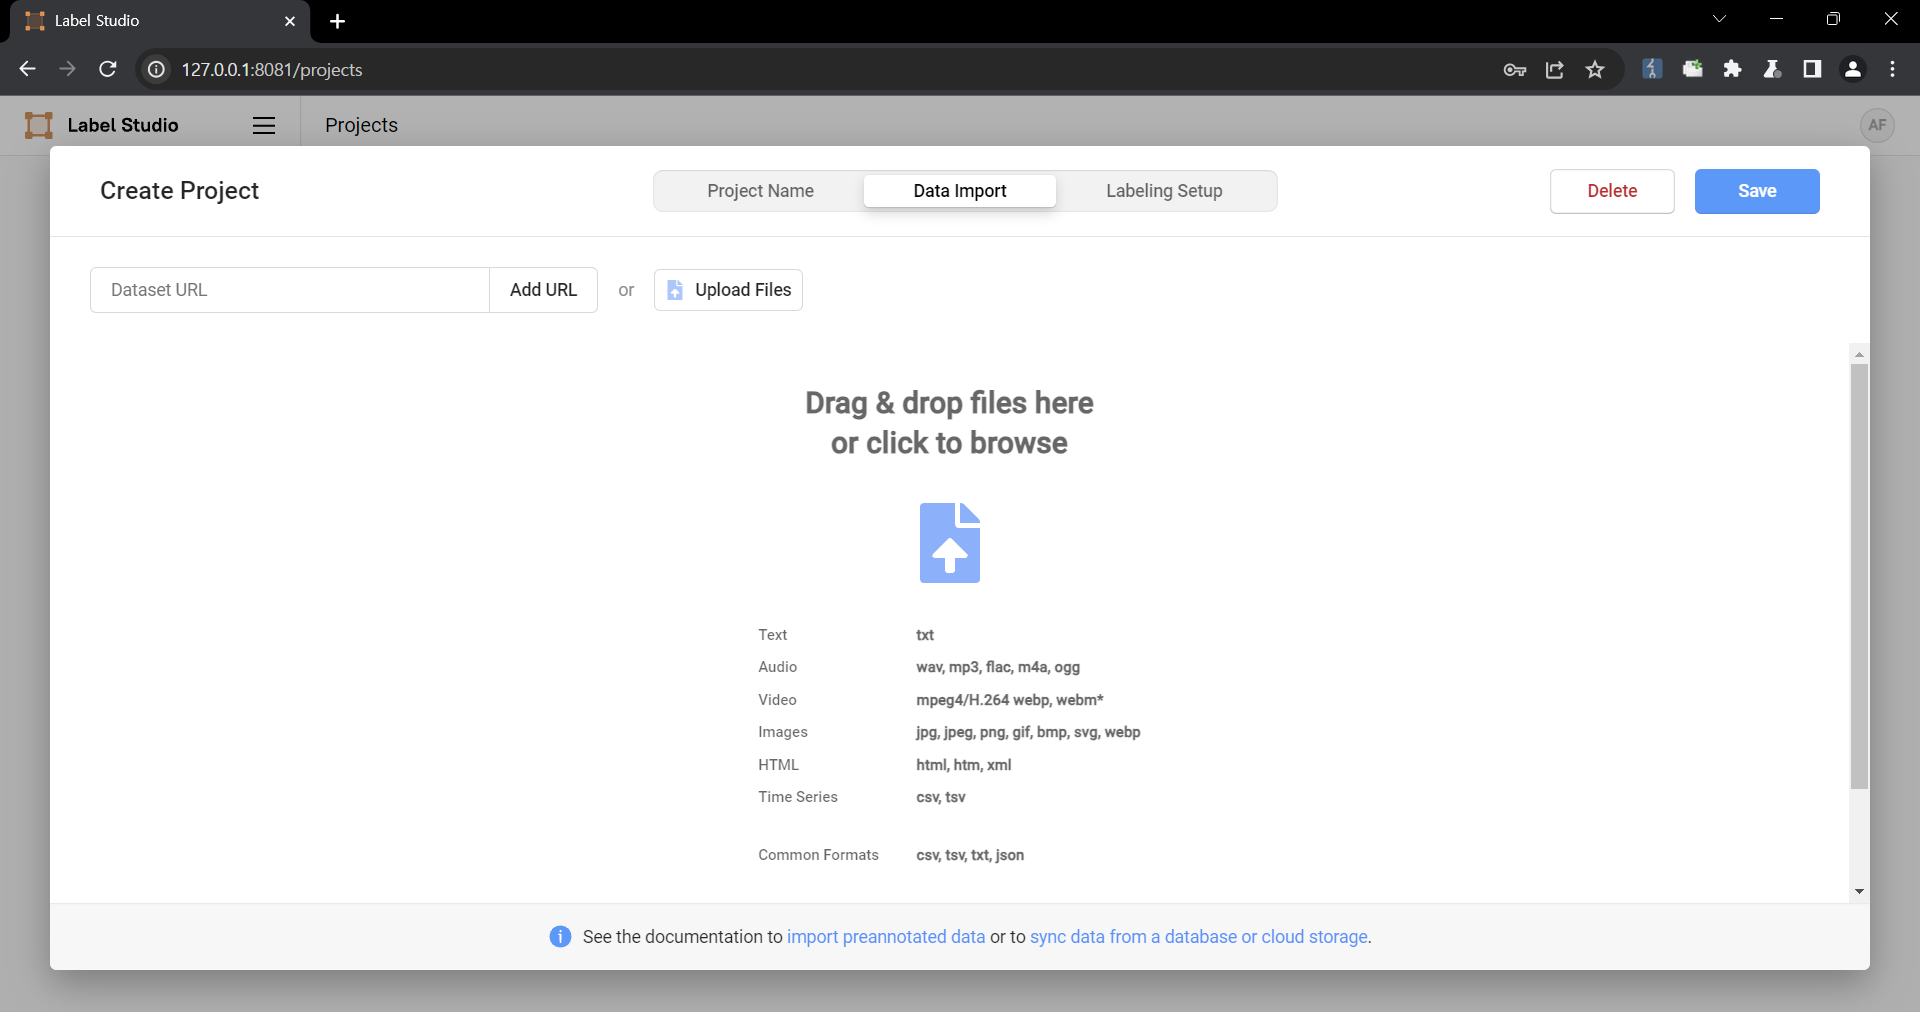
2. Upload a file containing the payload using the "Upload Files" function. ![2 Upload a file containing the payload using the Upload Files function](https://github.com/HumanSignal/label-studio/assets/3943358/26bb7af1-1cd2-408f-9adf-61e31a5b7328) ![3 complete](https://github.com/HumanSignal/label-studio/assets/3943358/f2f62774-1fa6-4456-9e6f-8fa1ca0a2d2e)
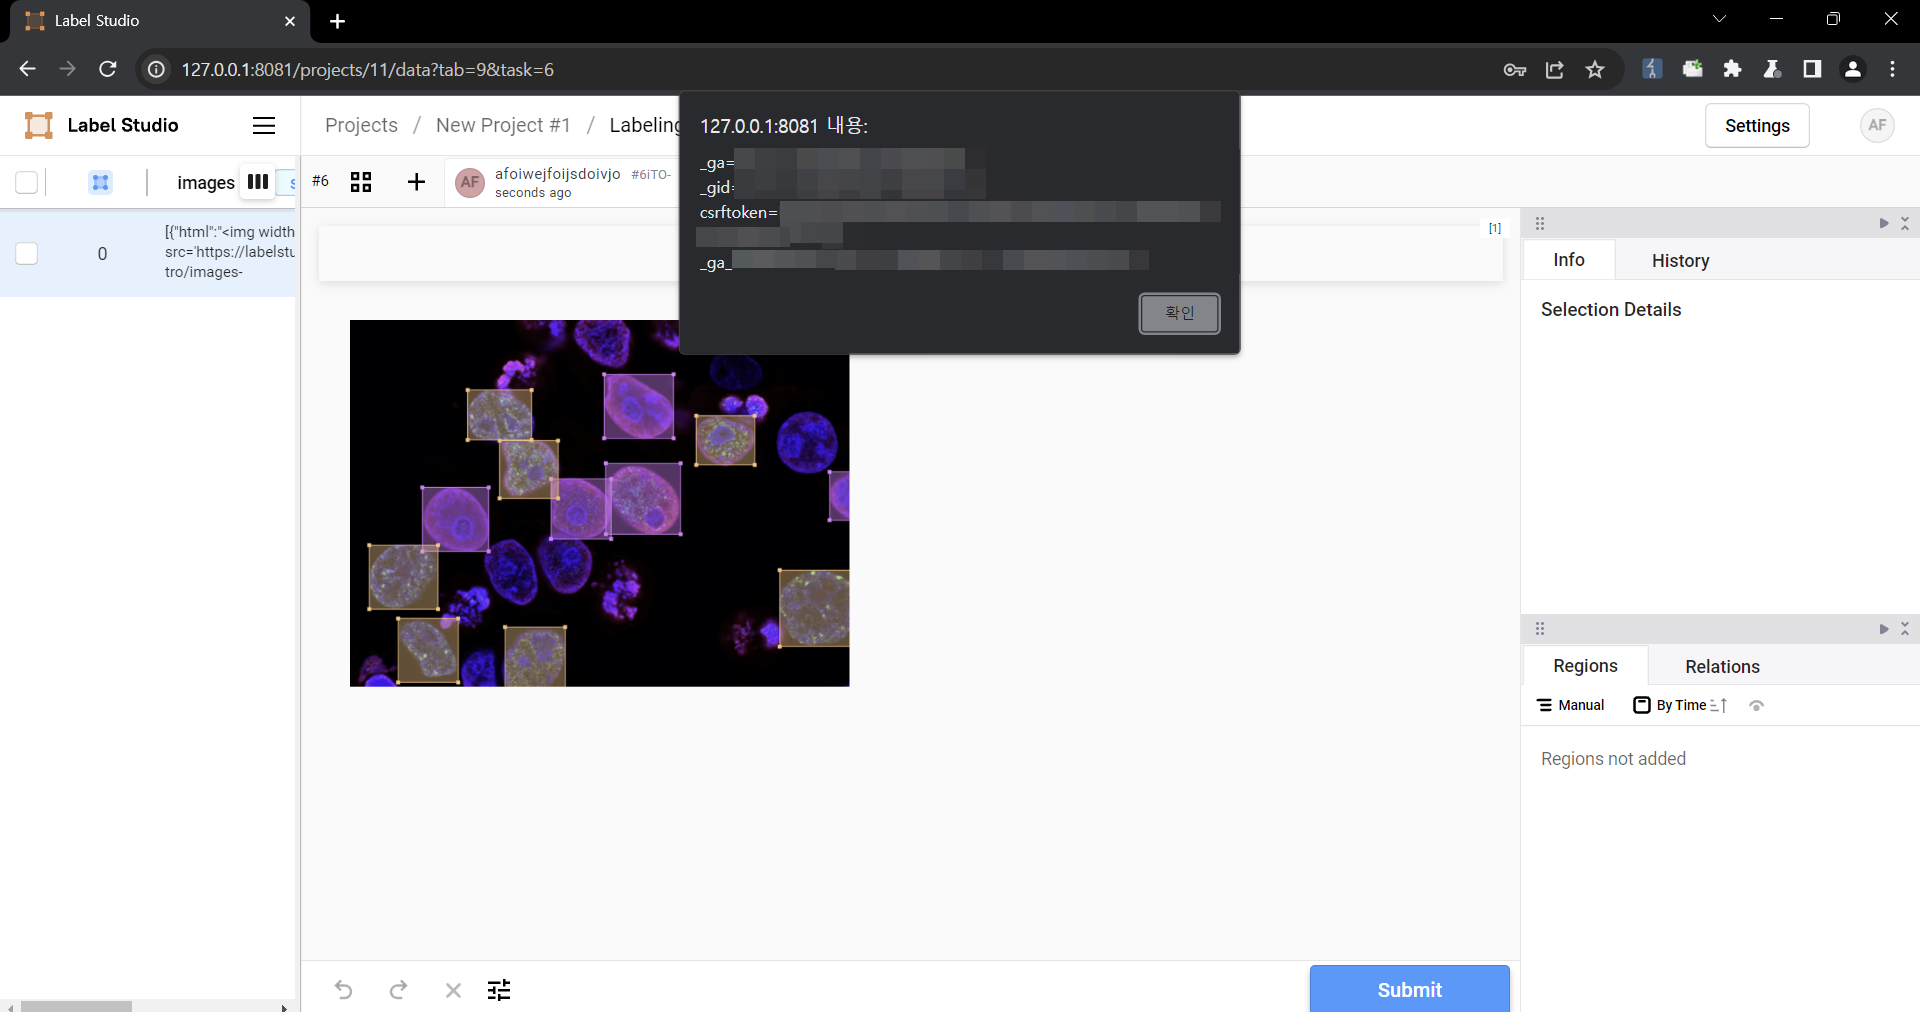
The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ```

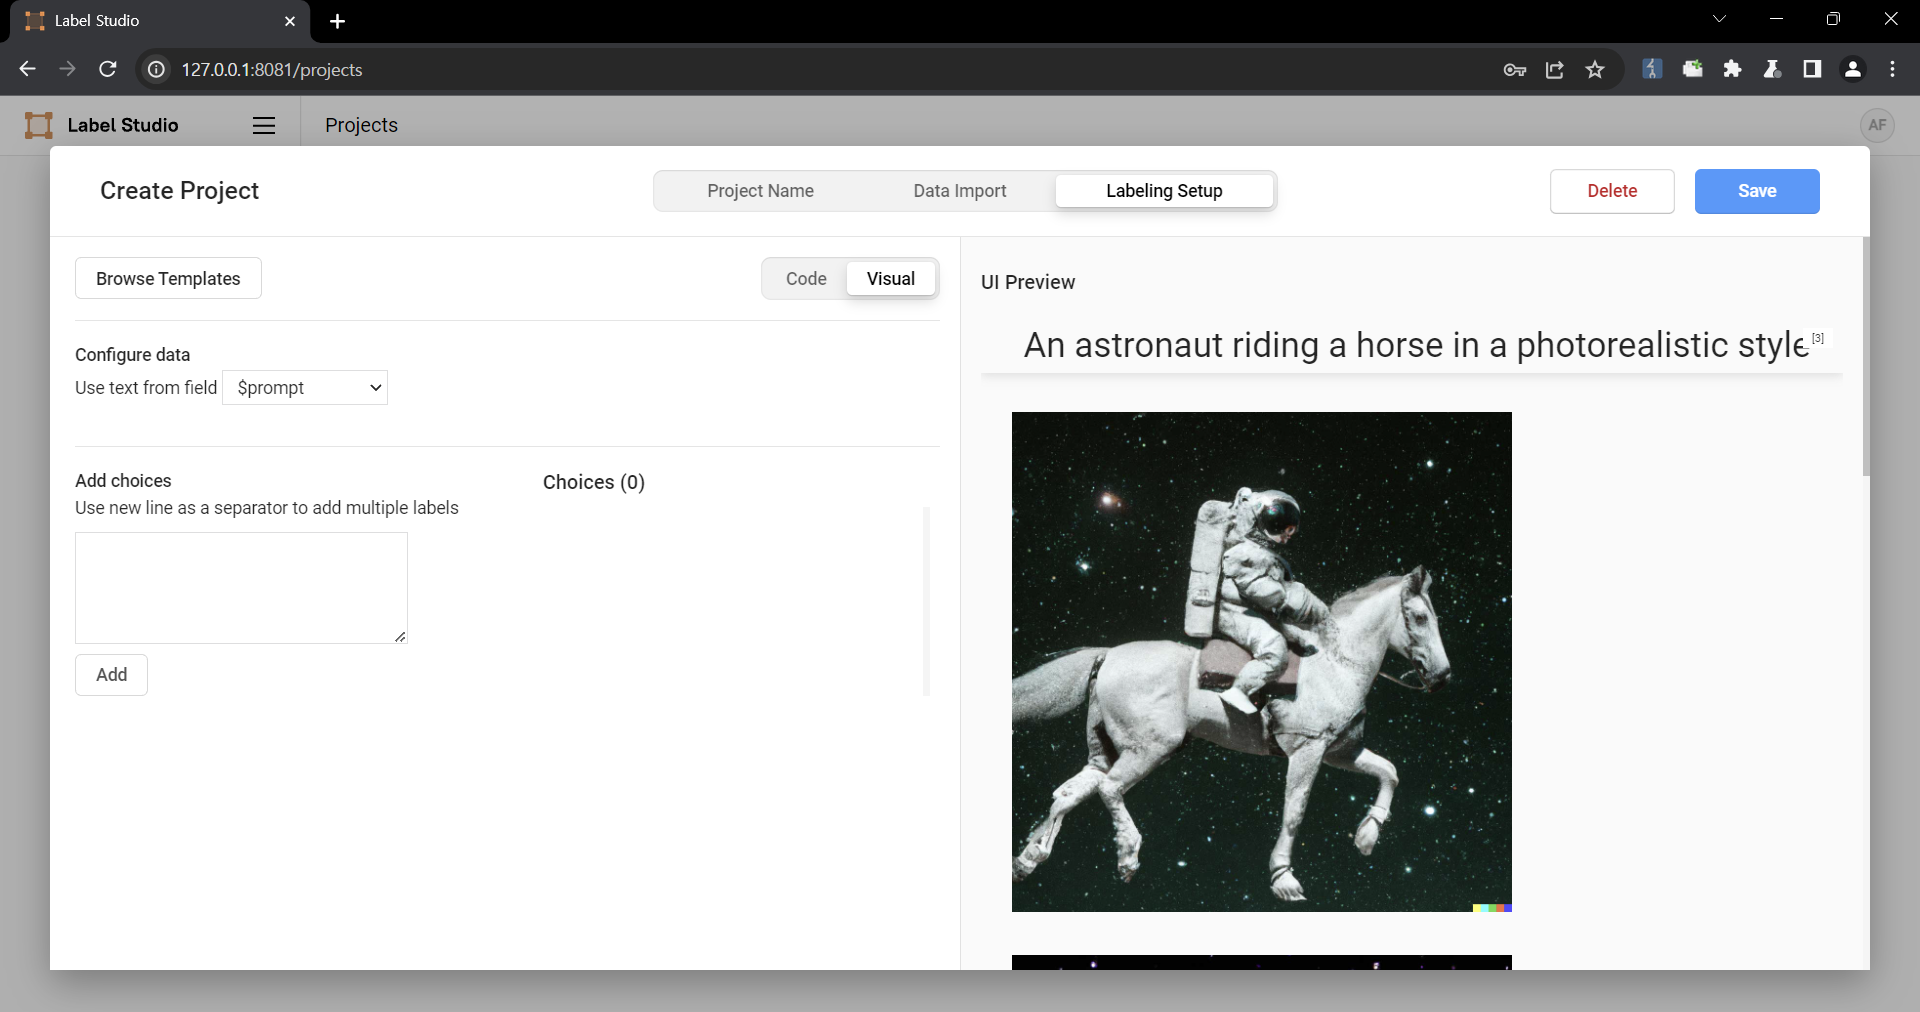
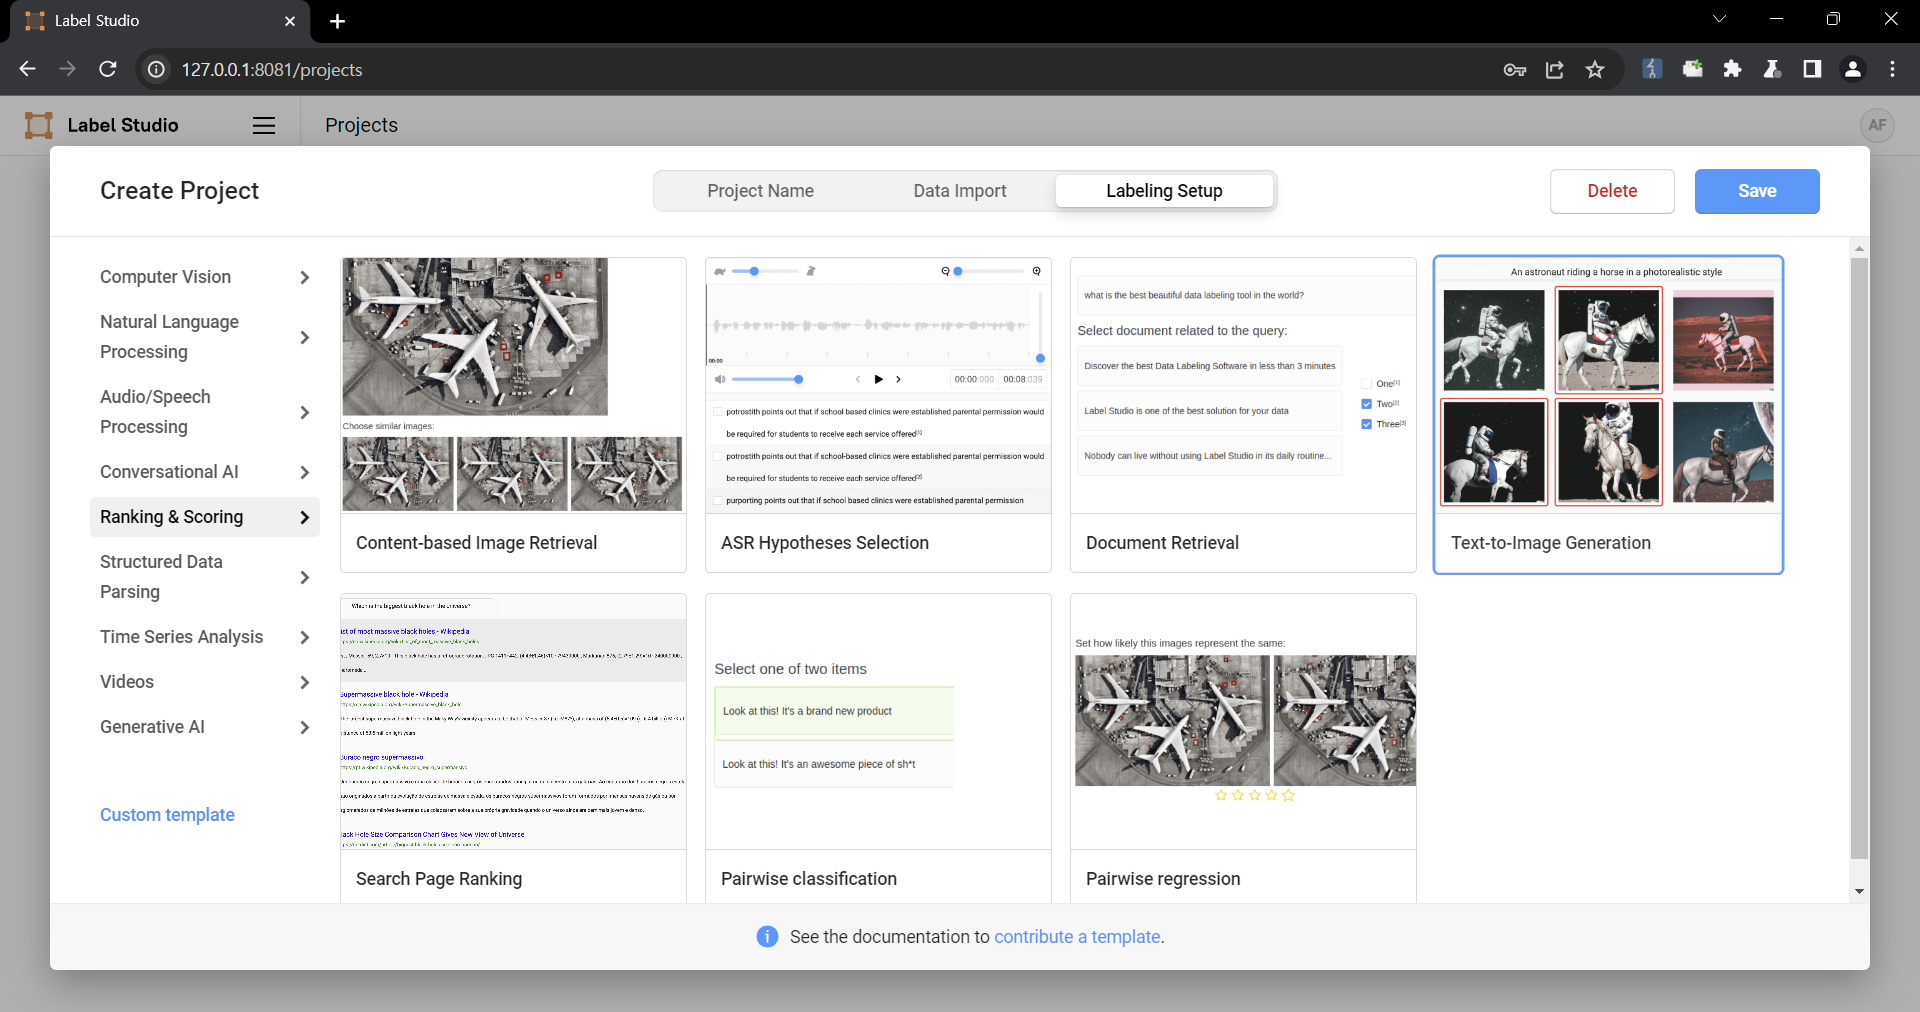
3. Select the text-to-image generation labeling template of Ranking and scoring ![3 Select the text-to-image generation labelling template for Ranking and scoring](https://github.com/HumanSignal/label-studio/assets/3943358/f227f49c-a718-4738-bc2a-807da4f97155) ![5 save](https://github.com/HumanSignal/label-studio/assets/3943358/9b529f8a-8e99-4bb0-bdf6-bb7a95c9b75d)
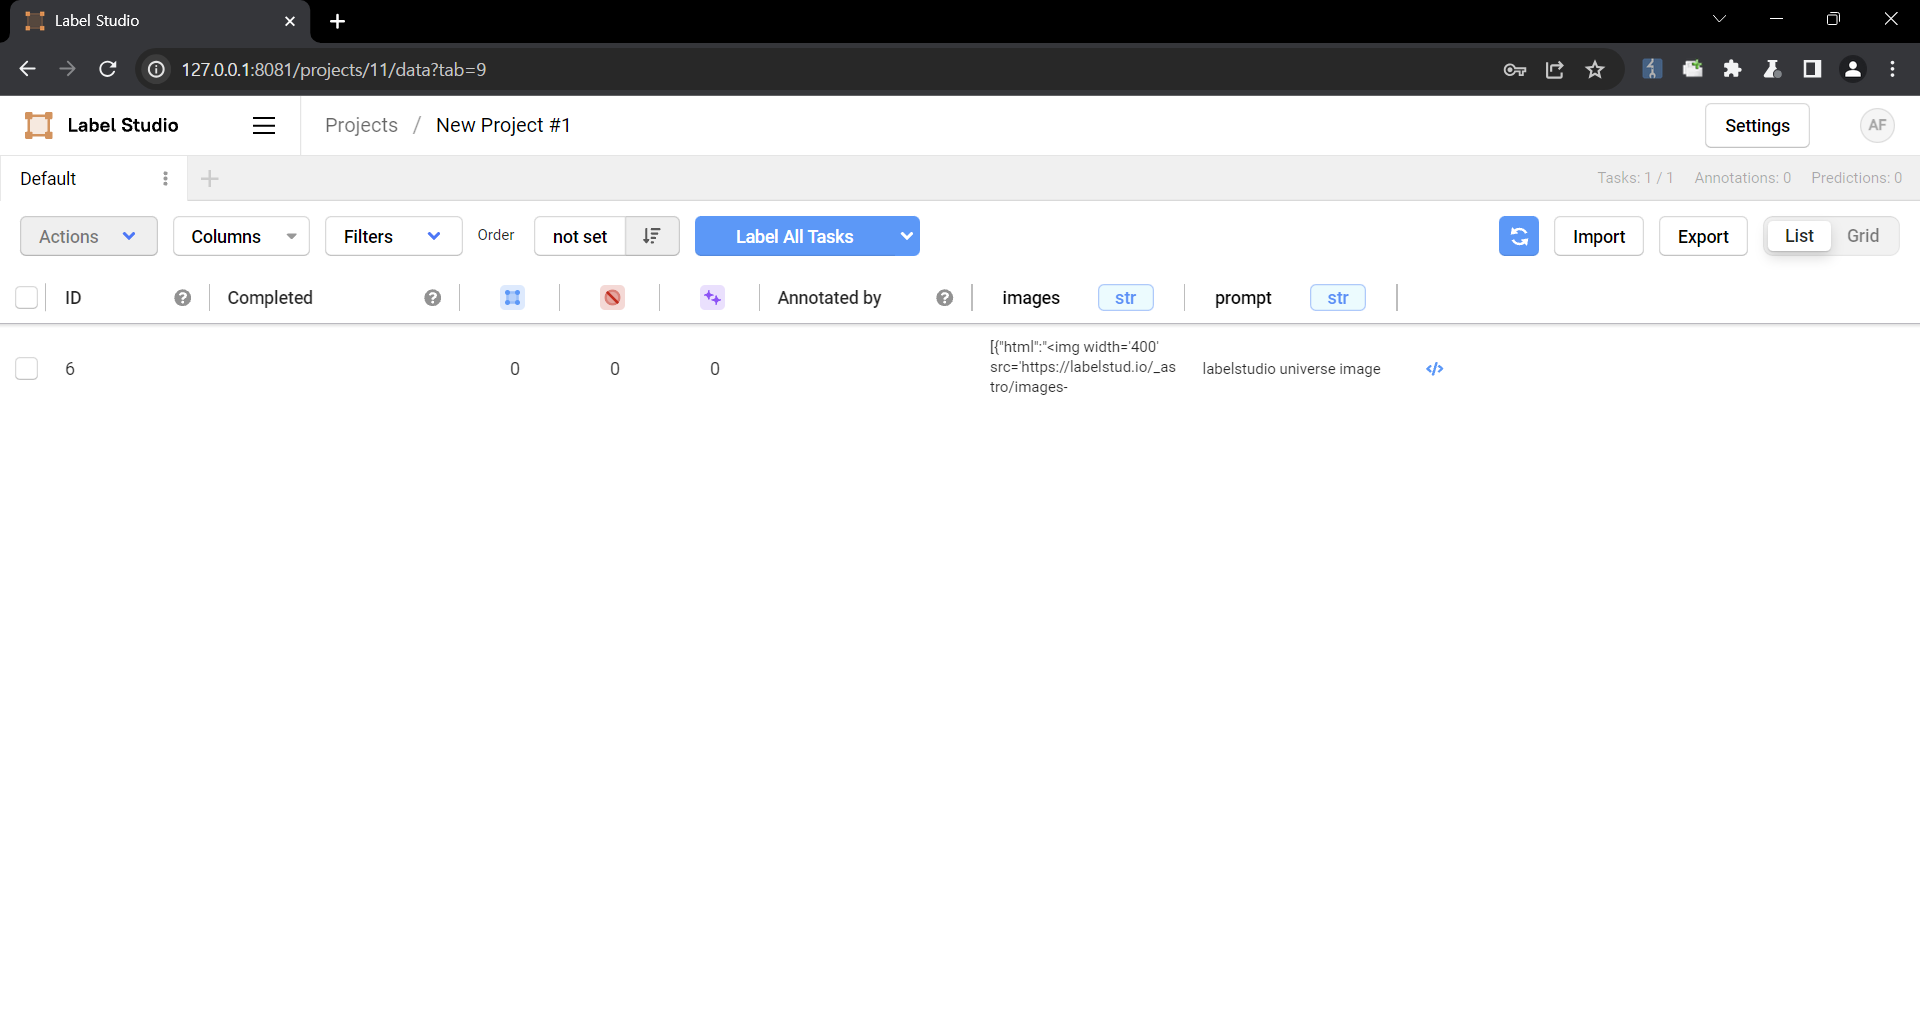
4. Select a task ![4 Select a task](https://github.com/HumanSignal/label-studio/assets/3943358/71856b7a-2b1f-44ea-99ab-fc48bc20caa7)

5. Check that the script is running ![5 Check that the script is running](https://github.com/HumanSignal/label-studio/assets/3943358/e396ae7b-a591-4db7-afe9-5bab30b48cb9)

### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.

Technologies: label-studio (PyPI). Vendors: PyPI.

Quick answers

Is CVE-2024-26152 exploited in the wild?
No. Junglewise Threat Intelligence has no report of CVE-2024-26152 being exploited in the wild.
How severe is CVE-2024-26152?
Low severity, with a CVSS score of 3.1, published 22 February 2024.
Which products and versions are affected?
label-studio (PyPI) ECOSYSTEM:introduced=0,fixed=1.11.0, GIT:introduced=0,fixed=5df9ae3828b98652e9fa290a19f4deedf51ef6c8|ECOSYSTEM:introduced=0,fixed=1.11.0.
Is there a fix for CVE-2024-26152?
Yes. label-studio (PyPI): upgrade to 1.11.0 or later. Junglewise finds every place you run it, drafts the upgrade and applies it once you approve.
Am I affected by CVE-2024-26152?
Check whether you run label-studio (PyPI) at an affected version. Junglewise does that check for you around the clock: connect your code, cloud and domains, and it matches new vulnerabilities like this one against what you actually run and tells you when one reaches you.

How to fix

  • label-studio (PyPI): upgrade to 1.11.0 or later
    pip install "label-studio>=1.11.0"

Affected products

  • label-studio (PyPI) ECOSYSTEM:introduced=0,fixed=1.11.0, GIT:introduced=0,fixed=5df9ae3828b98652e9fa290a19f4deedf51ef6c8|ECOSYSTEM:introduced=0,fixed=1.11.0

Identifiers

  • CVE-2024-26152
  • GHSA-6xv9-957j-qfhg
  • PYSEC-2024-249

This page as Markdown. Free to reuse under CC BY 4.0 with a link back.